

The DOI matches its DataCite record; none of the 2 sources its claims cite is checked for support yet.
Malicious GenAI Chrome Extensions: Unpacking Data Exfiltration and Malicious Behaviours
Open accessAbstract
The rapid proliferation of AI and GenAI tools has extended to the Chrome Web Store. Cybercriminals are exploiting this trend, deploying malicious Chrome extensions posing as AI tools or impersonating popular GenAI models to target users. These extensions often appear legitimate while secretly exfiltrating sensitive data or redirecting users web traffic to attacker-controlled domains. To examine the impact of this trend on the browser extension ecosystem, we curated a dataset of 5,551 AI-themed extensions released over a nine-month period to the Chrome Web Store. Using a multi-signal detection methodology that combines manifest analysis, domain reputation, and runtime network behavior, supplemented with human review, we identified 154 previously undetected malicious Chrome extensions. Together with extensions known from public threat research disclosures, this resulted in a final set of 341 malicious extensions for analysis. Of these, 29 were GenAI-related, forming the focus of our in-depth analysis and disclosure. We deconstruct representative GenAI cases, including Supersonic AI, DeepSeek AI | Free AI Assistant, and Perplexity Search, to illustrate attacker techniques such as Adversary-in-the-Browser, impersonation, bait-and-switch updates, query hijacking, and redirection. Our findings show that threat actors are leveraging GenAI trends and exploiting browser extension APIs and settings for malicious purposes. This demonstrates that the browser extension threat landscape is directly evolving alongside the rapid adoption of GenAI technologies.
Overview
CoChat Summary
TL;DR
The paper curates 5,551 AI-themed Chrome extensions released between 1 January and 15 September 2025 and identifies 154 previously undetected malicious extensions, which together with 187 publicly disclosed malicious extensions yields a final set of 341 malicious extensions. It focuses on 29 GenAI-themed malicious extensions to show how attackers use impersonation, bait-and-switch updates, query/prompt hijacking, data exfiltration, and malicious redirection.
Key findings
- Of 5,551 AI-themed extensions, the authors detected 154 previously undetected malicious extensions; combined with 187 from public disclosures, this produced 341 malicious extensions, of which 29 were GenAI-themed and analyzed in depth.
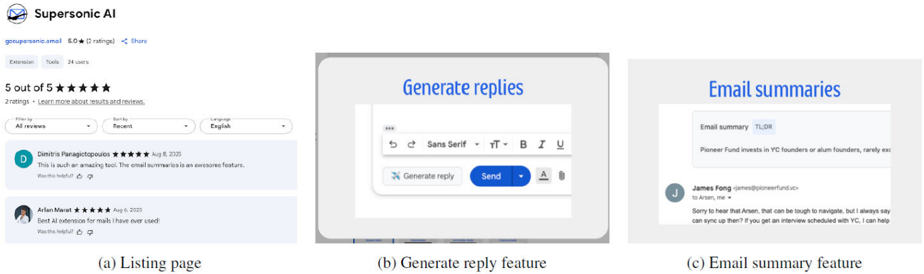
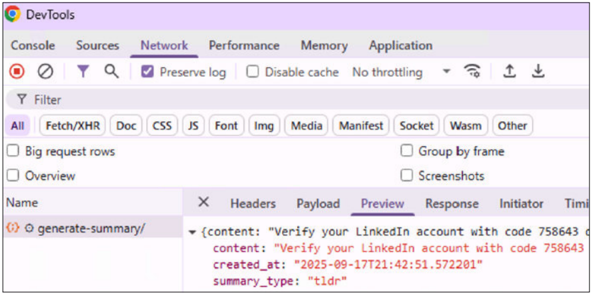
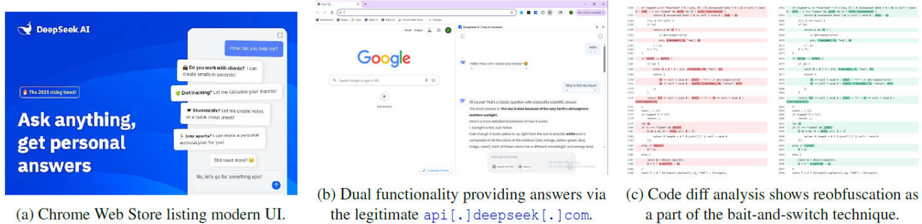
- GenAI-themed cases demonstrated adversary-in-the-browser, impersonation, dual functionality, bait-and-switch updates, query hijacking, prompt hijacking, and redirection. For example, Supersonic AI exfiltrated full email content and a LinkedIn verification code “758643” via POST requests to `api[.]gosupersonic[.]email`; DeepSeek AI | Free AI Assistant impersonated `deepseek[.]com`, sent GET requests to `api[.]glimmerbloop[.]top` (11 VirusTotal detections), and moved from benign versions 0.0.1/0.0.2 to malicious version 3.0.1.
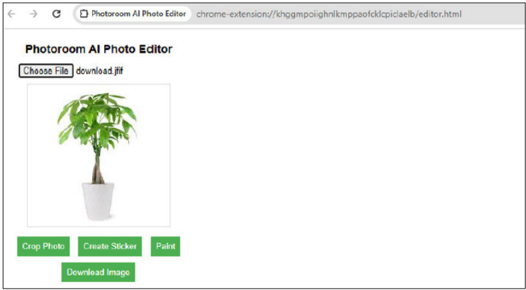
- Malicious redirection cases included Photoroom AI Photo Editor, which abused `chrome.runtime.onInstalled` to redirect users through an iframe from `photor-extens[.]uno` and monetized via affiliate fraud with `utm_medium=pa`; the authors found this was part of a campaign involving at least 68 similar malicious extensions.
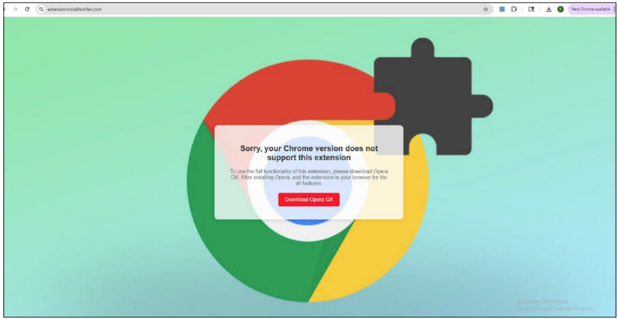
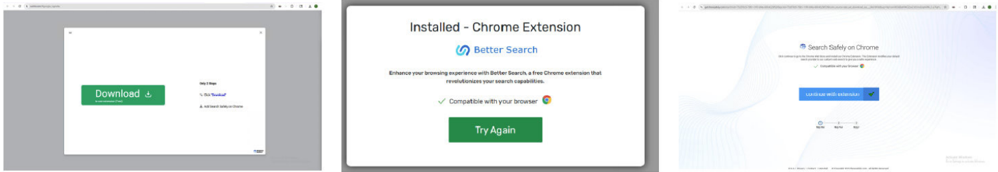
- A PUP delivery case, The Pokemon Cursor ★ Custom Cursor for Chrome™, redirected users from `owhit[.]com` to `get[.]theresafely[.]com` promoting the Better Search extension; this was part of a larger campaign involving 75 malicious extensions.
Methods
- The authors compiled a targeted dataset of 5,551 unique Chrome extensions released between 1 January and 15 September 2025 that included AI-related keywords in their name or description, plus 187 confirmed malicious extensions from public disclosures.
- They applied a multi-signal detection methodology combining extension metadata analysis, static code analysis, and runtime behavioural/network intelligence, supplemented with manual human review, to identify 154 new malicious extensions.
- The final ground-truth dataset of 341 malicious extensions was analyzed, with 29 GenAI-themed extensions selected for detailed case studies using sandbox network logs, version-by-version differential analysis, and domain reputation checks.
Limitations
- The paper states that its current triaging process relies on manual correlation and expert human review, and that future work plans to explore similar trends on other browser platforms such as Edge and Firefox.
- Evident from the text: the dataset is limited to Chrome Web Store extensions with AI-related keywords in their name or description over a specific nine-month period, so findings may not generalize to other browsers, non-AI-themed extensions, or other time periods.
- Evident from the text: the in-depth GenAI analysis focuses on 29 extensions, and some included case studies (e.g., Pokemon Cursor) are not GenAI-themed, so the case-study findings may not represent all malicious browser extensions.
Model-written summary. Check it against the paper before relying on it.
Integrity signals
Registry
Cites
Statistics
Figures
Verification
Claims the paper makes
0 Valid · 1 Not valid · 3 Not checked · 89 Own results and interpretations
A result the paper states — it cites no source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“Despite the Chrome Web Store's strict policies, the extension remains available.”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > Attack flow 2: passive data exfiltration without direct interaction
plain- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: unclear — It is unclear whether the paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Rests on an assumption not shown here.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“A more notable attack flow involves data exfiltration that occurs without any direct user interaction with the extension's features.”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > Attack flow 2: passive data exfiltration without direct interaction
plainSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“This script programmatically accesses the content of the entire email thread, including the sensitive message.”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > Attack flow 1: active data exfiltration via feature interaction:
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“Dynamic analysis captured this behaviour, logging a POST request to hxxps://api[.]gosupersonic[.]email/api/generate-reply/. The request body contained the full, unredacted content of the confidential email, confirming the exfiltration of sensitive data.”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > 2. Message passing:
boostedstates a causeSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“Analysis of its associated domain (api[.]gosupersonic[.]email)on VirusTotal returned a detection rate of 1/97, reflecting limited coverage by existing blocklists.”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > Attack flow 2: passive data exfiltration without direct interaction
plainSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: unclear — It is unclear whether the paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
48 more claims
Create a free account to see all 93 claims and every source verdict.
- Probably not a substantial claim. 11
- It may state two separate claims as one. 30
- The quote only partly states this claim. 1
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
Each contradiction between two passages listed here was confirmed by an independent check.
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > VIRUS BULLETIN CONFERENCE SEPTEMBER 2025
“low reputation by third-party sources such as VirusTotal [29] or internal (Palo Alto Networks) intelligence.”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > References
“29. DomainTools Investigations. Hidden threats of dualfunction malware found in chrome extensions. May 2025.”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > VIRUS BULLETIN CONFERENCE SEPTEMBER 2025
“This finding was publicly reported through Palo Alto Networks' Unit 42 channel [34].”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > References
“34. Unit 42 Intel. Prompt hijacker ai-themed chrome. 2025. https://x.com/Unit42_Intel/status/1971252186030981140.”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > 5.1.2 Impersonation, dual functionality, and bait-and-switch
“Initial intelligence from DomainTools [30] in May 2025 identifies this family of extensions”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > References
“30. Tuckner, J. Secure annex blog. 2025. https://secureannex.com/blog/searching-for-something-unknow/.”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > 2. Redirect via button click event:
“This was publicly reported via Palo Alto Networks' Unit 42 channel [37].”
§ MALICIOUS GENAI CHROME EXTENSIONS: UNPACKING DATA EXFILTRATION AND MALICIOUS BEHAVIOURS > References
“36. Unit 42 Intel. Campaign of malicious extensions delivering pups. 2025. https://x.com/Unit42_Intel/ status/1957564228081988038.”
Citations
Cites
Still being checked.
Research works printed but not linked: 10
- Fass, A.; Konwinski, A.; Squarcina, M.; Lindorfer, M. What is in the Chrome Web Store? investigating Security- Noteworthy Browser Extensions. In the ACM Conference on Data and Application Security and Privacy (CODASPY), 2024.
- Kapravelos, A.; Shoshitaishvili, Y.; Athanasopoulos, E.; Kruegel, C.; Vigna, G. Hulk: Eliciting malicious behavior in browser extensions. In USENIX Security Symposium (USENIX Security), 2014.
- Starov, O.; Nikiforakis, N. Xhound: Quantifying the fingerprintability of browser extensions. In 2017 IEEE Symposium on Security and Privacy (SP), pages 941-956, 2017.
- Starov, O.; Nikiforakis, N. Extended tracking powers: Measuring the privacy diffusion enabled by browser extensions. In Proceedings of the 26th International Conference on World Wide Web (WWW '17), pages 1481- 1490. International World Wide Web Conferences Steering Committee, 2017.
- Xie, Q.; Kasi Murali, M. V.; Pearce, P.; Li, F. Arcanum: Detecting and evaluating the privacy risks of browser extensions on web pages and web content. In 33rd USENIX Security Symposium (USENIX Security 24), pages 4607-4624, Philadelphia, PA, August 2024. USENIX Association.
- Pantelaios, N.; Nikiforakis, N.; Kapravelos, A. You've changed: Detecting malicious browser extensions through their update deltas. In the ACM SIGSAC Conference on Computer and Communications Security (CCS), 2020.
- Fass, A.; Somé, D. F.; Backes, M.; Stock, B. Doublex: Statically detecting vulnerable data flows in browser extensions at scale. In Proceedings of the 2021 ACM SIGSAC Conference on Computer and Communications Security (CCS), pages 3092-3109. ACM, 2021.
- Aggarwal, A.; D'Angelo, G.; Squarcina, M.; Lindorfer, M.; Eubeler, J.; Egele, M.; Anderle, B.; Huber, P.; Kruegel, C.; Vigna, G. I spy with my little eye: Analysis and detection of spying browser extensions. In IEEE European Symposium on Security and Privacy (EuroS&P), 2018.
- Rydecki, J.; Tong, J.; Zheng, J. Detecting malicious browser extensions by combining machine learning and feature engineering. In ITNG 2023: 20th International Conference on Information Technology -New Generations, volume 1445 of Advances in Intelligent Systems and Computing, pages 105-113. Springer, Cham, 2023.
- Karuppaia, R. A.; Zonta, T.; Sathiyanarayanan, M. A holistic review on detection of malicious browser extensions and links using deep learning. In 2024 IEEE 3rd International Conference on AI in Cybersecurity (ICAIC), pages 1-6. IEEE, 2024.
Cited by
From Storage to Steering: Memory Control Flow Attacks on LLM Agents
Xu, Z., Zhu, X., Yao, Y., Xue, M., & Song, Y. (2026) · arXiv · doi:10.48550/arxiv.2603.15125
Metadata
- Authors
- Seetharam, S. B., Nabeel, M., & Melicher, W.
- Affiliations
- Palo Alto Networks (United States) (US)
- Venue
- arXiv
- Publisher
- arXiv
- Published
- 2025
- ISSN
- 2331-8422 (ISSN-L)
- arXiv
- 2512.10029
- OpenAlex
- W4417293751
- Semantic Scholar
- facd1fa16f02f7dbe25503d4ef30c66ba8d0eae8
- Cited by
- 1
- References
- 0
- Citations by year
- 2026: 1
- Type
- posted content
- Language
- en
- Open access
- green
- arxiv.org
- Licence
- Locations
- arXiv (Cornell University) (submittedVersion, cc-by)
- arXiv (Cornell University) (cc-by)
- Topics
- Physical Sciences › Computer Science › Software › Advanced Malware Detection Techniques
- Physical Sciences › Computer Science › Information Systems › Spam and Phishing Detection
- Physical Sciences › Computer Science › Information Systems › Web Application Security Vulnerabilities
- Keywords
- generative AI, data exfiltration, network behavior analysis, domain reputation
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
A language model drew the claims from the paper on 2026-11-13, under version 3 of the claim definition (model deepseek-v4.1-flash, prompt extract-v3).
A second model labelled each claim on 2026-11-13 (model jev-1.13-20260917, definition revision gold-guideline-v0.2).
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
How to cite
Cite CoChat for the checks on this page, and the paper for its own findings.
- This page
- CoChat. (2026). Citation check: Malicious GenAI Chrome Extensions: Unpacking Data Exfiltration and Malicious Behaviours. https://app.cochat.ai/papers/10.48550/arxiv.2512.10029
- The paper
- Seetharam, S. B., Nabeel, M., & Melicher, W. (2025). Malicious GenAI Chrome Extensions: Unpacking Data Exfiltration and Malicious Behaviours. arXiv. https://doi.org/10.48550/arxiv.2512.10029
Data sources
Bibliographic data: Semantic Scholar, OpenAlex, Crossref.
Contains information from the Semantic Scholar Academic Graph Datasets, made available under the ODC Attribution License (ODC-BY 1.0).
Semantic Scholar’s data is described in: Kinney, R., et al. (2023). The Semantic Scholar Open Data Platform. arXiv:2301.10140.
