

The DOI matches its Crossref record; 42 of the 42 references it cites were found in a registry or an index; none of the 4 sources its claims cite is checked for support yet.
A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems
Open accessAbstract
Intrusion Detection Systems are expected to detect and prevent malicious activities in a network, such as a smart grid. However, they are the main systems targeted by cyber-attacks. A number of approaches have been proposed to classify and detect these attacks, including supervised machine learning. However, these models require large labeled datasets for training and testing. Therefore, this paper compares the performance of supervised and unsupervised learning models in detecting cyber-attacks. The benchmark of CICDDOS 2019 was used to train, test, and validate the models. The supervised models are Gaussian Naïve Bayes, Classification and Regression Decision Tree, Logistic Regression, C-Support Vector Machine, Light Gradient Boosting, and Alex Neural Network. The unsupervised models are Principal Component Analysis, K-means, and Variational Autoencoder. The performance comparison is made in terms of accuracy, probability of detection, probability of misdetection, probability of false alarm, processing time, prediction time, training time per sample, and memory size. The results show that the Alex Neural Network model outperforms the other supervised models, while the Variational Autoencoder model has the best results compared to unsupervised models.
Overview
CoChat Summary
TL;DR
This paper compares supervised and unsupervised machine learning models for intrusion detection using the CICDDOS 2019 dataset. It finds that AlexNet performs best overall, while the Variational Autoencoder is the best unsupervised model.
Key findings
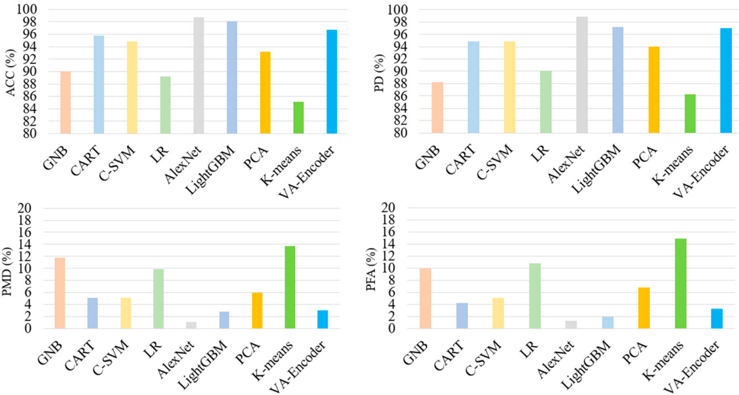
- AlexNet yielded the best results among all supervised and unsupervised models; the ranking reported is AlexNet, LightGBM, VA-Encoder, CART, C-SVM, PCA, GNB and LR, and K-means.
- For DNS attacks, AlexNet achieved ACC 99.13%, PD 99.81%, PMD 0.19%, and PFA 0.93%, while VA-Encoder achieved ACC 96.83%, PD 97.11%, PMD 2.89%, and PFA 3.23%.
- AlexNet had the best processing time, prediction time, training time per sample, and memory size among the compared models, with PRT 1.01 s, PT 1 s, TPS 0.01 s, and M 102 MiB in Table 4; GNB had the worst performance on these metrics (PRT 4.33 s, PT 4.15 s, TPS 0.82 s, M 245 MiB).
- VA-Encoder yielded the highest performance among unsupervised models, while K-means had the lowest ACC and PD and the highest PMD and PFA among unsupervised models.
Methods
- Used the CICDDOS 2019 dataset, containing normal traffic and 10 attack types; the lowest attack sample count (366,461 for UDP-Lag) was used as a threshold for all attacks, and 4,031,071 normal samples were randomly selected, resulting in 8,062,142 samples. The original 88 features were reduced to 21 features using Pearson’s Correlation and tree-based feature selection.
- Supervised models: Gaussian Naïve Bayes, Classification and Regression Tree, C-Support Vector Machine, Logistic Regression, Alex Neural Network, and Light Gradient Boosting. Unsupervised models: Principal Component Analysis, K-means, and Variational Autoencoder. Preprocessing included mean imputation and Yeo-Johnson Power Transformer; supervised models used labeled data, while the label column was removed for unsupervised models.
- Models were optimized with grid search and ADAM optimizer and evaluated with ACC, PD, PMD, PFA, processing time, prediction time, training time per sample, and memory size. A 5-fold cross-validation approach trained on 80% of the data and tested on the remaining 20%.
Limitations
- The paper does not state an explicit limitations section; it only notes future work to investigate supervised and unsupervised deep learning models for detecting attacks on intrusion detection systems.
- Evident from the text: the comparison uses only the CICDDOS 2019 dataset, so generalization to other networks or smart-grid environments is not established.
- Evident from the text: balancing the dataset by limiting every attack class to 366,461 samples and randomly selecting normal samples may discard data and affect representativeness; additionally, some reported table entries are incomplete or unclear in the provided text (e.g., VA-Encoder memory size is blank in Table 4, and Table 6 formatting is garbled), which limits reproducibility.
Model-written summary. Check it against the paper before relying on it.
Integrity signals
Registry
Cites
Statistics
Figures



Verification
Claims the paper makes
0 Valid · 1 Not valid · 2 Not checked · 35 Own results and interpretations
A result the paper states — it cites no source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“GNB and LR models yielded the worst results of the supervised models.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > •
plain- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“AlexNet outperformed VA-Encoder in detecting cyber-attacks.”
- Also stated in: § 4. Results and Discussion · hedged
“To summarize, AlexNet could detect LDAP, DNS, SNMP, MSSQL, NetBIOS, NTP, SSDP, TFTP, UDP, UDP-Lag attacks, and Benign traffic better than VA-Encoder.”
- Also stated in: § 5. Conclusions · plain
“In addition, cyber-attacks can be detected better with better performance in comparison with the same attacks using Variational-Encoder.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 4. Results and Discussion
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Also stated in: § 4. Results and Discussion · hedged
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“however, this last model detected SSDP, NTP, and TFP with the lowest performance.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 4. Results and Discussion
plain- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: unclear — It is unclear whether the paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper states — it cites no source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“The worst performance model among the unsupervised models was K-means.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > •
plain- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: unclear — It is unclear whether the paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“AlexNet outperformed the VA-Encoder model when detecting cyber-attacks.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 4. Results and Discussion
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
16 more claims
Create a free account to see all 38 claims and to verify the 4 references still open.
- Borderline: one of the tests for a substantial claim is unclear. 1
- It may state two separate claims as one. 11
- The quote only partly states this claim. 1
- Probably not a substantial claim. 5
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
Each contradiction between two passages listed here was confirmed by an independent check.
Rated major: it would touch a result — a value a result rests on, reported and recomputed p-values on opposite sides of the significance level, two passages that conflict with no sign which is right, or a cited work retracted before this paper was published.
In the paper
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 3.1. Dataset
“This dataset includes normal traffic samples and samples from 10 attack types.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 3.1. Dataset
“To address such an issue, the lowest number of attack samples (366,461) that belongs to the UDP-lag attacks was used as a threshold for all attacks; therefore, each attack category was limited to this number.For the normal samples, we randomly selected 4,031,071, resulting in a dataset with 8,062,142 samples.”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 4. Results and Discussion
“AlexNet detected NetBIOS attacks with the highest PRT, PT, TPS, and M compared to those of other attacks”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 5. Conclusions
“| | NetBIOS | 1.9 | 1.4 | 0.9 | 191 | | AlexNet | NTP | 1.2 | 1.7 | 0.6 | 182 |”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 4. Results and Discussion
“VA-Encoder detected SSDP attacks with the highest PRT, PT, TPS, and M compared to those other attacks.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 5. Conclusions
“| | LDAP | 3.5 | 3.1 | 0.4 | 290 | | | DNS | 3.4 | 2.9 | 0.4 | 278 | | | SNMP | 3.2 | 2.3 | 0.9 | 276 | | | MSSQL | 2.9 | 2.3 | 0.3 | 254 | | | NetBIOS | 2.9 | 2.3 | 0.4 | 246 | | VA-Encoder | NTP | 2.9 | 1.3 | 0.6 | 277 | | | SSDP | 3.9 | 2.1 | 0.5 | 297 |”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 4. Results and Discussion
“VA-Encoder yielded the best results among the unsupervised models in terms of ACC, PD, PMD, PFA, PRT, PT, TPS, and M.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 5. Conclusions
“| PCA | 1.9 | 0.91 | 0.89 | 164 | | K-means | 1.9 | 1.4 | 0.81 | 180 | | VA-Encoder | 1.77 | 1.2 | 0.5 | |”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 3.5. Evaluation Metrics
“PRT refers to the total time necessary to train, test, and validate the models.”
§ A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems > 5. Conclusions
“| AlexNet | NTP | 1.2 | 1.7 | 0.6 | 182 |”
5 more findings
Create a free account to see every finding of this check.
Citations
Cites
Principal component analysis: A review and recent developments
Jolliffe, I. T., & Cadima, J. (2016) · Philosophical Transactions of the Royal Society A: Mathematical, Physical and Engineering Sciences · doi:10.1098/rsta.2015.0202 · Cited by 10,117
Understanding of a convolutional neural network
Albawi, S., Mohammed, T. A., & Al-Zawi, S. (2017) · 2017 International Conference on Engineering and Technology (ICET) · doi:10.1109/icengtechnol.2017.8308186 · Cited by 3,986
ML-KNN: A lazy learning approach to multi-label learning
Zhang, M.-L., & Zhou, Z.-H. (2007) · Pattern Recognition · doi:10.1016/j.patcog.2006.12.019 · Cited by 3,552
Developing Realistic Distributed Denial of Service (DDoS) Attack Dataset and Taxonomy
Sharafaldin, I., Lashkari, A. H., Hakak, S., & Ghorbani, A. A. (2019) · 2019 International Carnahan Conference on Security Technology (ICCST) · doi:10.1109/ccst.2019.8888419 · Cited by 1,275
Bayesian statistics and modelling
van de Schoot, R., Depaoli, S., King, R., Kramer, B., Märtens, K., Tadesse, M. G., Vannucci, M., Gelman, A., Veen, D., Willemsen, J., et al. (2021) · Nature Reviews Methods Primers · doi:10.1038/s43586-020-00001-2 · Cited by 1,176
Decision tree methods: applications for classification and prediction.
Song, Y. Y., & Lü, Y. (2015) · PubMed · doi:10.11919/j.issn.1002-0829.215044 · Cited by 1,132
Selection of K in K-means clustering
Pham, D. T., Dimov, S. S., & Nguyen, C. D. (2005) · Proceedings of the Institution of Mechanical Engineers, Part C: Journal of Mechanical Engineering Science · doi:10.1243/095440605x8298 · Cited by 597
A Supervised Intrusion Detection System for Smart Home IoT Devices
Anthi, E., Williams, L., Slowinska, M., Theodorakopoulos, G., & Burnap, P. (2019) · IEEE Internet of Things Journal · doi:10.1109/jiot.2019.2926365 · Cited by 597
Wang, S.-C. (2003) · Interdisciplinary Computing in Java Programming · doi:10.1007/978-1-4615-0377-4_5 · Cited by 580
On the training of radial basis function classifiers
Musavi, M. T., Ahmed, W., Chan, K. H., Faris, K. B., & Hummels, D. M. (1992) · Neural Networks · doi:10.1016/s0893-6080(05)80038-3 · Cited by 569
Research works printed but not linked: 4
- Tazi, K., Abdi, F., and Abbou, M.F. (2015). International Renewable and Sustainable Energy Conference (IRSEC), IEEE.
- Mrabet, Z.E., Ghazi, H.E., and Kaabouch, N. (2019). Conference on Electro Information Technology (EIT), IEEE.
- Altwaijry, H. (2013). IAENG Transactions on Engineering Technologies, Springer.
- Singh, 2014, Comparative study ID3, cart and C4. 5 decision tree algorithm: A survey, Int. J. Adv. Inf. Sci. Technol. (IJAIST), 27, 97
Cited by
Machine Learning: Models, Challenges, and Research Directions
Khoei, T. T., & Kaabouch, N. (2023) · Future Internet · doi:10.3390/fi15100332 · Cited by 119
Self-citationElectricity Theft Detection Using Deep Reinforcement Learning in Smart Power Grids
El-Toukhy, A. T., Badr, M. M., Mahmoud, M. M. E. A., Srivastava, G., Fouda, M. M., & Alsabaan, M. (2023) · IEEE Access · doi:10.1109/access.2023.3284681 · Cited by 112
Alnajim, A. M., Habib, S., Islam, M., Thwin, S. M., & Alotaibi, F. (2023) · Technologies · doi:10.3390/technologies11060161 · Cited by 89
Li, S., Zeng, W., Ni, X., Liu, Q., Li, W., Stackpole, M. L., Zhou, Y., Gower, A., Krysan, K., Ahuja, P., et al. (2023) · Proceedings of the National Academy of Sciences · doi:10.1073/pnas.2305236120 · Cited by 87
Muthubalaji, S., Muniyaraj, N. K., Rao, S. P. V. S., Thandapani, K., Mohan, P. R., Somasundaram, T., & Farhaoui, Y. (2024) · Big Data Mining and Analytics · doi:10.26599/bdma.2023.9020022 · Cited by 76
Metadata
- Authors
- Talaei Khoei, T., & Kaabouch, N.
- Affiliations
- School of Electrical Engineering and Computer Science, University of North Dakota, Grand Forks, ND 58202, USA
- University of North Dakota (US)
- Venue
- Information
- Publisher
- MDPI AG
- Published
- 2023-02-07
- Volume
- 14
- Issue
- 2
- Pages
- 103
- ISSN
- 2078-2489 (ISSN-L)
- OpenAlex
- W4319439792
- Cited by
- 95
- References
- 40
- Citations by year
- 2026: 23 · 2025: 32 · 2024: 22 · 2023: 18
- FWCI
- 7.26
- Type
- journal article
- Language
- en
- Open access
- gold
- doi.org
- Licence
- Locations
- Information (publishedVersion, cc-by)
- DOAJ (DOAJ: Directory of Open Access Journals) (submittedVersion, cc-by-sa)
- Topics
- Physical Sciences › Computer Science › Computer Networks and Communications › Network Security and Intrusion Detection
- Physical Sciences › Computer Science › Hardware and Architecture › Network Packet Processing and Optimization
- Physical Sciences › Computer Science › Artificial Intelligence › Artificial Immune Systems Applications
- Keywords
- intrusion detection, cyberattack detection, supervised learning, unsupervised learning, smart grid security, Gaussian naive Bayes, decision tree, support vector machine, LightGBM, AlexNet, variational autoencoder, K-means clustering, principal component analysis, false alarm rate, detection accuracy
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
A language model drew the claims from the paper on 2026-11-16, under version 3 of the claim definition (model deepseek-v4.1-flash, prompt extract-v3).
A second model labelled each claim on 2026-11-16 (model jev-1.13-20260917, definition revision gold-guideline-v0.2).
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
How to cite
Cite CoChat for the checks on this page, and the paper for its own findings.
- This page
- CoChat. (2026). Citation check: A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems. https://app.cochat.ai/papers/10.3390/info14020103
- The paper
- Talaei Khoei, T., & Kaabouch, N. (2023). A Comparative Analysis of Supervised and Unsupervised Models for Detecting Attacks on the Intrusion Detection Systems. Information. https://doi.org/10.3390/info14020103
Data sources
Bibliographic data: Semantic Scholar, OpenAlex, Crossref.
Contains information from the Semantic Scholar Academic Graph Datasets, made available under the ODC Attribution License (ODC-BY 1.0).
Semantic Scholar’s data is described in: Kinney, R., et al. (2023). The Semantic Scholar Open Data Platform. arXiv:2301.10140.
