

The DOI matches its Crossref record.
Understanding Man-in-the-middle-attack through Survey of Literature
Open accessAbstract
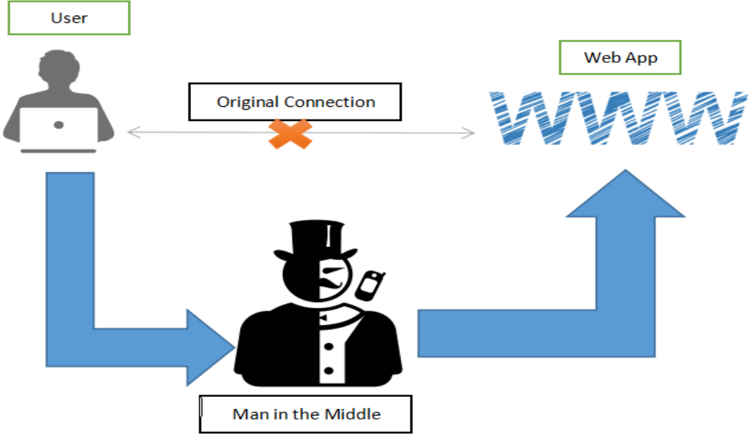
These days cyberattack is a serious criminal offense and it is a hotly debated issue moreover. A man-in-the-middle-attack (MITM) is a kind of cyberattack where an unapproved outsider enters into an online correspondence between two users, remains escaped the two parties. The malware that is in the middle-attack often monitors and changes individual/classified information that was just realized by the two users. A man-in-the-middle-attack as a protocol is subjected to an outsider inside the system, which can access, read and change secret information without keeping any tress of manipulation. This issue is intense, and most of the cryptographic systems without having a decent authentication security are threatened to be hacked by the malware named MITM. This paper essentially includes the view of understanding the term of MITM; the current work is mainly emphasized to accumulate related data/information in a single article so that it can be a reference to conduct research further on this topic at college/undergraduate level. This paper likewise audits most cited research and survey articles on MITM recorded on 'Google Scholar'. The result showed that the MITM has correlation to the user behavior, in which this must be considered and careful understood for the way how to solve this problem. The motivation behind this paper is to help the readers for understanding and familiarizing the topic 'man-in-the-middle attack'.
Overview
The claims and statistics of this paper haven’t been checked yet.
Run the check — free, no account needed. It reads the open-access text and checks the sources it cites.
Integrity signals
Registry
Cites
Statistics
Figures
Verification
Claims the paper makes
The claims and statistics of this paper haven’t been checked yet.
Run the check — free, no account needed. It reads the open-access text and checks the sources it cites.
Claims other papers make about this one
Each is checked against this paper’s own text: does it say what the citing paper says it does?
In the citing paper
“There are several types of MITM attacks, and the man-in-the-browser variant injects malicious software into the victim’s computer or mobile device through phishing. Upon clicking on a phishing e-mail link or opening the attachment, the user loads the malware, and the malware installs itself on the browser without the user’s knowledge. The malware enables the attacker to capture the information”
From Impact, Vulnerabilities, and Mitigation Strategies for Cyber-Secure Critical Infrastructure. (2023) · cites this paper as [37]
In the citing paper
“The attacker gains access to an unsecured network, often targeting networks in public areas such as Wi-Fi access points [37].”
From Impact, Vulnerabilities, and Mitigation Strategies for Cyber-Secure Critical Infrastructure. (2023) · cites this paper as [37]
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
The self-check needs the paper’s full text.
Citations
Cites
Still being checked.
Research works printed but not linked: 22
- Chaudhari, N. S., & SAXENA, N. (2014). NS-AKA: An improved and efficient AKA protocol for 3G (UMTS) networks. International Conference on Advances in Computer Science and Electronics Engineering -CSEE 2014, 220-224. https://doi.org/10.15224/978-1-63248- 000-2-74 · DOI
- Chen, Z., Guo, S., Zheng, K., & Yang, Y. (2007). Modeling of man-in-the-middle attack in the wireless networks. 2007 International Conference on Wireless Communications, Networking and Mobile Computing, WiCOM 2007. https://doi.org/10.1109/WICOM.2007.562 · DOI
- Conti, M., Dragoni, N., & Lesyk, V. (2016). A Survey of Man in the Middle Attacks. In IEEE Communications Surveys and Tutorials (Vol. 18, Issue 3). https://doi.org/10.1109/COMST.2016.2548426 · DOI · Paper page
- Dutta, A. K. (2018). Deployment of Soft-Computing for System Computing and Informatics. American Journal of Computer Science and Information Technology, 06(02). https://doi.org/10.21767/2349-3917.100018 · DOI
- Feher, B., Sidi, L., Shabtai, A., Puzis, R., & Marozas, L. (2018). WebRTC security measures and weaknesses. International Journal of Internet Technology and Secured Transactions, 8(1). https://doi.org/10.1504/IJITST.2018.092138 · DOI
- Hardin, N. V. (2018). UNCOVERING THE SECRECY OF STINGRAYS: What Every Practitioner Needs to Know. Criminal Justice, 32(4), 20-24.
- Huang, Y. L., Shen, C. Y., & Shieh, S. W. (2011). S-AKA: A provable and secure authentication key agreement protocol for UMTS networks. IEEE Transactions on Vehicular Technology, 60(9). https://doi.org/10.1109/TVT.2011.2168247 · DOI
- Hudaib, A. A. Z. (2014). Comprehensive Social Media Security Analysis & XKeyscore Espionage Technology. In Zare Hudaib International Journal of Computer Science and Security (IJCSS) (Issue 8).
- Hwang, T., & Gope, P. (2014). Provably secure mutual authentication and key exchange scheme for expeditious mobile communication through synchronously one-time secrets. Wireless Personal Communications, 77(1). https://doi.org/10.1007/s11277- 013-1501-5 · DOI
- Kozaczuk, W., & Kozaczuk, W. (1984). Enigma: How the German Machine Cipher was Broken, and how it was Read by the Allies in World War Two (C. Kasparek (ed.); 2nd ed.). University Publications of America. https://books.google.co.id/books/about/Enigma.html?id=5hJnAAAAMAAJ&redir_esc=y
- Meyer, U., & Wetzel, S. (2004). A man-in-the-middle attack on UMTS. WiSe '04: Proceedings of the 3rd ACM Workshop on Wireless Security, 90-97. https://doi.org/https://doi.org/10.1145/1023646.1023662 · DOI
- Oh, M., Kim, Y. G., Hong, S., & Cha, S. (2012). ASA: Agent-based secure ARP cache management. IET Communications, 6(7). https://doi.org/10.1049/iet-com.2011.0566 · DOI
- Ornaghi, A., & Valleri, M. (2003). Man in the middle attacks. Blackhat Conference Europe. https://blackhat.com/presentations/bh-europe-03/bh-europe-03-valleri.pdf
- Ou, H. H., Hwang, M. S., & Jan, J. K. (2010). A cocktail protocol with the Authentication and Key Agreement on the UMTS. Journal of Systems and Software, 83(2). https://doi.org/10.1016/j.jss.2009.08.019 · DOI
- Rahim, R. (2017). Man-in-the-middle-attack prevention using interlock protocol method. ARPN Journal of Engineering and Applied Sciences, 12(22). https://doi.org/10.17605/osf.io/wsa8d · DOI
- Saif, S., Gupta, R., & Biswas, S. (2018). Implementation of cloud-assisted secure data transmission in WBAN for healthcare monitoring. Advances in Intelligent Systems and Computing, 706. https://doi.org/10.1007/978-981-10-8237-5_64 · DOI
- Saxena, N., & Chaudhari, N. S. (2014). Secure-AKA: An efficient AKA protocol for UMTS networks. Wireless Personal Communications, 78(2). https://doi.org/10.1007/s11277- 014-1821-0 · DOI
- Schuckers, S. A. C. (2002). Spoofing and Anti-Spoofing Measures. In Information Security Technical Report (Vol. 7, Issue 4). https://doi.org/10.1016/S1363-4127(02)00407-7 · DOI
- Sounthiraraj, D., Sahs, J., Greenwood, G., Lin, Z., & Khan, L. (2014). SMV-HUNTER: Large Scale, Automated Detection of SSL/TLS Man-in-the-Middle Vulnerabilities in Android Apps. https://doi.org/10.14722/ndss.2014.23205 · DOI
- Su, Z., Timmermans, W., Zeng, Y., Schulz, J., John, V. O., Roebeling, R. A., Poli, P., Tan, D., Kaspar, F., Kaiser-Weiss, A. K., Swinnen, E., Toté, C., Gregow, H., Manninen, T., Riihelä, A., Calvet, J. C., Ma, Y., & Wen, J. (2018). An overview of european efforts in generating climate data records. Bulletin of the American Meteorological Society, 99(2). https://doi.org/10.1175/BAMS-D-16-0074. · DOI
- Sun, D. Z., Mu, Y., & Susilo, W. (2018). Man-in-the-middle attacks on Secure Simple Pairing in Bluetooth standard V5.0 and its countermeasure. Personal and Ubiquitous Computing, 22(1). https://doi.org/10.1007/s00779-017-1081-6 · DOI
- Valluri, M. R. (2018). Cryptanalysis of Xinyu et al.'s NTRU-lattice based key exchange protocol. Journal of Information and Optimization Sciences, 39(2). https://doi.org/10.1080/02522667.2017.1368182 · DOI
Cited by
Sorted by citations
Impact, Vulnerabilities, and Mitigation Strategies for Cyber-Secure Critical Infrastructure.
Riggs, H., Tufail, S., Parvez, I., Tariq, M., Khan, M. A., Amir, A., Vuda, K. V., & Sarwat, A. I. (2023) · Sensors · doi:10.3390/s23084060 · Cited by 124
“The attacker gains access to an unsecured network, often targeting networks in public areas such as Wi-Fi access points [37].”
BackgroundInfluentialEyeleko, A. H., & Feng, T. (2023) · IEEE Internet of Things Journal · doi:10.1109/jiot.2023.3308195 · Cited by 38
“One example is the attacker’s use of a MITM attack [103] to intercept Web traffic and access sensitive information within Prime MotorX’s processing layer due to the lack of Web traffic encryption.”
Background
Metadata
- Authors
- Mallik, A., Ahsan, A., Shahadat, M. M. Z., & Tsou, J. C.
- Affiliations
- Rajshahi University of Engineering and Technology (BD)
- China University of Technology (TW)
- Venue
- Indonesian Journal of Computing, Engineering and Design (IJoCED)
- Published
- 2019-04-21
- Volume
- 1
- Issue
- 1
- Pages
- 44
- ISSN
- 2656-1972 (ISSN-L)
- 2656-8179
- OpenAlex
- W2993011270
- Cited by
- 11
- References
- 0
- Citations by year
- 2025: 2 · 2024: 2 · 2023: 4 · 2021: 2 · 2020: 1
- FWCI
- 0.41
- Type
- journal article
- Language
- en
- Open access
- diamond
- doi.org
- Licence
- cc-by-nc
- Locations
- Indonesian Journal of Computing Engineering and Design (IJoCED) (publishedVersion, cc-by-nc)
- DOAJ (DOAJ: Directory of Open Access Journals) (submittedVersion, cc-by-sa)
- Topics
- Physical Sciences › Computer Science › Computer Networks and Communications › Advanced Authentication Protocols Security
- Physical Sciences › Computer Science › Information Systems › Information and Cyber Security
- Physical Sciences › Computer Science › Computer Networks and Communications › Network Security and Intrusion Detection
- Keywords
- man-in-the-middle attacks, cyberattacks, authentication security, ciphers, malware, user behavior, interception of communications
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
How to cite
Cite CoChat for the checks on this page, and the paper for its own findings.
- This page
- CoChat. (2026). Citation check: Understanding Man-in-the-middle-attack through Survey of Literature. https://app.cochat.ai/papers/10.35806/ijoced.v1i1.36
- The paper
- Mallik, A., Ahsan, A., Shahadat, M. M. Z., & Tsou, J. C. (2019). Understanding Man-in-the-middle-attack through Survey of Literature. Indonesian Journal of Computing, Engineering and Design (IJoCED). https://doi.org/10.35806/ijoced.v1i1.36
