

The DOI matches its Crossref record; 23 of the 23 references it cites were found in a registry or an index; none of the 5 sources its claims cite is checked for support yet.
Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok
Open accessAbstract
This study evaluates the IT governance maturity of the Central Lombok Civil Service Police Unit (Satpol PP) using the COBIT 2019 framework, focusing on improving service continuity and data security in a resource-constrained public sector context. The assessment, conducted across key domains such as service delivery, data security, and compliance, revealed that Satpol PP operates at Level 3 (Defined) maturity. While processes are documented and standardized, significant gaps remain in automation, proactive risk management, and real-time monitoring. These limitations hinder the organization's ability to optimize service continuity and safeguard sensitive data effectively. The study emphasizes the innovative application of COBIT 2019 in a resource-limited environment, demonstrating how the framework can be adapted to prioritize immediate needs while progressively advancing IT governance maturity. Key recommendations include automating monitoring systems, enhancing data security protocols, and implementing proactive risk management strategies. These findings contribute valuable insights into the challenges and solutions for IT governance in public institutions, providing a replicable model for similar organizations. Future research should explore the long-term impacts of these recommendations on IT governance maturity and service efficiency in other public sector contexts.
Overview
AI snapshot
Written from the paper’s full text.
TL;DR
This case study applies the COBIT framework to assess IT governance maturity at the Central Lombok Civil Service Police Unit (Satpol PP), finding an overall Level 3 (Defined) maturity with weaker service delivery and data security. It recommends automated monitoring, stronger data security protocols, and proactive risk management as a phased roadmap for resource-constrained public institutions.
Key findings
- Satpol PP's overall IT governance maturity is Level 3 (Defined): processes are documented and standardized but lack advanced evaluation, automation, and optimization mechanisms.
- Domain-level results (Table 3): Service Delivery Level 3 (well-documented but not adaptable to demand fluctuations), Data Security Level 2 (basic protocols, no real-time encryption or automated threat detection), Compliance Level 3 (practices followed but audit mechanisms need enhancement).
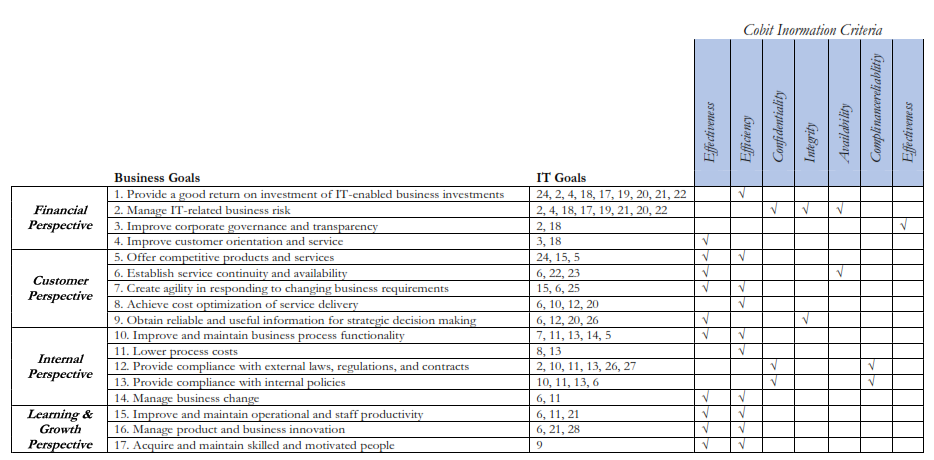
- A separate assessment table (Table 2) reports Business Goals, IT Goals, and IT Processes at Level 3, with Service Delivery and Data Security at Level 2, and overall maturity at Level 3.
- Three challenges are identified for advancing maturity: resource limitations (funding for tools and training), lack of automated tools (no real-time monitoring or analytics), and training gaps among IT staff.
Methods
- Case study of the Central Lombok Civil Service Police Unit (Satpol PP), using the COBIT framework to assess IT governance maturity across domains including service delivery, data security, and compliance.
- Data collection combined primary sources (structured observation focused on discrepancies between documented policies and actual practice, and semi-structured interviews with IT managers, administrators, and business strategists) with secondary sources (literature review and internal documents such as IT governance policies, operational manuals, and performance reports).
- Analysis proceeded stepwise: mapping business goals to IT goals, identifying key IT processes, domain-specific analysis, and maturity-level assessment via structured questionnaires scored against the framework's maturity levels (Level 1 Initial to Level 5 Optimized), followed by tailored recommendations.
Limitations
- The paper states that Satpol PP operates under resource constraints (limited funding, technical expertise, and organizational readiness) that restrict adoption of advanced IT governance practices; these are framed as contextual constraints rather than study limitations.
- The paper does not state explicit methodological limitations such as sample size, single-case generalizability, or interview counts.
- Evident in the text: the paper is internally inconsistent about which framework was used — the title, abstract, and conclusion say COBIT 2019, while the Methods and Results sections repeatedly describe applying COBIT 4.1 (including "COBIT 4.1 maturity model" and "COBIT 4.1 Framework" in Figure 1), and the secondary literature review is described as focused on COBIT 4.1. Table numbering is also duplicated (two "Table 3" entries), and no quantitative questionnaire scores or participant counts are reported.
Model-written summary. Check it against the paper before relying on it.
Integrity signals
Registry
Cites
Statistics
Figures
Verification
Claims the paper makes
5 Sources not found · 4 Own result · 2 Own interpretation · 1 Own method · 1 No basis given
The paper states this without a source or data behind it here, so there is nothing to check it against. The quote shows it is in the paper.
In the paper
“In the case of Satpol PP, this alignment is at a moderate level (Level 3), indicating that there is foundational integration between business and IT goals but room for strategic improvement.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 3.2 Analysis of Business and IT Goals Alignment
hedgedSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: unclear — It is unclear whether the paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“The assessment, conducted across key domains such as service delivery, data security, and compliance, revealed that Satpol PP operates at Level 3 (Defined) maturity.”
- Also stated in: § 3.1 Overview of IT Governance Maturity Assessment Using COBIT 4.1 · plain
“The study revealed that the Central Lombok Civil Service Police Unit (Satpol PP) operates at a moderate level of IT governance maturity, corresponding to Level 3 (Defined) within the COBIT 2019 framework.”
- Also stated in: § 4. CONCLUSION · hedged
“The findings indicate that Satpol PP operates at Level 3 (Defined), with processes that are documented and standardized but lack advanced mechanisms for real-time evaluation, automation, and proactive risk management.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > Abstract
plainSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Also stated in: § 3.1 Overview of IT Governance Maturity Assessment Using COBIT 4.1 · plain
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“However, the maturity assessment suggests that IT activities are often reactive, addressing issues as they arise rather than proactively preventing them.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 3.2.1 Business Goals
hedged- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
In the paper
“Studies have shown that COBIT 2019 enhances IT governance by providing standardized processes that align IT functions with organizational goals and support efficient resource allocation [4].”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 1. INTRODUCTION
What the sources say
- Not matchedcites [4]
Couldn’t be matched to a paper in Crossref, so it can’t be checked.
boostedstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Not matched
In the paper
“Additionally, COBIT 2019's adaptability allows public institutions to customize the framework according to their specific needs, making it aolution for varying levels of IT governance maturity [18].”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > Amir Bagja, Zaenul Amri, at all | 2763
What the sources say
- Not matchedcites [18]
Couldn’t be matched to a paper in Crossref, so it can’t be checked.
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Not matched
In the paper
“Furthermore, empirical studies indicate that COBIT 2019's domain-specific guidance, such as its focus on service delive security, is particularly beneficial in public sector settings where compliance with external regulations and internal policies is crucial [16].”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > Amir Bagja, Zaenul Amri, at all | 2763
What the sources say
- Not matchedcites [16]
Couldn’t be matched to a paper in Crossref, so it can’t be checked.
hedgedstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Not matched
A conclusion the paper draws from its own results — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“However, this study contributes uniquely by showcasing how COBIT 2019 can be adapted in a resource-constrained context to address service continuity and data management challenges.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 3.1 Overview of IT Governance Maturity Assessment Using COBIT 4.1
plainstates a possible causeSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Rests on an assumption: Satpol PP operates within a resource-constrained environment that limits its capacity to adopt advanced IT governance practices.
- It may state two separate claims as one. 6
- Probably not a substantial claim. 2
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“This level indicates that IT processes are documented and standardized but lack advanced mechanisms for evaluation and optimization.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 3.1 Overview of IT Governance Maturity Assessment Using COBIT 4.1
hedgedSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
It may state two separate claims as one.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“Key gaps identified include limited automation, a lack of proactive risk management, and insufficient real-time monitoring systems.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 3.1 Overview of IT Governance Maturity Assessment Using COBIT 4.1
plainSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
It may state two separate claims as one.
What the paper did — it cites no source for this, so there is none to check. The quote shows it is in the paper.
In the paper
“Data collection was conducted through a combination of primary and secondary sources, enabling triangulation and strengthening the validity of the findings.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 2.1 Data Collection
boostedstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: fails — The paper’s conclusions may not depend on it.
- Based: passes — The paper gives a reason why it holds.
Probably not a substantial claim. The paper’s conclusions may not depend on it. It may state two separate claims as one.
A conclusion the paper draws from its own results — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“These limitations hinder the organization's ability to respond promptly to emerging threats and optimize service continuity and data security.”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 3.1 Overview of IT Governance Maturity Assessment Using COBIT 4.1
plainstates a causeSingle case- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
It may state two separate claims as one.
In the paper
“Previous research in both private and public sectors has demonstrated that structured IT governance educe operational risks and improve the quality of service delivery by promoting consistency and reliability in IT processes [13].”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > Amir Bagja, Zaenul Amri, at all | 2763
What the sources say
- Not matchedcites [13]
Couldn’t be matched to a paper in Crossref, so it can’t be checked.
boostedstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
It may state two separate claims as one.
- Not matched
In the paper
“Among these, COBIT 2019 (Control Objectives for Information and Related Technologies) has gained recognition as a comprehensive tool for IT governance.It offers structured processes and measurable objectives that align IT operations with organizational goals while ensuring service continuity and data security [3].”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 1. INTRODUCTION
What the sources say
- Not matchedcites [3]
Couldn’t be matched to a paper in Crossref, so it can’t be checked.
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
Probably not a substantial claim. It may state two separate claims as one.
- Not matched
The paper relies on this without support.
Satpol PP operates within a resource-constrained environment that limits its capacity to adopt advanced IT governance practices.
“Despite these demands, Satpol PP operates within a resource-constrained environment, which limits its capacity to adopt advanced IT governance practices.”
The paper relies on this without support.
Public institutions tend to take reactive rather than proactive approaches to IT governance, addressing issues only after they have impacted services or security.
“Additionally, there is a tendency in such organizatiot reactive rather than proactive approaches to IT governance, meaning that issues are often addressed only after they have impacted services or security.”
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
Each contradiction between two passages listed here was confirmed by an independent check.
Rated major: it would touch a result — a value a result rests on, reported and recomputed p-values on opposite sides of the significance level, two passages that conflict with no sign which is right, or a cited work retracted before this paper was published.
In the paper
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 2. METHODS
“This study employs the COBIT 2019 framework to evaluate the IT governance maturity level within the Central Lombok Civil Service Police Unit (Satpol PP)”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 2.2 Data Analysis
“The data analysis phase involved the structured application of the COBIT 4.1 framework to assess IT governance maturity.”
Rated major: it would touch a result — a value a result rests on, reported and recomputed p-values on opposite sides of the significance level, two passages that conflict with no sign which is right, or a cited work retracted before this paper was published.
In the paper
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 4. CONCLUSION
“| Service | Level 2 | Basic documentation of processes exists, but lacks | | Delivery | | adaptability and proactive response capabilities. |”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 4. CONCLUSION
“| Service | Level 3 | Well-documented processes, but lacks adaptability for | | Delivery | | demand fluctuations and unforeseen challenges. |”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 3.2.1 Business Goals
“This approach aligns with findings from Afdhani and Soewito (2024) [26]”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > References
“26. G. M. W. Tangka and E. Lompoliu, "Information Technology Governance Using the COBIT 2019 Framework in Manado Post Companies," Jurnal Informasi dan Teknologi, pp. 53-62, 2024.”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 4. CONCLUSION
“Table: 3 Table 3 . Domain-Specific IT Governance Maturity Assessment Based on COBIT 4.1”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 4. CONCLUSION
“Table: 3 Table 3 . Identified Challenges and Proposed Solutions for Advancing IT Governance Maturity Levels”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 2.3 Maturity Level Assessment
“Maturity levels in COBIT 4.1 range from Level 1 (Initial) to Level 5 (Optimized)”
§ Enhancing Public Sector IT Governance through COBIT 2019: A Case Study on Service Continuity and Data Management in the Central Lombok > 4. CONCLUSION
“| Level 0 | Non-existent | No formal processes are implemented. IT activities |”
Citations
Cites
Nachrowi, E., Nurhadryani, Y., & Sukoco, H. (2020) · Jurnal RESTI (Rekayasa Sistem dan Teknologi Informasi) · doi:10.29207/resti.v4i4.2265 · Cited by 99
COBIT as a Framework for Enterprise Governance of IT
Haes, S. D., Grembergen, W. V., Joshi, A., & Huygh, T. (2019) · Management for professionals · doi:10.1007/978-3-030-25918-1_5 · Cited by 84
Yasin, M. P. E., Arman, A. A., Edward, I. J. M., & Shalannanda, W. (2020) · International Conference on Telecommunication Systems, Services, and Applications · doi:10.1109/tssa51342.2020.9310875 · Cited by 38
Audit Tata Kelola Teknologi Informasi Menggunakan Framework Cobit 4.1
Imtihan, K., Rodi, M., Ashari, M. K. A., Zaen, M. T. A., & Marzuki, K. (2022) · Matrik Jurnal Manajemen Teknik Informatika dan Rekayasa Komputer · doi:10.30812/matrik.v21i2.1569 · Cited by 30
Self-citationUtomo, D., Wijaya, M. I., Suzanna, S., et al. (2022) · CommIT (Communication and Information Technology) Journal · doi:10.21512/commit.v16i2.8172 · Cited by 17
Sipayung, A., Yunis, R., & Elly, E. (2022) · International Journal of Research and Applied Technology · doi:10.34010/injuratech.v2i2.8085 · Cited by 14
Advancing Towards IT Maturity Governance Excellence: COBIT 2019 in Higher Education (Indonesia)
Febriyani, W., Hendrawan, F. R., & Kusumasari, T. F. (2023) · International Conference on Informatics and Computing (ICIC) · doi:10.1109/icic60109.2023.10382082 · Cited by 10
Capability Gap Analysis in IT Governance for a Logistics Company Using COBIT 2019
Ahmad, Y., Saputra, W. A., & Jamilah, J. (2024) · Journal of Information Systems and Informatics · doi:10.51519/journalisi.v6i3.832 · Cited by 10
Information Technology Governance Design in Trading Companies Using the COBIT 2019 Framework
Leonardo, K., & Latuperissa, R. (2024) · Journal of Information Systems and Informatics · doi:10.51519/journalisi.v6i3.798 · Cited by 8
Kassim, M., & Mujinga, M. (2024) · Journal of Information Systems and Informatics · doi:10.51519/journalisi.v6i3.820 · Cited by 7
Research works printed but not linked: 4
- M. Yasin, A. A. Arman, I. J. M. Edward, and W. Shalannanda, "Designing information security governance recommendations and roadmap using p-ISSN: 2656-5935 http://journal-isi.org/index.php/isi e-ISSN: 2656-4882 2774 | Enhancing Public Sector IT Governance through COBIT 2019: A Case Study ..... COBIT 2019 Framework and ISO 27001: 2013 (Case Study Ditreskrimsus Polda XYZ)," in 2020 14th International Conference on Telecommunication Systems, Services, and Applications (TSSA, IEEE, 2020, pp. 1-5.
- T. H. Thabit, "The Impact of Implementing COBIT 2019 Framework on Reducing the Risks of e-Audit," Journal of Prospective Researches, no. 49, 2021.
- E. Nachrowi, Y. Nurhadryani, and H. Sukoco, "Evaluation of Governance and Management of Information Technology Services Using Cobit 2019 and ITIL 4," Accredited by National Journal Accreditation, vol. 4, no. 2, pp. 764- 774, 2020.
- K. Leonardo and R. Latuperissa, "Information Technology Governance Design in Trading Companies Using the COBIT 2019 Framework," Journal of Information Systems and Informatics, vol. 6, no. 3, pp. 1466-1483, 2024.
Cited by
Sorted by citations
Integrasi IoT dan Katalis Edge Computing untuk Mitigasi Kebisingan Elektronik
Achaqie, H. N. R., & Pratiwi, P. (2025) · Jurnal Ilmiah Sistem Informasi · doi:10.51903/wpt7q648 · Cited by 3
Ensuring Data Quality and Integrity in Modern Enterprises
Vayyala, R. (2025) · IGI Global eBooks · doi:10.4018/979-8-3373-0365-9.ch002 · Cited by 1
Ernawati, Imtihan, K., & Bagye, W. (2025) · Jurnal Informatika dan Rekayasa Elektronik · doi:10.36595/jire.v8i2.1766 · Cited by 1
Self-citationTambalean, F. G. M., Montolalu, C. E. J. C., Takaendengan, M. I., Lapihu, D., Soewoeh, C. A. J., & Tenda, E. P. (2026) · Jurnal Tata Kelola dan Kerangka Kerja Teknologi Informasi · doi:10.34010/jtk3ti.v12i1.19833
Suseno, H. B., & Muhammad, A. H. (2025) · International Research on Big-Data and Computer Technology I-Robot · doi:10.53514/ir.v9i1.646
Pancho, M. T. N., Pancho, R. L., Abante, M. V., Paculanan, R. S., Ellana, R. C., & Geronimo, S. (2026) · International Conference on Computing, Networks and Internet of Things (CNIOT) · doi:10.1109/cniot69547.2026.11582833
Designing a Continuous Value Optimization Assessment Tool for Public-Sector IT Governance
Amelia, I. F., Dewi, F., & Nugraha, R. A. (2026) · International Conference on Advancement in Data Science, E-learning and Information System (ICADEIS) · doi:10.1109/icadeis71120.2026.11644530
Evaluating Smart Tourism Maturity in Indonesia: Integrating User Experience with COBIT Governance
Putri, R. A., Gaol, F. L., Utama, D. N., Legowo, N., & Mauritsius, T. (2026) · International Conference on ICT for Smart Society (ICISS) · doi:10.1109/iciss71466.2026.11715082
Rodi, M., Imtihan, K., Mardi, M., Bagye, W., Amrullah, A., & Fitriyani, B. Y. (2026) · JITEKH
Self-citationNasution, S. A., Sudrajat, A. W., & Mardiani, M. (2026) · UKMC International Conference (UKMC IC) Proceedings · doi:10.32524/ukmcic.v3i1.2302
Metadata
- Authors
- Bagja, A., Amri, Z., Imtihan, K., Rodi, M., & Rusniatun, S. Y.
- Affiliations
- Universitas Hamzanwadi (ID)
- STMIK Lombok (ID)
- Venue
- Journal of Information Systems and Informatics
- Published
- 2024-12-31
- Volume
- 6
- Issue
- 4
- Pages
- 2761-2776
- ISSN
- 2656-4882 (ISSN-L)
- 2656-5935
- OpenAlex
- W4408209840
- Semantic Scholar
- ef5a55a17f16959ef64ea44c548ec2cfdc77da52
- Cited by
- 10
- References
- 8
- Citations by year
- 2026: 6 · 2025: 4
- FWCI
- 2.86
- Type
- journal article
- Language
- en
- Open access
- gold
- doi.org
- Locations
- Journal of Information Systems and Informatics (publishedVersion, cc-by)
- DOAJ (DOAJ: Directory of Open Access Journals) (submittedVersion, cc-by-sa)
- Topics
- Social Sciences › Business, Management and Accounting › Management Information Systems › Information Technology Governance and Strategy
- Social Sciences › Political Science and International Relations › E-Government and Public Services
- Physical Sciences › Computer Science › Information Systems › Information and Cyber Security
- Keywords
- IT governance, COBIT 2019, public sector IT, service continuity, data security, IT governance maturity, civil service police, Satpol PP, Central Lombok, resource-constrained organizations, risk management, process automation, real-time monitoring, compliance
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
A language model drew the claims from the paper on 2026-11-07, under version 3 of the claim definition (model deepseek-v4.1-flash, prompt extract-v3).
A second model labelled each claim on 2026-11-07 (model jev-1.13-20260917, definition revision gold-guideline-v0.2).
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
