

A Role-Based Access Control Model in Modbus SCADA Systems. A Centralized Model Approach
Open accessThe DOI matches its Crossref record; 27 of the 29 references it cites were found in a registry or an index.
Abstract
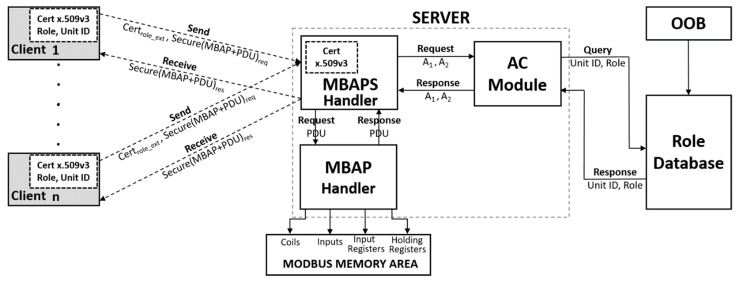
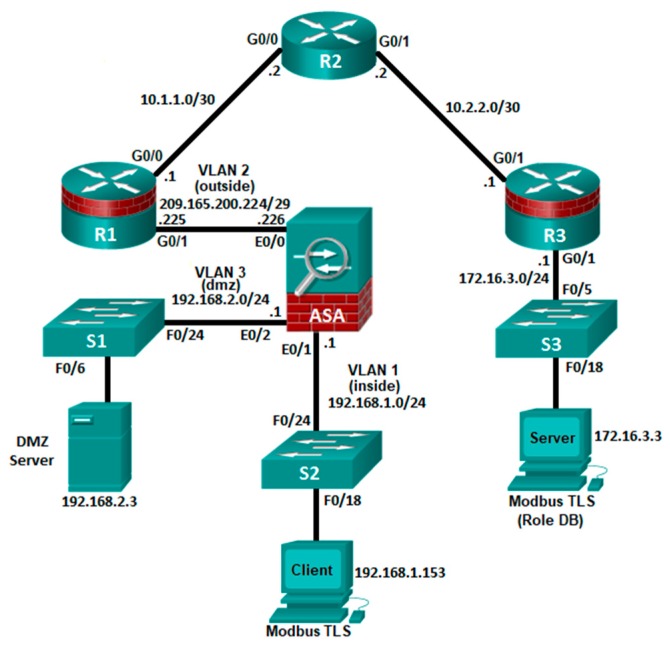
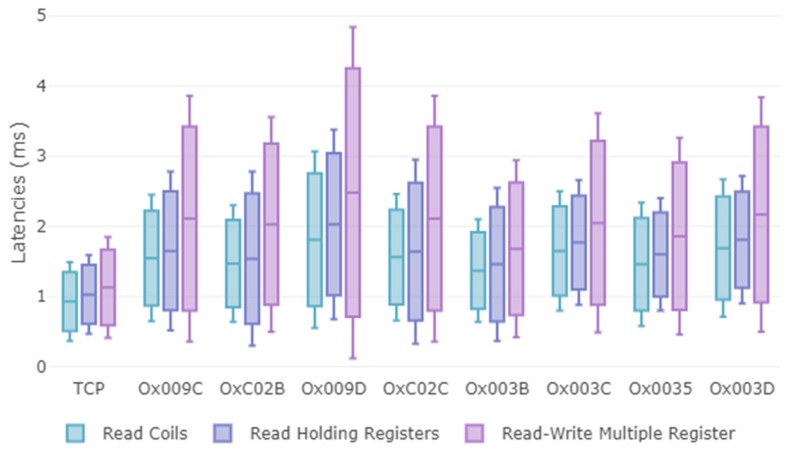
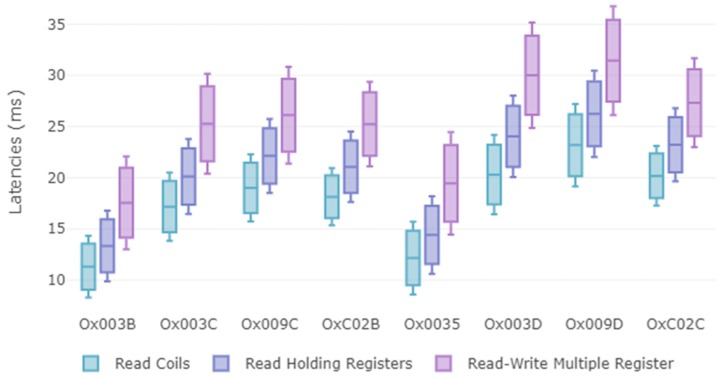
Industrial Control Systems (ICS) and Supervisory Control systems and Data Acquisition (SCADA) networks implement industrial communication protocols to enable their operations. Modbus is an application protocol that allows communication between millions of automation devices. Unfortunately, Modbus lacks basic security mechanisms, and this leads to multiple vulnerabilities, due to both design and implementation. This issue enables certain types of attacks, for example, man in the middle attacks, eavesdropping attacks, and replay attack. The exploitation of such flaws may greatly influence companies and the general population, especially for attacks targeting critical infrastructural assets, such as power plants, water distribution and railway transportation systems. In order to provide security mechanisms to the protocol, the Modbus organization released security specifications, which provide robust protection through the blending of Transport Layer Security (TLS) with the traditional Modbus protocol. TLS will encapsulate Modbus packets to provide both authentication and message-integrity protection. The security features leverage X.509v3 digital certificates for authentication of the server and client. From the security specifications, this study addresses the security problems of the Modbus protocol, proposing a new secure version of a role-based access control model (RBAC), in order to authorize both the client on the server, as well as the Modbus frame. This model is divided into an authorization process via roles, which is inserted as an arbitrary extension in the certificate X.509v3 and the message authorization via unit id, a unique identifier used to authorize the Modbus frame. Our proposal is evaluated through two approaches: A security analysis and a performance analysis. The security analysis involves verifying the protocol’s resistance to different types of attacks, as well as that certain pillars of cybersecurity, such as integrity and confidentiality, are not compromised. Finally, our performance analysis involves deploying our design over a testnet built on GNS3. This testnet has been designed based on an industrial security standard, such as IEC-62443, which divides the industrial network into levels. Then both the client and the server are deployed over this network in order to verify the feasibility of the proposal. For this purpose, different latencies measurements in industrial environments are used as a benchmark, which are matched against the latencies in our proposal for different cipher suites.
Overview
The claims and statistics of this paper haven’t been checked yet.
Free: it reads the open-access text and checks the first 5 claims that cite a source we can check. Create a free account to check every claim.
Integrity signals
Registry
Cites
Statistics
Figures
Verification
Claims the paper makes
The claims and statistics of this paper haven’t been checked yet.
Free: it reads the open-access text and checks the first 5 claims that cite a source we can check. Create a free account to check every claim.
Claims other papers make about this one
Each is checked against this paper’s own text: does it say what the citing paper says it does?
The cited source says what the claim attributes to it.
In the citing paper
“However, because it is widespread in the industry, the option to provide security to the protocol is a solution that many organizations are likely to adopt [13].”
From Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported (2022) · cites this paper as [13]
In the citing paper
“Cyber-security measures have not been implemented in the proposal so far; nonetheless, measures in this regard for vulnerabilities of the Modbus TCP network should be taken into account [55].”
From Innovative Multi-Layered Architecture for Heterogeneous Automation and Monitoring Systems: Application Case of a Photovoltaic Smart Microgrid (2021) · cites this paper as [55]
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
The self-check needs the paper’s full text.
Citations
Cites
The Transport Layer Security (TLS) Protocol Version 1.3
Rescorla, E. (2018) · doi:10.17487/rfc8446 · Cited by 1,897
Guide to Industrial Control Systems (ICS) Security
Stouffer, K., Pillitteri, V., Lightman, S., Abrams, M., & Hahn, A. (2015) · doi:10.6028/nist.sp.800-82r2 · Cited by 1,377
Turner, S. (2014) · IEEE Internet Computing · doi:10.1109/mic.2014.126 · Cited by 452
Attack taxonomies for the Modbus protocols
Huitsing, P., Chandia, R., Papa, M., & Shenoi, S. (2008) · International Journal of Critical Infrastructure Protection · doi:10.1016/j.ijcip.2008.08.003 · Cited by 249 · cited 2×
“The same work ([18]) identifies several taxonomies, divided into the serial transmission mode and Modbus TCP / IP protocol.”
BackgroundMethodAn experimental investigation of malware attacks on SCADA systems
Fovino, I. N., Carcano, A., Masera, M., & Trombetta, A. (2009) · International Journal of Critical Infrastructure Protection · doi:10.1016/j.ijcip.2009.10.001 · Cited by 133
OpenPLC: An open source alternative to automation
Rodrigues Alves, T., Buratto, M., de Souza, F. M., & Rodrigues, T. V. (2014) · IEEE Global Humanitarian Technology Conference (GHTC 2014) · doi:10.1109/ghtc.2014.6970342 · Cited by 114 · cited 1×
“In addition, at the Defconf security conference in 2018, a study was presented where an injection attack was made upon three types of PLC (one Modicon, another Allen-Bradley and the third based on an open source PLC, known as OpenPLC [8]) which supported the Modbus protocol.”
A computational interpretation of Dolev–Yao adversaries
Herzog, J. C. (2005) · Theoretical Computer Science · doi:10.1016/j.tcs.2005.03.003 · Cited by 72 · cited 1×
“The attacker model used is the classic Dolev-Yao [31].”
MethodFigueroa-Lorenzo, S., Añorga, J., & Arrizabalaga, S. (2019) · Computers · doi:10.3390/computers8030057 · Cited by 70 · cited 1×
“Since one of our lines of research is access control, based on attributes (ABAC) in decentralized systems ([40,41]) and this model of access control based on roles (RBAC) has been applied in a centralized environment (Role Database), the first future line of research is to apply this model in a…”
MethodSelf-citationStandards landscape and directions for smart manufacturing systems
Lu, Y., Morris, K. C., & Frechette, S. (2015) · 2015 IEEE International Conference on Automation Science and Engineering (CASE) · doi:10.1109/coase.2015.7294229 · Cited by 66 · cited 2×
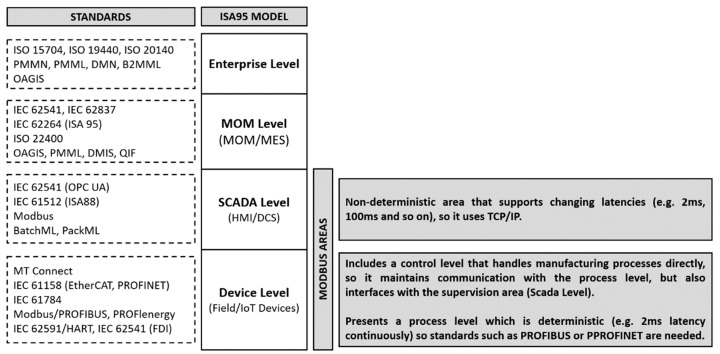
“cti fiel s f s ase t e I 95 el a relate sta ar s [3,4].”
BackgroundMethodHayes, G., & El-Khatib, K. (2013) · 2013 Third International Conference on Communications and Information Technology (ICCIT) · doi:10.1109/iccitechnology.2013.6579545 · Cited by 65 · cited 1×
“A solution based on SCTP (Stream Control Transmission Protocol) and HMAC (Hash-based Message Authentication Code) named ModbusSec, is presented by the reference [23].”
Method
Research works printed but not linked: 1
- Bullema, J.E. (2019, July 22). Available online: https://www.researchgate.net/publication/321770622_2017_-_Bullema_-_Smart_Manufacturing_-_not_only_for_greenfield_high_tech_factories.
Cited by
Innovation and challenges of artificial intelligence technology in personalized healthcare
Li, Y.-H., Li, Y.-L., Wei, M.-Y., & Li, G.-Y. (2024) · Scientific Reports · doi:10.1038/s41598-024-70073-7 · Cited by 275
“A combination of technical and organizational measures can be employed to tackle these issues, including data encryption, access control, and data breach prevention and response planning 42 .”
BackgroundKayes, A. S. M., Kalaria, R., Sarker, I. H., Islam, M. S., Watters, P., Ng, A., Hammoudeh, M. A. A., Badsha, S., & Kumara, I. (2020) · Sensors · doi:10.3390/s20092464 · Cited by 143
“Recently, a new secure version of an RBAC approach has also been introduced [70].”
A Survey of IIoT Protocols: A Measure of Vulnerability Risk Analysis Based on CVSS
Figueroa-Lorenzo, S., Añorga, J., & Arrizabalaga, S. (2021) · ACM Computing Surveys · doi:10.1145/3381038 · Cited by 89
“In addition, Reference [207], addresses the security problems of the Modbus protocol, through a new secure version of a RBAC model, which takes advantage of the authentication provided by TLS, as well as granting authorization of the client on the server, as well as of the Modbus frame.”
Self-citationGonzález, I., Calderón, A. J., & Portalo, J. M. (2021) · Sustainability · doi:10.3390/su13042234 · Cited by 90
“Cyber-security measures have not been implemented in the proposal so far; nonetheless, measures in this regard for vulnerabilities of the Modbus TCP network should be taken into account [55].”
BackgroundContainer-based Virtualization for Real-time Industrial Systems—A Systematic Review
Queiroz, R., Cruz, T., Mendes, J., Sousa, P., & Simões, P. (2023) · ACM Computing Surveys · doi:10.1145/3617591 · Cited by 84
“There are also indicative values for the end-to-end latency [ 23 ]—as shown in Table 1 —from which the deadlines can be gauged.”
BackgroundMulti-Points Indoor Air Quality Monitoring Based on Internet of Things
Liu, Z., Wang, G., Zhao, L., & Yang, G. (2021) · IEEE Access · doi:10.1109/access.2021.3073681 · Cited by 82
“Modbus is a field bus protocol in the field of industrial communication, which has been widely used in various industrial occasions since 1979 [25].”
BackgroundEnhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported
Martins, T., & Oliveira, S. V. G. (2022) · Sensors · doi:10.3390/s22208024 · Cited by 45
“However, because it is widespread in the industry, the option to provide security to the protocol is a solution that many organizations are likely to adopt [13].”
Polat, O., Ahmad, A. A., Oyucu, S., Algül, E., Doğan, F., & Aksöz, A. (2025) · IEEE Access · doi:10.1109/access.2025.3577761 · Cited by 47
“However, security systems have been deemed inadequate because they have revealed security vulnerabilities that contradict the requirements [21], [22].”
de Brito, I. B., & de Sousa, R. T. (2022) · Applied Sciences · doi:10.3390/app12157942 · Cited by 39
“S. Figueroa-Lorenzo et al., 2019 [13], in order to test their proposal to improve the security of the Modbus protocol, have built a virtual testbed, containing TCP/IP software network elements (firewall, routers and switches) made available by Cisco for use in the network simulator GNS3.”
Gaffurini, M., Bellagente, P., Depari, A., Flammini, A., Sisinni, E., & Ferrari, P. (2024) · IEEE Transactions on Instrumentation and Measurement · doi:10.1109/tim.2024.3370746 · Cited by 34
Găitan, V. G., & Zagan, I. (2021) · Sensors · doi:10.3390/s21010246 · Cited by 30
“Scientific papers related to Modbus refer in particular to Modbus TCP/IP addressing issues related to the following, among others: use as a support for communication in distributed applications [4] (mostly SCADA [2]), the implementation of access gateways (for remote connection using a TCP/IP protocol stack [5] and wi…”
BackgroundInfluentialModbus Access Control System Based on SSI over Hyperledger Fabric Blockchain
Figueroa-Lorenzo, S., Añorga, J., & Arrizabalaga, S. (2021) · Sensors · doi:10.3390/s21165438 · Cited by 33
“For instance, this approach provides Modbus with trusted identity and mutual authentication based on X.509 certificates, as well as secure authorization based on a Role-based Access Control (RBAC) [2].”
BackgroundSelf-citationA secure revocable fine-grained access control and data sharing scheme for SCADA in IIoT systems
Zhang, W., Zhang, H., Fang, L., Liu, Z., & Ge, C. (2022) · IEEE Internet of Things Journal · doi:10.1109/jiot.2021.3091760 · Cited by 26
“However, the generality of these works [6]–[8] is weak.”
BackgroundMethodAutomatic Hybrid Access Control in SCADA-Enabled IIoT Networks Using Machine Learning
Usman, M., Sarfraz, M. S., Habib, U., Aftab, M. U., & Javed, S. (2023) · Sensors · doi:10.3390/s23083931 · Cited by 27
“The authors of [25] considered the security issues of the Modbus, protocol which is used by most SCADA applications, and proposed a secure RBAC model to provide authorization to the client, as well as the Modbus frame.”
MethodZagan, I., & Găitan, V. G. (2022) · Mathematics · doi:10.3390/math10244686 · Cited by 21
Mughaid, A. S., AlZu’bi, S. M. F., Alkhatib, A. A., AlZioud, A., Ghazo, A. T. A., & Al-Aiash, I. (2025) · Simulation Modelling Practice and Theory · doi:10.1016/j.simpat.2025.103078 · Cited by 19
Yang, Y.-S., Lee, S., Chen, W.-C., Yang, C.-S., Huang, Y.-M., & Hou, T.-W. (2021) · Sensors · doi:10.3390/s21082685 · Cited by 24
“The authors of [30] proposed a Role-Based Access Control (RBAC) model that integrates TLS and X.”
BackgroundPLC Cyber-Security Challenges in Industrial Networks
Ramirez, R., Chang, C.-K., & Liang, S.-H. (2022) · IEEE/ASME International Conference on Mechatronic and Embedded Systems and Applications · doi:10.1109/mesa55290.2022.10004463 · Cited by 19
“The authors proposed a new secure version of the Modbus protocol, where a central architecture design authorizes the client, server, and its Modbus frame[7].”
BackgroundAttack tree Model for Potential Attacks Against the SCADA System
Aldahasi, E., & Saqib, B. N. A. (2019) · Telecommunications Forum (TELFOR) · doi:10.1109/telfor48224.2019.8971181 · Cited by 15
“Sub-Function Codes of Diagnostic Function [16].”
PLC Cybersecurity Test Platform Establishment and Cyberattack Practice
Ramirez, R., Chang, C.-K., & Liang, S.-H. (2023) · Electronics · doi:10.3390/electronics12051195 · Cited by 21
ISA 100.11a Networked Control System Based on Link Stability
Florêncio, H. M., Neto, A. D. D., & Martins, D. (2020) · Sensors · doi:10.3390/s20185417 · Cited by 12
“, between sensors, actuators and PLCs [39,40].”
Tolbert, C. L. (2025) · NDT · doi:10.3390/ndt3020007 · Cited by 12
“It is important to note that PLCs and DCSs can be the center of both collection and transformation through the ML techniques noted earlier or can serve as a bridge to a tertiary system [16].”
Investigation of Secure Communication of Modbus TCP/IP Protocol: Siemens S7 PLC Series Case Study
Dao, Q.-T., Nguyen, L.-T., Ha, T.-K., Nguyen, V., & Nguyen, T. A. (2025) · Applied System Innovation · doi:10.3390/asi8030065 · Cited by 12
“This protocol supports Public Key Infrastructure for authentication and confidentiality, and introduces Role-Based Access Control through X.509v3 certificates [13,14].”
Intelligent Access Control Design for Security Context Awareness in Smart Grid
Kim, H., & Choi, J. (2021) · Sustainability · doi:10.3390/su13084124 · Cited by 12
Modbus Extension Server Implementation for BIoT-Enabled Smart Switch Embedded System Device
Găitan, V. G., & Zagan, I. (2024) · Sensors · doi:10.3390/s24020475 · Cited by 11
“…technological developments driven by the rapid development of the IoT, wired and wireless communication networks, the extensions of communication protocols such as Modbus [1–3], touch screen technologies, LCD, microcontroller performance [4], and the use of cloud computing (CC) and smartphones.”
BackgroundA Framework for Communicating and Building a Digital Twin Model of the Electric Car
Bednarz, T. P., Baier, A., & Paprocka, I. (2024) · Applied Sciences · doi:10.3390/app14051776 · Cited by 11
“FC16—write multiple registers.”
Testing the limits of general-purpose hypervisors for real-time control systems
Queiroz, R., Cruz, T., & Simões, P. (2023) · Microprocessors and Microsystems · doi:10.1016/j.micpro.2023.104848 · Cited by 10
Zhao, S., Zhang, Q., Zhao, Q., Zhang, X., Guo, Y., Lu, S., Song, L., & Zhao, Z. (2025) · Sensors · doi:10.3390/s25133861 · Cited by 10
“…protocols such as Open Platform Communications Unified Architecture (OPC UA) and Message Queuing Telemetry Transport (MQTT), Modbus continues to play a pivotal role at the field level, particularly for the large installed base of legacy PLCs and remote I/O devices that remain in operation [5].”
Detecting Flooding Attacks in Communication Protocol of Industrial Control Systems
Rajesh, L., & Satyanarayana, P. (2020) · International Journal of Advanced Computer Science and Applications · doi:10.14569/ijacsa.2020.0110149 · Cited by 10
Operational Simulation Environment for SCADA Integration of Renewable Resources
Larios, D. F., Personal, E., Parejo, A., García, S., García, A., & León, C. (2020) · Energies · doi:10.3390/en13061333 · Cited by 11
“A special mention should be given to OPC-UA, an interesting secure [44] platform for Industry 4.”
BackgroundSecurity, Privacy, and Trustworthiness of Sensor Networks and Internet of Things
Katsikas, S. K., & Gkioulos, V. (2020) · Sensors · doi:10.3390/s20143846 · Cited by 10
“In [5], entitled “A Role-Based Access Control Model in Modbus SCADA Systems.”
BackgroundCanaan, B., Makhlouf, Y., & Abdeslam, D. O. (2025) · Energy Conversion and Management X · doi:10.1016/j.ecmx.2025.101406 · Cited by 18
Role and Object Domain-Based Access Control Model for Graduate Education Information System
Jin, G., Wang, D., Yang, D., Hong, D., Dong, Q., & Wang, Y. (2020) · Procedia Computer Science · doi:10.1016/j.procs.2020.09.133 · Cited by 9
Securing IoT Devices Using Generative AI Techniques
Khan, A., Jhanjhi, N. Z., Abdulhabeb, G. A. A., Ray, S. K., Ghazanfar, M. A., & Humayun, M. (2024) · Advances in information security, privacy, and ethics book series · doi:10.4018/979-8-3693-5415-5.ch007 · Cited by 7
Rajawat, A. S., Rawat, R., & Barhanpurkar, K. (2022) · Wiley eBooks · doi:10.1002/9781119795667.ch14 · Cited by 6
Kholidy, H. A. (2021) · arXiv (Cornell University) · doi:10.48550/arxiv.2112.14137 · Cited by 6
Bridging Theory and Practice: Addressing Current Cybersecurity Gaps in Industry 5.0
Sheikhi, S., Eceiza, M., Arellano, C., López, O. G., Kelnberger, S., Lindner, R., Partanen, J. O., & Lovén, L. (2025) · IEEE Access · doi:10.1109/access.2025.3569130 · Cited by 6
“This approach enables organizations to enforce granular access controls based on predefined roles, enhancing the security of industrial networks and SCADA systems [7].”
Attribute Based Access Control Model for Protecting Programmable Logic Controllers
Gowdanakatte, S., Ray, I., & Houmb, S. H. (2022) · ACM Workshop on Secure and Trustworthy Cyber-Physical Systems (SaT-CPS) · doi:10.1145/3510547.3517926 · Cited by 7
Methodology for Assessing Existing Vulnerabilities in Modbus Protocol
Rashid, M., Singh, Y. P., & Manzoor, S. I. (2025) · Procedia Computer Science · doi:10.1016/j.procs.2025.04.154 · Cited by 3
PLC Protection System Based on Verification Separation
Pan, X., Li, H., Li, X., Xu, L. J., & Sun, Y. (2021) · Computers, materials & continua/Computers, materials & continua (Print) · doi:10.32604/cmc.2022.021020 · Cited by 3
A Blockchain-Based Access Control Scheme for Reputation Value Attributes of the Internet of Things
Tian, H., & Tian, J. (2024) · Computers, materials & continua/Computers, materials & continua (Print) · doi:10.32604/cmc.2024.047058 · Cited by 3
A Desktop Review of Security Techniques Applicable for Optimised Water Network
Namukuwa, R., Chitauro, M., & Shava, F. B. (2021) · International Multidisciplinary Information Technology and Engineering Conference (IMITEC) · doi:10.1109/imitec52926.2021.9714530 · Cited by 2
Data Communication Based on MQTT in a Polymer Extrusion Process
Kim, J. H., Moon, S. H., Ryu, J. S., & Kim, S. K. (2022) · Journal of Visualized Experiments · doi:10.3791/63717 · Cited by 2
Fine-Grained Access Control Mechanism of Energy Internet
Miao, S., ZHANG, X., & Zhe, L. I. U. (2022) · Wuhan University Journal of Natural Sciences · doi:10.1051/wujns/2022273231 · Cited by 2
A Scada system used for monitoring virtual chemical plants via Modbus communication
de Miranda, T. D. C. R. D., & Santos, L. D. S. (2024) · Internet Technology Letters · doi:10.1002/itl2.495 · Cited by 1
Găitan, N. C., Zagan, I., & Găitan, V. G. (2026) · The Journal of Supercomputing · doi:10.1007/s11227-025-08207-5 · Cited by 1
“For example, a typical Human–Machine Interface (HMI) or Supervisory Control and Data Acquisition (SCADA) application implements a client service to initiate communications with Programmable Logic Controllers (PLCs) and other devices to interrogate systems and collect data [9, 10].”
Kumar, V., & Jain, P. (2026) · IGI Global eBooks · doi:10.4018/979-8-3373-3531-5.ch009 · Cited by 1
Rajesh, L., & Satyanarayana, P. (2022) · Lecture notes in electrical engineering · doi:10.1007/978-981-16-7985-8_27 · Cited by 1
Towards decentralized and scalable architectures for Access Control Systems in IIoT environments
Figueroa-Lorenzo, S., Arrizabalaga, S., & Añorga, J. (2021) · Colección Jornadas y congresos · doi:10.18239/jornadas_2021.34.33
Self-citationResearch on database controlled memory authorization application model based on ARM architecture
Shen, W., Zhang, I., & Shen, G. (2021) · IEEE International Conference on Artificial Intelligence and Industrial Design (AIID) · doi:10.1109/aiid51893.2021.9456582
“The following is an example of executing automatic revocation operation for revoking advanced privilege DM, and the scheme is as follows [20].”
MethodIndustrial control system software patterns in manufacturing
Valiev, R. A., & Khuzyatov, S. S. (2020) · IOP Conference Series Materials Science and Engineering · doi:10.1088/1757-899x/915/1/012056
SCADA Authentication Identification Over The Next Generation CyberNetPreprint
Mughaid, A. S., AlZu’bi, S. M. F., AlZioud, A., & Ghazo, A. T. A. (2022) · Research Square · doi:10.21203/rs.3.rs-2364360/v1
Blockchain-Based Social Network Access Control Mechanism
Dai, M., Li, Y., Wen, Y., Liu, D., & Chen, H. (2022) · Communications in computer and information science · doi:10.1007/978-981-19-8043-5_11
Hybrid control system: Integration of sensors and controllers using MQTT and Modbus-RT
Sokołov, O., Malaga, M., Raška, P., Соколов, С. В., & Leontiev, P. (2024) · Průmyslové inženýrství · doi:10.24132/pi.2024.12594.078-087
Trezza, N., Makrakis, G. M., & Roberson, D. (2025) · IT Professional · doi:10.1109/mitp.2024.3502436
Intelligent Building Management: Leveraging AI and VAV for Sustainable HVAC Performance
Samuji, S. N. A. B., Bohari, Z. H., Azhuan, N. A. N., Sulaima, M. F., Jali, M. H., Abdullah, A. Z., Isa, M., & Soh, P. J. (2026) · International Journal of Research and Innovation in Social Science · doi:10.47772/ijriss.2026.100300445
Artificial intelligence and antiaging research
Arumugam, S., Muthuvel, R., Antony, B. S., Chandrasekaran, K., & Subbaraj, G. K. (2026) · Elsevier eBooks · doi:10.1016/b978-0-443-33159-6.00009-6
Abu-Alzanat, T., Alieyan, K., Qutaibah, A., & Alassar, S. (2025) · International Conference on Engineering and Computing Technologies (EngiTek) · doi:10.1109/engitek68245.2025.11567628
“In addition, the study by Figueroa-Lorenzo et al. (2019) A centralized model of access control objectives within Modbus SCADA systems, but focused on static security without dealing with any dynamic threats [12].”
Privacy-preserving SCADA systems: a hybrid encryption approach
Guo, X., & Zhao, D. (2026) · The Journal of Supercomputing · doi:10.1007/s11227-026-08823-9
de Lima, S. B., & da Rocha, S. D. (2026) · Revista Tópicos. · doi:10.70773/revistatopicos/789008512
de Brito, I. B. (2022) · RIUnB Institutional Repository (University of Brasília) · doi:10.26512/2022.11.d.45788
Phiri, L., & Kamutumwa, M. (2026) · International Journal of Applied Mathematics Computational Science and Systems Engineering · doi:10.37394/232026.2026.8.16
ENCRYPTED ONLINE EXAMINATION QUESTION PAPER DISTRIBUTION WITH ROLE-BASED ACCESS CONTROL
Chamanthula, R. G. A. (2026) · American Journal of AI Digital Transformation and Regenerative Pharmacist · doi:10.64751/j4ps1w02
Navigating Security Risks in Large-Scale Data Handling: A Big Data and Mis Perspective
Asha, N. B. (2024) · Letters in High Energy Physics
Gupta, M. K., Sharma, A., Sahoo, S. R., & Chaturvedi, S. (2026) · Electric Power Systems Research · doi:10.1016/j.epsr.2026.114289
Metadata
- Authors
- Figueroa-Lorenzo, S., Añorga, J., & Arrizabalaga, S.
- Affiliations
- Centro de Estudios e Investigaciones Técnicas de Gipuzkoa (ES)
- Corresponding author
- Figueroa-Lorenzo, Santiago
- Venue
- Sensors
- Publisher
- MDPI AG
- Published
- 2019-10-14
- Volume
- 19
- Issue
- 20
- Pages
- 4455
- ISSN
- 1424-8220 (ISSN-L)
- PMC
- PMC6832255
- OpenAlex
- W2980075564
- Cited by
- 58
- References
- 29
- Citations by year
- 2026: 6 · 2025: 9 · 2024: 7 · 2023: 4 · 2022: 11 · 2021: 11 · 2020: 8 · 2019: 2
- FWCI
- 4.43
- Type
- journal article
- Language
- en
- Open access
- gold
- dx.doi.org
- Licence
- Locations
- Sensors (publishedVersion, cc-by)
- Europe PMC (PubMed Central) (publishedVersion, cc-by)
- PubMed Central (publishedVersion, cc-by)
- PubMed (publishedVersion)
- Deposito Adademico Digital Universidad De Navarra (University of Navarra) (submittedVersion, cc-by)
- DOAJ (DOAJ: Directory of Open Access Journals) (submittedVersion, cc-by-sa)
- Topics
- Physical Sciences › Engineering › Control and Systems Engineering › Smart Grid Security and Resilience
- Physical Sciences › Computer Science › Computer Networks and Communications › Access Control and Trust
- Physical Sciences › Computer Science › Computer Networks and Communications › Advanced Authentication Protocols Security
- Keywords
- Modbus, role-based access control, SCADA security, industrial control systems, IEC 62443, man-in-the-middle attacks, replay attacks, eavesdropping, network latency, critical infrastructure security
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
Data sources
Bibliographic data: Semantic Scholar, OpenAlex, Crossref.
Contains information from the Semantic Scholar Academic Graph Datasets, made available under the ODC Attribution License (ODC-BY 1.0).
Semantic Scholar’s data is described in: Kinney, R., et al. (2023). The Semantic Scholar Open Data Platform. arXiv:2301.10140.
