

Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported
Open accessThe DOI matches its Crossref record; 19 of the 19 references it cites were found in a registry or an index; 4 of the 24 sources its claims cite were checked for support.
Abstract
The Zero Trust concept is being adopted in information technology (IT) deployments, while human users remain to be the main risk for operational technology (OT) deployments. This article proposes to enhance the new Modbus/TCP Security protocol with authentication and authorization functions that guarantee security against intentional unauthorized access. It aims to comply with the principle of never trusting the person who is accessing the network before carrying out a security check. Two functions are tested and used in order to build an access control method that is based on a username and a password for human users with knowledge of industrial automation control systems (IACS), using simple means, low motivation, and few resources. A man-in-the-middle (MITM) component was added in order to intermediate the client and the server communication and to validate these functions. The proposed scenario was implemented using the Node-RED programming platform. The tests implementing the functions and the access control method through the Node-RED software have proven their potential and their applicability.
Overview
CoChat Summary
TL;DR
The paper proposes enhancing the Modbus/TCP Security protocol with two user-defined functions for authentication and authorization to build access control for human users. Tests implemented in Node-RED show role-based read/write permissions and rejection of unknown users, supporting IEC 62443-4-2 security level 1.
Key findings
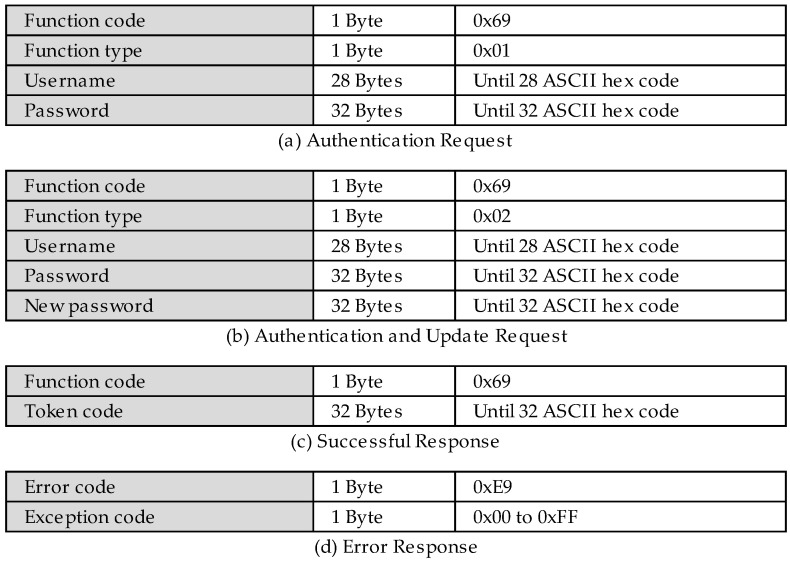
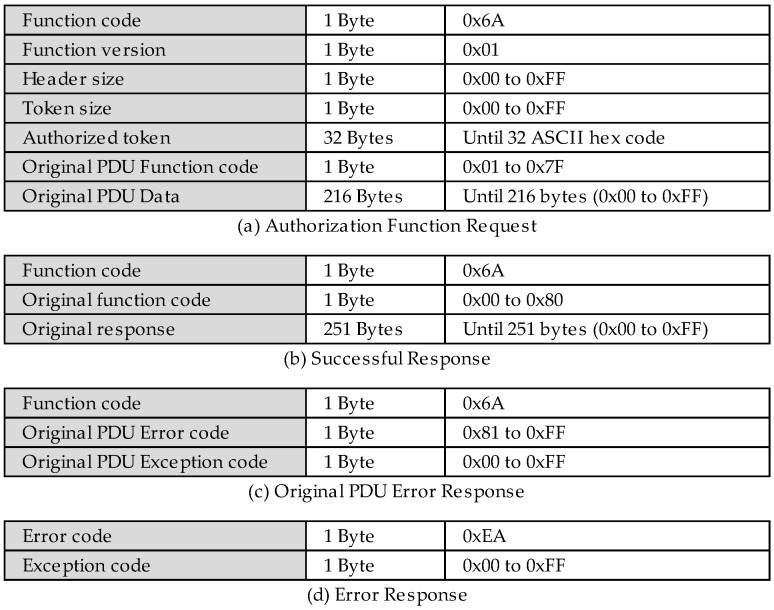
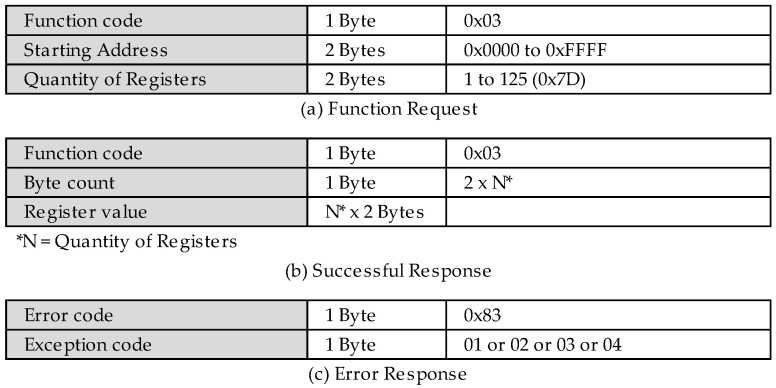
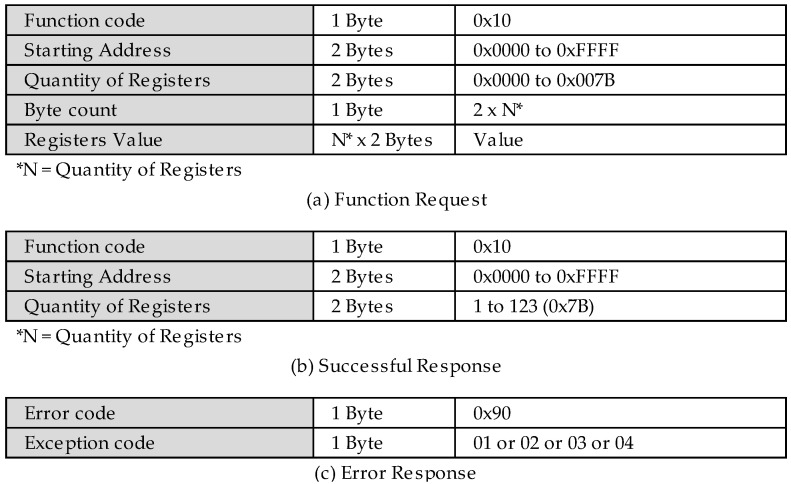
- Two new user-defined functions are proposed: authentication with function code 0x69, using a 28-byte username and 32-byte password and returning a 32-byte token, and authorization with function code 0x6A, which encapsulates the original Modbus PDU limited to 216 bytes and uses the token to identify the user.
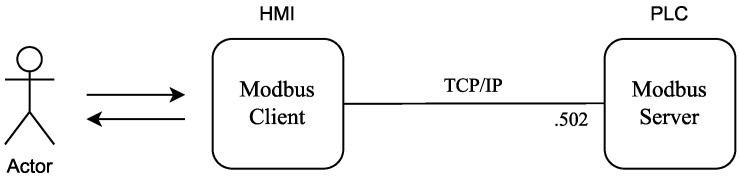
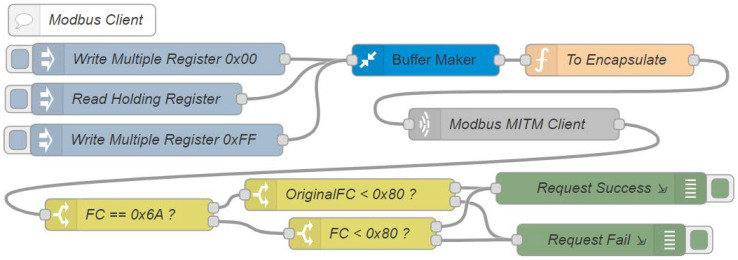
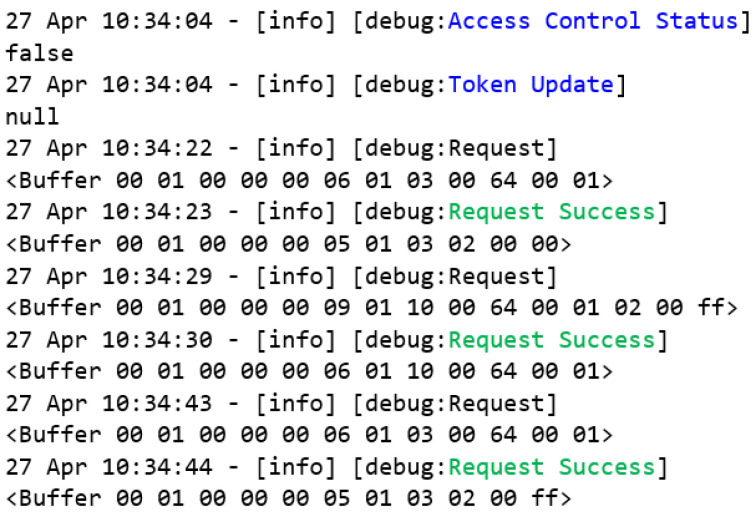
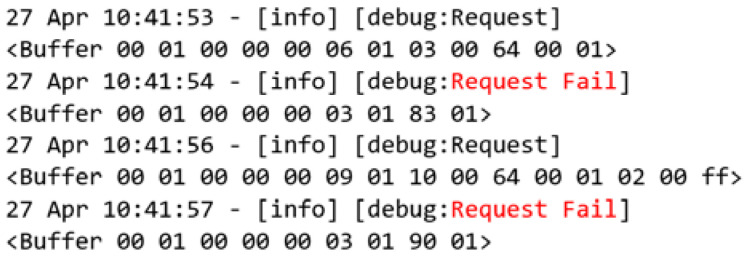
- In Node-RED tests, with access control disabled, read and write requests to register 0x64 succeeded, changing the value from 0x00 to 0xFF; with access control enabled, public read and write requests were denied with an illegal function exception.
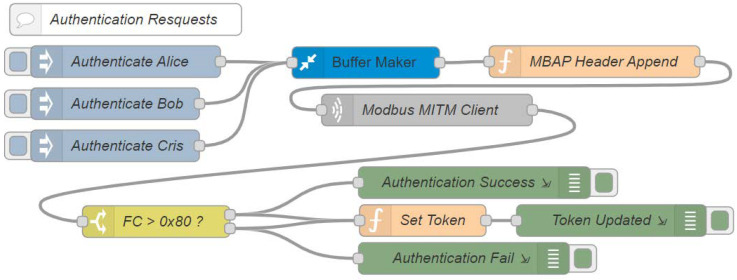
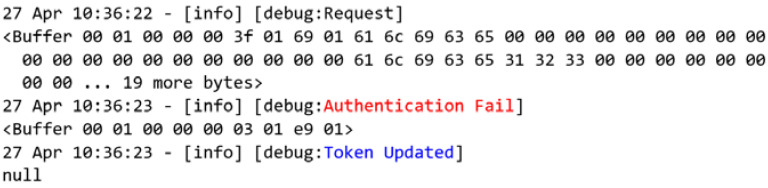
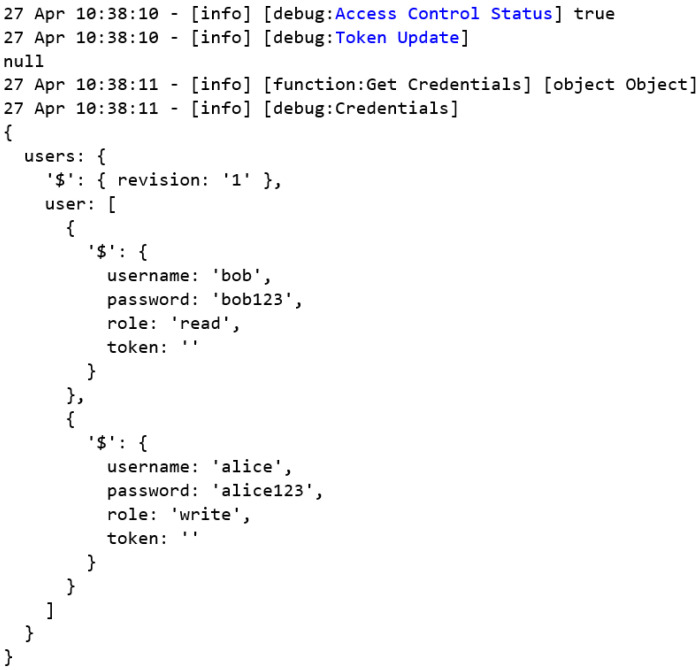
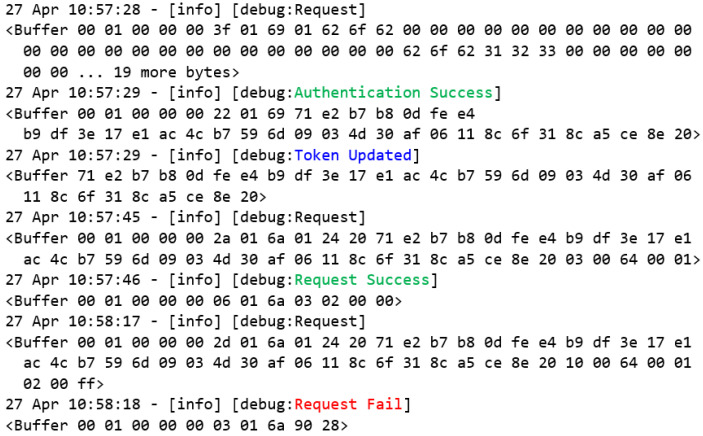
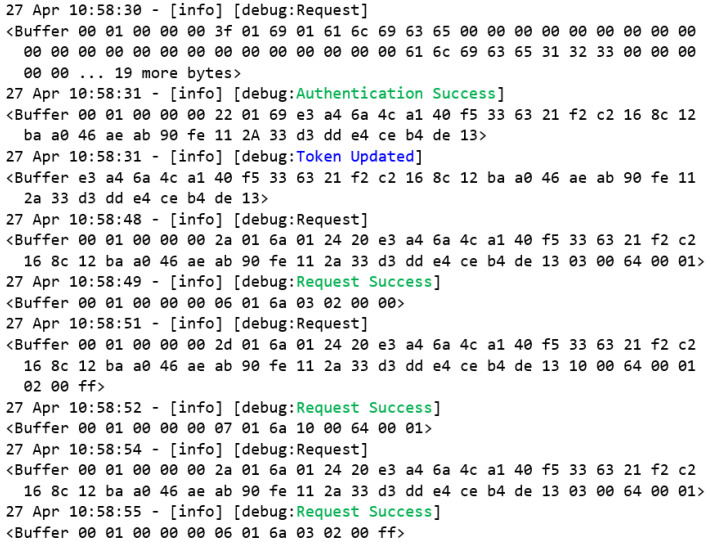
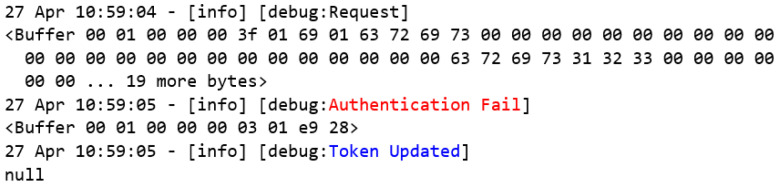
- Role segmentation was demonstrated: user Bob (read-only) authenticated and read successfully but had a write request denied; user Alice (read/write) authenticated and both read and wrote successfully, changing register 0x64 to 0xFF; user Cris (unknown) received an authentication exception and the global token was forced to null.
- The authors state the implementation evidences applicability for constructing access control that allows level one of maturity under IEC 62443-4-2, covering authentication (FR 1) and usage control (FR 2), against casual unauthorized users with generic IACS knowledge, simple means, few resources, and low motivation.
Methods
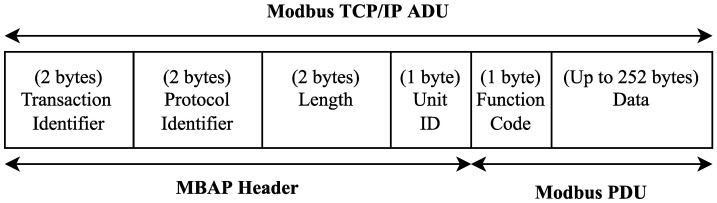
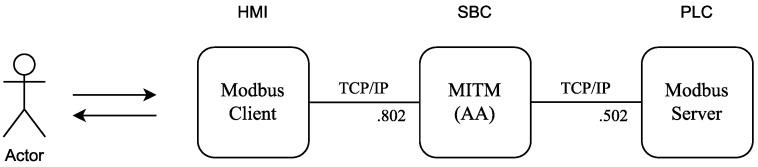
- Design: the Modbus/TCP Security protocol is enhanced with two user-defined functions—authentication (0x69) and authorization (0x6A)—and a man-in-the-middle (MITM) component intermediates client–server communication to validate these functions.
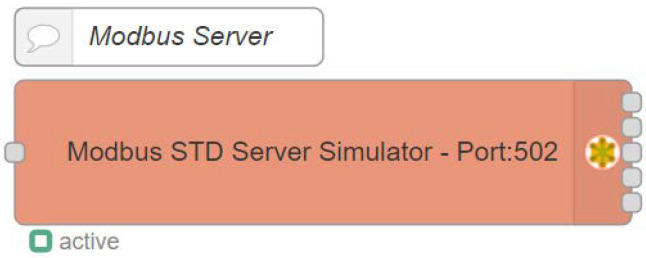
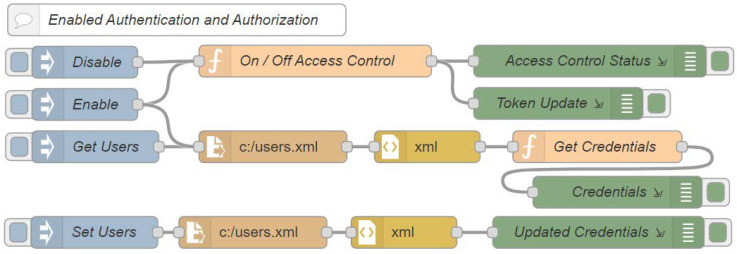
- Implementation and sample: the proposed scenario was simulated using the Node-RED programming platform, with a Modbus server on TCP port 502, a Modbus client, and a MITM flow on TCP port 802; tests used register 0x64 and users Bob, Alice, and Cris.
- Main analysis: tests compared access control disabled versus enabled, exercised authentication and authorization requests, and verified read/write permissions and exception responses according to each user’s role.
Limitations
- The paper states that encryption and audit-relevant event storage were not applied in the tests because they were not considered of paramount importance for validating the developed functions; PKI certificates were not used during testing but are essential for the functions to work correctly and must support revocation or limited expiration.
- The paper states vulnerabilities: other device access interfaces must also be controlled, password-based authenticator secrecy can be compromised by sharing, policies must limit authenticator lifetime, and the implemented access control is vulnerable to actors with many resources and deep IACS knowledge; it recommends multifactor authentication, double approval for critical parameter changes, and other mitigations.
- The paper states that encapsulating the authorization function required limiting the original PDU to 216 bytes, so care must be taken not to apply the functions with PDUs that exceed this amount.
Model-written summary. Check it against the paper before relying on it.
Integrity signals
Registry
Cites
Statistics
Figures
Verification
Claims the paper makes
2 Valid · 2 Not valid · 14 Not checked · 30 Own results and interpretations
The cited sources that could be checked couldn’t confirm or dispute this claim.
In the paper
“because the vast majority of industrial communication protocols were not designed to ensure the cybersecurity of the communication between devices, making the access control mechanisms in industrial devices limited and unable to employ role-based access control (RBAC) concepts and protocols with authentication and authorization capabilities.”
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 1. Introduction
What the sources say
- Not matchedcites [7] Filkins, B., Wylie, D., and Dely, A.J. (SANSTM Institute, 2019). Sans 2019 State of ot/ics Cybersecurity Survey, SANSTM Institute.
Couldn’t be matched to a paper in Crossref, so it can’t be checked.
- Could not verifycites [8] Bassett, G., Hylender, C.D., Langlois, P., Pinto, A., and Widup, S. (2022, February 03). 2020 Data Breach Investigations Report. Verizon, 2020. Available online: https://www.verizon.com/business/resources/reports/2020-data-breach-investigations-report.pdf. sourceExperimental — accuracy not yet measured
The cited “Verizon: Data Breach Investigations Report 2020” has no available full-text snippets for either of two paper-scoped searches, so the attribution cannot be checked directly. An unscoped search found the claim’s wording in “Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported,” but its reported score is 0.477, below the threshold for a misattribution verdict. That passage also cites earlier work, so its presence does not establish that the Verizon item was not a source. (LLM, conf=0.68)
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Not matched
The sources with a verdict support this claim; the rest weren’t checked yet, have no full text we could read, or their verdicts aren’t rated yet.
In the paper
“However, both of these works do not consider the confidentiality requirement for Modbus messages, as they are usually implemented using cryptography, which is expensive and presents a considerable overhead that can affect the performance in real-time communication [15,16].”
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 1. Introduction
What the sources say
- Supportedcites [15] Fovino, I.N., Carcano, A., Masera, M., and Trombetta, A. (2009). Design and implementation of a secure modbus protocol. Critical Infrastructure Protection III, Proceedings of the International Conference on Critical Infrastructure Protection, Hanover, NH, USA, 23–25 March 2009, Springer. source
In “Secure Modbus Protocol,” the authors explicitly say their work does not consider confidentiality for Modbus messages. They also explain that encryption is expensive and can introduce overhead affecting real-time performance. This verdict concerns only this cited work, not the other work cited in the sentence. (LLM, conf=0.95)
- Not checked — no full text of the sourcecites [16] Hayes, G., and El-Khatib, K. (2013, January 19–21). Securing modbus transactions using hash-based message authentication codes and stream transmission control protocol. Proceedings of the 2013 Third International Conference on Communications and Information Technology (ICCIT), Beirut, Lebanon. source
plain- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Supported
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“Furthermore, the read and write requests to the register 0x64 can be successfully performed through the Modbus client flow.”
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 5. Tests
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper states — it cites no source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“In this first scenario (Figure 5), there is no control over the client’s requests, therefore, the Modbus server will successfully respond to all of the public requests that are made by the Modbus client for valid registers on the server.”
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 4. Implementation
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“The tests implementing the functions and the access control method through the Node-RED software have proven their potential and their applicability.”
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > Abstract
boostedstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Rests on an assumption not shown here.
11 more claims
Create a free account to see all 48 claims and every source verdict.
- Probably not a substantial claim. 18
- It may state two separate claims as one. 23
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
Each contradiction between two passages listed here was confirmed by an independent check.
Rated major: it would touch a result — a value a result rests on, reported and recomputed p-values on opposite sides of the significance level, two passages that conflict with no sign which is right, or a cited work retracted before this paper was published.
In the paper
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 3. Enhanced Modbus/TCP Security Protocol > 3.2. Authorization User-Defined Function
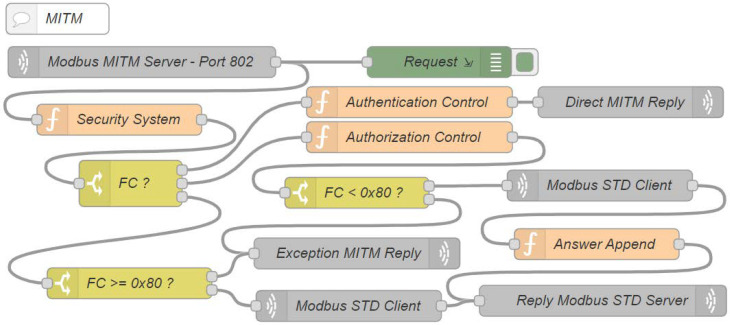
“if an exception occurs for the original function, or if the user does not have access permission for the given register, the function will return this exception encapsulated in a successful response frame that is performed by the new authorization function (Figure 3c).”
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 4. Implementation
“then it is evaluated whether the given user is authorized to perform the given request. In negative cases, an exception is raised, but for positive cases, the original function is decapsulated to proceed with the request. As can be seen, this node is connected exclusively with node FC < 0x80?, which evaluates whether the response from the authorization control node is an exception. If so, it forwards the message (Figure 3d)”
Rated minor: it would not touch a result — a value no result rests on, a p-value that stays on the same side of the significance level, or a conflict that is clerical, resolved elsewhere in the paper, or outside its own findings.
In the paper
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 4. Implementation
“For the system under analysis, the function code of the request is evaluated when the access control is disabled, and a non-public request arrives, so the function code is replaced by its respective exception code.”
§ Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported > 5. Tests
“Moreover, the MITM flow forwards this request to the Modbus server that does not understand the requested function, returning an exception, according to Figure 2d.”
Citations
Cites
Internet of Things: A Survey on Enabling Technologies, Protocols, and Applications
Al-Fuqaha, A., Guizani, M., Mohammadi, M., Aledhari, M., & Ayyash, M. (2015) · IEEE Communications Surveys & Tutorials · doi:10.1109/comst.2015.2444095 · Cited by 8,630 · cited 1×
“Of these, 37% will be generated by things in the manufacturing area and 7% will be generated by electricity-related things [1,2].”
A Unified Deep Learning Anomaly Detection and Classification Approach for Smart Grid Environments
Siniosoglou, I., Radoglou-Grammatikis, P., Efstathopoulos, G., Fouliras, P., & Sarigiannidis, P. (2021) · IEEE Transactions on Network and Service Management · doi:10.1109/tnsm.2021.3078381 · Cited by 266 · cited 1×
“The intrusion detection system (IDS) for smart grid is presented in [24,25].”
Verizon: Data Breach Investigations Report 2020
(2020) · Computer Fraud & Security · doi:10.1016/s1361-3723(20)30059-2 · Cited by 189
Design and Implementation of a Secure Modbus Protocol
Fovino, I. N., Carcano, A., Masera, M., & Trombetta, A. (2009) · IFIP Advances in Information and Communication Technology · doi:10.1007/978-3-642-04798-5_6 · Cited by 138 · cited 2×
“A solution using integrity mechanisms through the SHA2 algorithm, authentication through RSA, and non-repudiation and anti-replay through the timestamp is presented in [15].”
AAA protocols: authentication, authorization, and accounting for the Internet
Metz, C. (1999) · IEEE Internet Computing · doi:10.1109/4236.807015 · Cited by 85 · cited 2×
“This control should be based on the concept of authentication, authorization, and accounting This control should be based on the concept of authentication, authorization, and accounting (AAA) [30].”
Balda, J. C., Mantooth, A., Blum, R. S., & Tenti, P. (2017) · IEEE Power Electronics Magazine · doi:10.1109/mpel.2017.2761422 · Cited by 82
ARIES: A Novel Multivariate Intrusion Detection System for Smart Grid
Grammatikis, P. I. R., Sarigiannidis, P. G., Efstathopoulos, G., & Panaousis, E. (2020) · Sensors · doi:10.3390/s20185305 · Cited by 76 · cited 1×
“The intrusion detection system (IDS) for smart grid is presented in [24,25].”
Hayes, G., & El-Khatib, K. (2013) · 2013 Third International Conference on Communications and Information Technology (ICCIT) · doi:10.1109/iccitechnology.2013.6579545 · Cited by 65 · cited 2×
“Another proposal that is based on SCTP (stream control transmission protocol) and HMAC (hash-based message authentication code), which is called ModbusSec, is presented in [16].”
A Role-Based Access Control Model in Modbus SCADA Systems. A Centralized Model Approach
Figueroa-Lorenzo, S., Añorga, J., & Arrizabalaga, S. (2019) · Sensors · doi:10.3390/s19204455 · Cited by 58 · cited 2×
“However, because it is widespread in the industry, the option to provide security to the protocol is a solution that many organizations are likely to adopt [13].”
Robust hardware true random number generators using DRAM remanence effects
Tehranipoor, F., Yan, W., & Chandy, J. A. (2016) · 2016 IEEE International Symposium on Hardware Oriented Security and Trust (HOST) · doi:10.1109/hst.2016.7495561 · Cited by 54 · cited 1×
“…token code must be unique in order to guarantee the integrity of the username, for This token code must be unique in order to guarantee the integrity of the username, for example, a SHA256 of a robust random number generation [33,34]. example, a SHA256 of a robust random number generation [33,34].”
Research works printed but not linked: 1
- Lorenz, 2015, Industry 4.0: The future of productivity and growth in manufacturing industries, Boston Consult. Group, 9, 54
Cited by
Folgado, F., Calderón, D., González, I., & Calderón, A. (2024) · Electronics · doi:10.3390/electronics13040782 · Cited by 174
“In these systems, open architectures are implemented and standardized communication protocols are used, implying better communication capabilities.”
BackgroundNankya, M., Chataut, R., & Akl, R. (2023) · Sensors · doi:10.3390/s23218840 · Cited by 114
“…of the Modbus protocol, as seen below: (a) A group of researchers proposed the Modbus/TCP Security protocol, which incorporates authentication and authorization mechanisms to ensure protection against deliberate unauthorized access as an enhancement for improved security in the ICS framework [74].”
MethodTapia, E., Pinilla, L. S., López-Novoa, U., Bediaga, I., & de Lacalle, L. N. L. (2023) · Sensors · doi:10.3390/s23125694 · Cited by 56
“For instance, Martins and Vidal [22] proposed authentication and authorization functions by implementing username and password based access control methods for human users with knowledge of industrial automation control systems (IACSs).”
BackgroundZagan, I., & Găitan, V. G. (2022) · Mathematics · doi:10.3390/math10244686 · Cited by 21
Strengthening ICS defense: Modbus-NFA behavior model for enhanced anomaly detection
Amer, E., Al‐rimy, B. A. S., & El–Sappagh, S. (2025) · Journal of Information Security and Applications · doi:10.1016/j.jisa.2025.103990 · Cited by 23
Metadata
- Authors
- Martins, T., & Oliveira, S. V. G.
- Affiliations
- Universidade do Estado de Santa Catarina (BR)
- Departamento de Engenharia Elétrica, Universidade do Estado de Santa Catarina, Joinville 89219-710, Brazil
- Venue
- Sensors
- Publisher
- MDPI AG
- Published
- 2022-10-20
- Volume
- 22
- Issue
- 20
- Pages
- 8024
- ISSN
- 1424-8220 (ISSN-L)
- PMC
- PMC9607043
- OpenAlex
- W4306965903
- Cited by
- 45
- References
- 19
- Citations by year
- 2026: 15 · 2025: 12 · 2024: 11 · 2023: 5 · 2022: 2
- FWCI
- 3.02
- Type
- journal article
- Language
- en
- Open access
- gold
- doi.org
- Licence
- Locations
- Sensors (publishedVersion, cc-by)
- PubMed Central (publishedVersion, cc-by)
- PubMed (publishedVersion)
- LA Referencia (Red Federada de Repositorios Institucionales de Publicaciones Científicas) (publishedVersion, other-oa)
- DOAJ (DOAJ: Directory of Open Access Journals) (submittedVersion, cc-by-sa)
- Funders
- Coordenação de Aperfeiçoamento de Pessoal de Nível Superior–CAPES–Brazil (1484/2020)
- Topics
- Physical Sciences › Engineering › Control and Systems Engineering › Industrial Automation and Control Systems
- Physical Sciences › Engineering › Control and Systems Engineering › Smart Grid Security and Resilience
- Physical Sciences › Computer Science › Computer Networks and Communications › Access Control and Trust
- Keywords
- Modbus TCP, security protocols, authentication, authorization, access control, zero-trust architecture, operational technology security, man-in-the-middle attacks, Node-RED, unauthorized access prevention
- MeSH terms
- Confidentiality, Humans, Software, Computer Security, Telemedicine
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
The claim verdicts this report counts are experimental: their accuracy is not yet measured.
A language model drew the claims from the paper on 2026-10-10, under version 3 of the claim definition (model deepseek-v4.1-flash, prompt extract-v3).
A second model labelled each claim on 2026-10-10 (model jev-1.13-20260917, definition revision gold-guideline-v0.2).
Cited sources are checked with a language model’s help (gpt-6-sol).
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
How to cite
Cite CoChat for the checks on this page, and the paper for its own findings.
- This page
- CoChat. (2026). Citation check: Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported. https://app.cochat.ai/papers/10.3390/s22208024
- The paper
- Martins, T., & Oliveira, S. V. G. (2022). Enhanced Modbus/TCP Security Protocol: Authentication and Authorization Functions Supported. Sensors. https://doi.org/10.3390/s22208024
Data sources
Bibliographic data: Semantic Scholar, OpenAlex, Crossref.
Contains information from the Semantic Scholar Academic Graph Datasets, made available under the ODC Attribution License (ODC-BY 1.0).
Semantic Scholar’s data is described in: Kinney, R., et al. (2023). The Semantic Scholar Open Data Platform. arXiv:2301.10140.
