

The DOI matches its Crossref record; 50 of the 50 references it cites were found in a registry or an index; none of the 42 sources its claims cite is checked for support yet.
A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks
Open accessAbstract
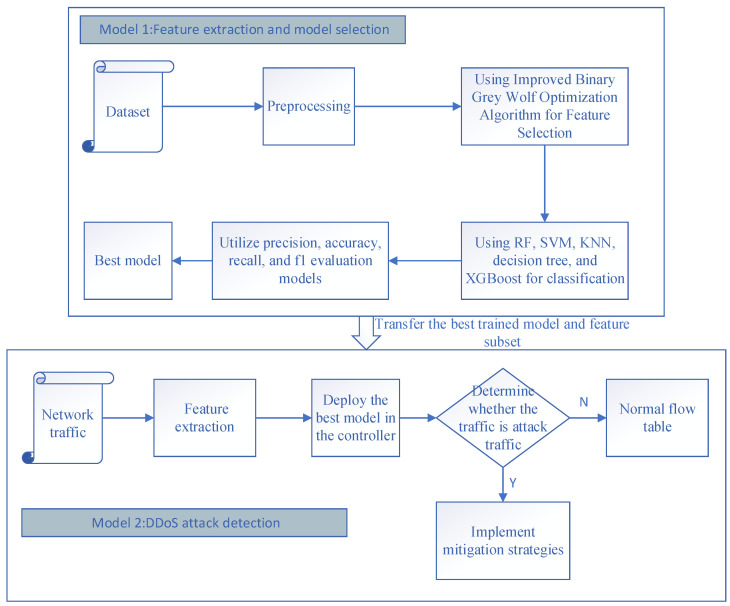
Distributed denial-of-service (DDoS) attacks pose a significant cybersecurity threat to software-defined networks (SDNs). This paper proposes a feature-engineering- and machine-learning-based approach to detect DDoS attacks in SDNs. First, the CSE-CIC-IDS2018 dataset was cleaned and normalized, and the optimal feature subset was found using an improved binary grey wolf optimization algorithm. Next, the optimal feature subset was trained and tested in Random Forest (RF), Support Vector Machine (SVM), K-Nearest Neighbor (k-NN), Decision Tree, and XGBoost machine learning algorithms, from which the best classifier was selected for DDoS attack detection and deployed in the SDN controller. The results show that RF performs best when compared across several performance metrics (e.g., accuracy, precision, recall, F1 and AUC values). We also explore the comparison between different models and algorithms. The results show that our proposed method performed the best and can effectively detect and identify DDoS attacks in SDNs, providing a new idea and solution for the security of SDNs.
Overview
CoChat Summary
TL;DR
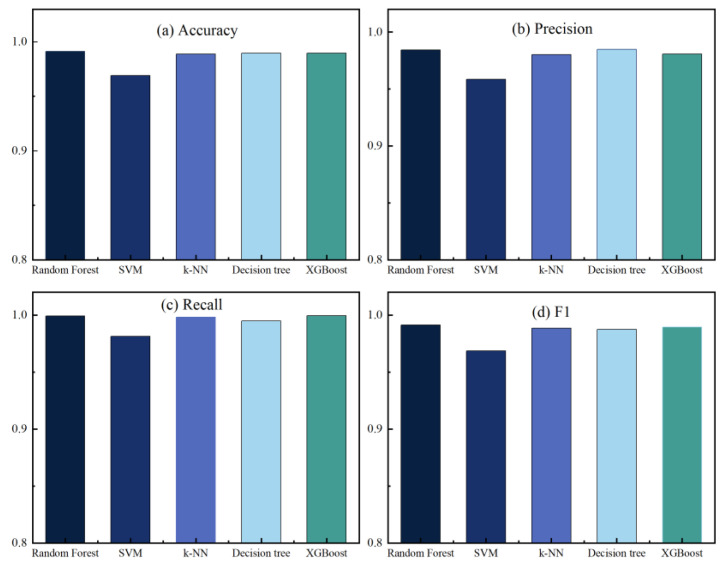
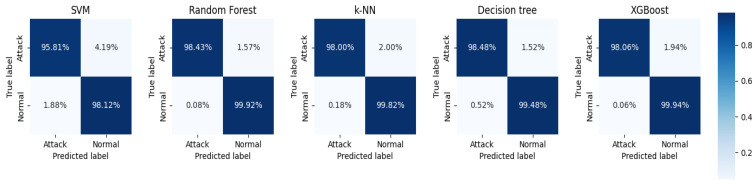
This paper proposes an SDN DDoS detection method that combines improved binary grey wolf optimization feature selection with machine learning, selecting 26 of 79 CSE-CIC-IDS2018 features and deploying the best classifier in the SDN controller. Random Forest performed best overall, achieving accuracy 0.9913, precision 0.9843, recall 0.9992, and F1 0.9913 after feature extraction.
Key findings
- Feature selection reduced the dataset from 79 to 26 features; after feature extraction, all classifiers improved in all metrics, with Decision Tree improving most by 0.0341, followed by RF by 0.0278, and SVM least by 0.0202.
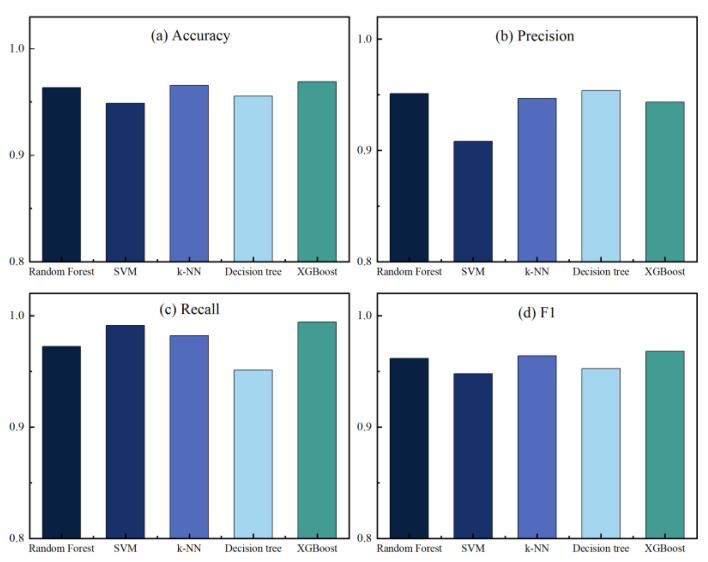
- On the original dataset, XGBoost had the best accuracy at 0.969. After feature extraction, the conclusion reports RF as best under accuracy, precision, recall, and F1 with 0.9913, 0.9843, 0.9992, and 0.9913, respectively; earlier text notes RF accuracy was slightly lower than Decision Tree but all other metrics were better.
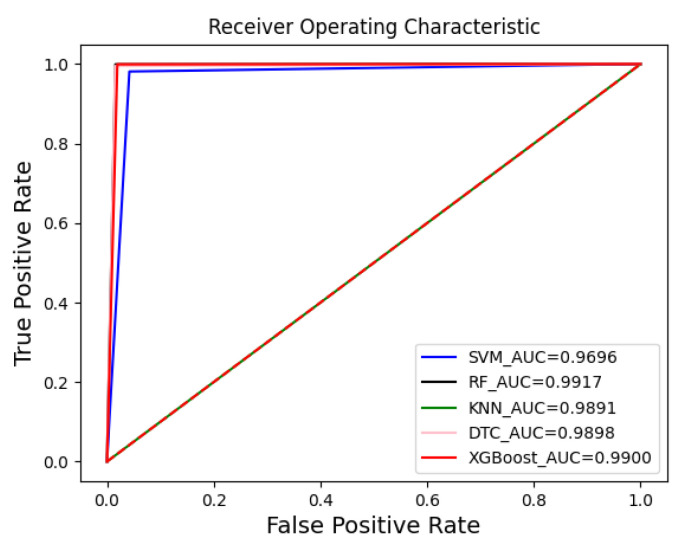
- AUC-ROC values were SVM 0.9696, RF 0.9917, k-NN 0.9891, DTC 0.9898, and XGBoost 0.99, leading the authors to consider RF the best performer.
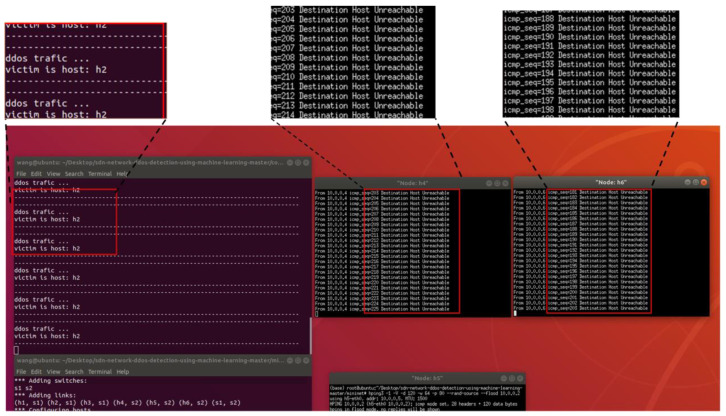
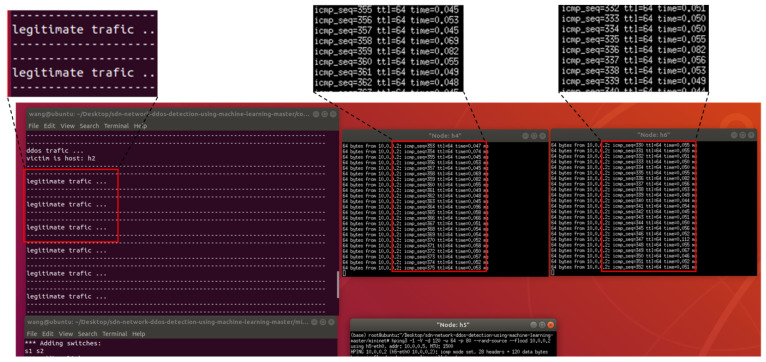
- In the SDN test, an hping3 flooding attack from h5 to h2 disrupted h4 and h6; after mitigation (dropping packets corresponding to a specific input port), h4 and h6 could send data to h2 normally.
Methods
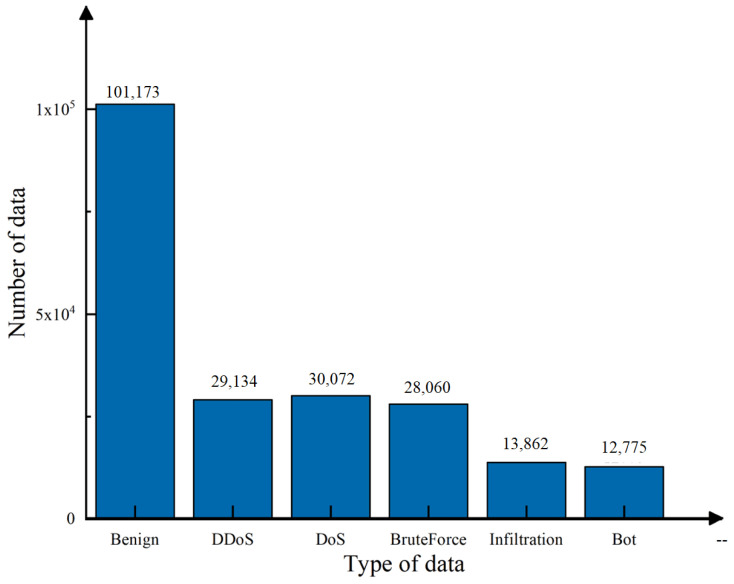
- Data: CSE-CIC-IDS2018 was cleaned by dropping NaN, empty, or infinite values, reducing samples from 215,761 to 215,076 (685 removed); MinMax scaling mapped features to [0,1]; an average of 210,000 samples was selected, including DDoS, DoS, Brute Force, Infiltration, and Bot attack types.
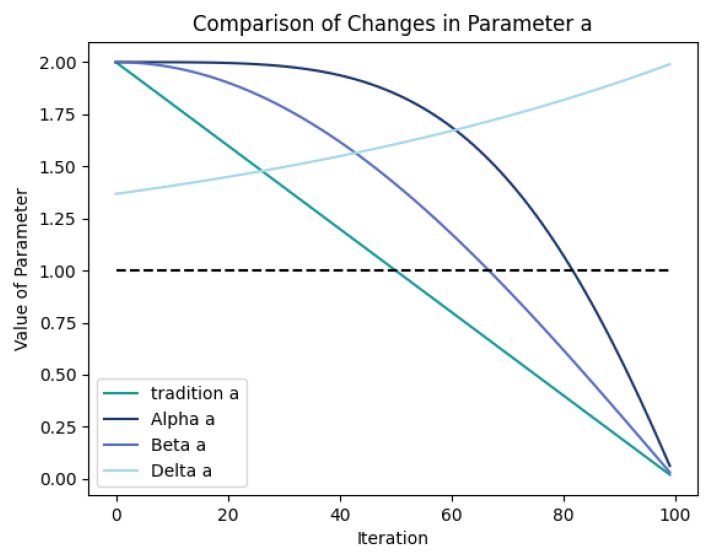
- Feature selection: an improved binary grey wolf optimization algorithm used Tent chaotic mapping initialization, nonlinear cosine search parameters, and weighted position updating; it selected 26 features from 79, with fitness based on feature count and k-NN classification error rate.
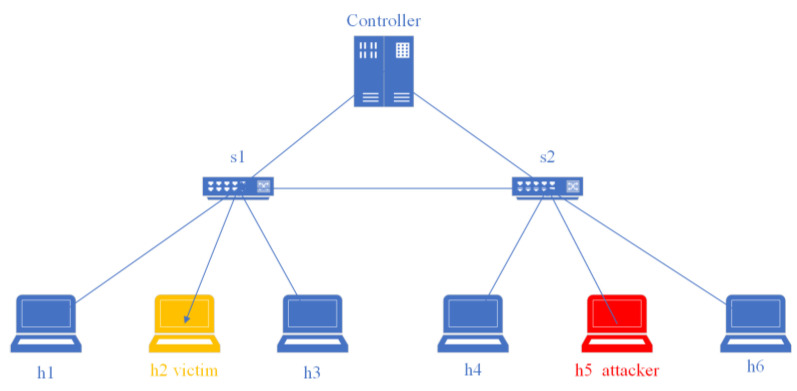
- Classifiers and evaluation: SVM, RF, Decision Tree, XGBoost, and k-NN were trained and tested with default parameters and 10-fold cross-validation using accuracy, precision, recall, F1, and ROC/AUC; the best classifier was deployed in a Ryu controller, with experiments on Ubuntu 18.04, 16 GB RAM, AMD Ryzen 7 5800 H at 3.20 GHz, Mininet, and a topology of one controller, two switches, and six hosts.
Limitations
- Stated: comparison with similar works is difficult because they use different datasets and models; the cited works did not show DDoS attack detection performance on SDNs and did not develop mitigation strategies.
- Stated future work implies current limitations: the authors plan to use advanced feature engineering and deep learning, research mitigation of adversarial attacks for robustness and adaptability, and integrate the method with other network security technologies.
- Evident from the text: evaluation uses one dataset (CSE-CIC-IDS2018) and a small Mininet topology (one controller, two switches, six hosts); classifiers used default parameters, and adversarial robustness is not tested in the current work.
Model-written summary. Check it against the paper before relying on it.
Integrity signals
Registry
Cites
Statistics
Figures
Verification
Claims the paper makes
0 Valid · 1 Not valid · 20 Not checked · 33 Own results and interpretations
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
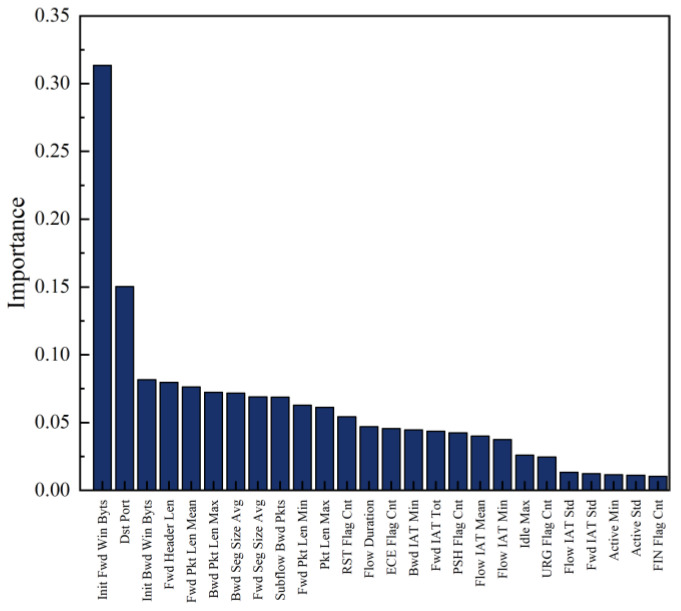
“the algorithm’s selection process also identified the importance of each selected feature, which is illustrated in Figure 6.”
§ A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks > 4. Methodology > 4.1. Data Preprocessing and Feature Extraction
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: unclear — It is unclear whether the paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“From the data analysis, we can see that the XGBoost algorithm had the best performance on the original dataset with an accuracy of 0.969.”
- Also stated in: § 6. Conclusions and Future Work · plain
“The results showed that the highest accuracy of XGBoost was 0.969 on the original dataset”
§ A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks > 5. Experiments and Analysis of Results > 5.3. Analysis of Results
plain- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: unclear — It is unclear whether the paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
- Rests on 2 assumptions not shown here.
- Also stated in: § 6. Conclusions and Future Work · plain
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“The results show that RF performs best when compared across several performance metrics (e.g., accuracy, precision, recall, F1 and AUC values).”
§ A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks > Abstract
plain- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper reports from its own data — it cites no other source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“In total, 26 features were selected from the original dataset of 79 features using the algorithm mentioned above.”
§ A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks > 4. Methodology > 4.1. Data Preprocessing and Feature Extraction
plainstates a cause- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
A result the paper states — it cites no source for it, so there is none to check. The quote shows it is in the paper.
In the paper
“Due to this dataset’s significant data volume imbalance, we selected an average of 210,000 sample data, including DDoS, DoS, Brute Force, Infiltration, and Bot attack types”
§ A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks > 4. Methodology > 4.1. Data Preprocessing and Feature Extraction
plainn = 210,000- Asserted: passes — The authors put it forward as true.
- Checkable: passes — It can be checked against evidence.
- Load-bearing: passes — The paper’s conclusions depend on it.
- Based: passes — The paper gives a reason why it holds.
12 more claims
Create a free account to see all 54 claims and to verify the 42 references still open.
- Probably not a substantial claim. 22
- It may state two separate claims as one. 25
- The quote only partly states this claim. 2
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
Each contradiction between two passages listed here was confirmed by an independent check.
Rated major: it would touch a result — a value a result rests on, reported and recomputed p-values on opposite sides of the significance level, two passages that conflict with no sign which is right, or a cited work retracted before this paper was published.
In the paper
§ A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks > 5. Experiments and Analysis of Results > 5.3. Analysis of Results
“the accuracy, which was slightly lower than that of the Decision Tree algorithm”
§ A DDoS Detection Method Based on Feature Engineering and Machine Learning in Software-Defined Networks > 6. Conclusions and Future Work
“the RF classifier performed best under accuracy, precision, recall, and f1_score metrics with 0.9913, 0.9843, 0.9992, and 0.9913, respectively.”
Citations
Cites
Mirjalili, S., Mirjalili, S. M., & Lewis, A. (2014) · Advances in Engineering Software · doi:10.1016/j.advengsoft.2013.12.007 · Cited by 19,343
Machine learning and deep learning
Janiesch, C., Zschech, P., & Heinrich, K. (2021) · Electronic Markets · doi:10.1007/s12525-021-00475-2 · Cited by 2,959
Binary grey wolf optimization approaches for feature selection
Emary, E., Zawbaa, H. M., & Hassanien, A. E. (2016) · Neurocomputing · doi:10.1016/j.neucom.2015.06.083 · Cited by 1,410
Binary Optimization Using Hybrid Grey Wolf Optimization for Feature Selection
Al-Tashi, Q., Abdul Kadir, S. J., Rais, H. M., Mirjalili, S., & Alhussian, H. (2019) · IEEE Access · doi:10.1109/access.2019.2906757 · Cited by 487
Mestres, A., Rodriguez-Natal, A., Carner, J., Barlet-Ros, P., Alarcón, E., Solé, M., Muntés-Mulero, V., Meyer, D., Barkai, S., Hibbett, M. J., et al. (2017) · ACM SIGCOMM Computer Communication Review · doi:10.1145/3138808.3138810 · Cited by 352
Increasing the Performance of Machine Learning-Based IDSs on an Imbalanced and Up-to-Date Dataset
Karatas, G., Demir, O., & Sahingoz, O. K. (2020) · IEEE Access · doi:10.1109/access.2020.2973219 · Cited by 293
Alzahrani, A. O., & Alenazi, M. J. F. (2021) · Future Internet · doi:10.3390/fi13050111 · Cited by 272
Polat, H., Polat, O., & Cetin, A. (2020) · Sustainability · doi:10.3390/su12031035 · Cited by 265
Automated DDOS attack detection in software defined networking
Ahuja, N., Singal, G., Mukhopadhyay, D., & Kumar, N. (2021) · Journal of Network and Computer Applications · doi:10.1016/j.jnca.2021.103108 · Cited by 234
Almomani, O. (2020) · Symmetry · doi:10.3390/sym12061046 · Cited by 231
Cited by
Advancing cybersecurity: a comprehensive review of AI-driven detection techniques
Salem, A. H., Azzam, S. M., Emam, O. E., & Abohany, A. A. (2024) · Journal of Big Data · doi:10.1186/s40537-024-00957-y · Cited by 282
Cyber-Secure SDN: A CNN-Based Approach for Efficient Detection and Mitigation of DDoS attacks
Najar, A. A., & Naik, S. M. (2024) · Computers & Security · doi:10.1016/j.cose.2024.103716 · Cited by 141
Musa, N. S., Mirza, N. M., Rafique, S. H., Abdallah, A. M., & Thangavel, M. (2024) · IEEE Access · doi:10.1109/access.2024.3360868 · Cited by 108
Cyber Attack Prediction: From Traditional Machine Learning to Generative Artificial Intelligence
Ankalaki, S., Atmakuri, A. R., Pallavi, M., Hukkeri, G. S., Jan, T., & Naik, G. R. (2025) · IEEE Access · doi:10.1109/access.2025.3547433 · Cited by 94
A DDoS attack detection method based on IQR and DFFCNN in SDN
Yue, M., Yan, H., Han, R., & Wu, Z. (2025) · Journal of Network and Computer Applications · doi:10.1016/j.jnca.2025.104203 · Cited by 55
Becerra-Suarez, F. L., Fernández-Roman, I., & Forero, M. G. (2024) · Mathematics · doi:10.3390/math12091294 · Cited by 49
Han, D., Li, H., Fu, X., & Zhou, S. (2024) · Sensors · doi:10.3390/s24134344 · Cited by 49
Feature-Selection-Based DDoS Attack Detection Using AI Algorithms
Raza, M. S., Sheikh, M. N. A., Hwang, I., & Ab–Rahman, M. S. (2024) · Telecom · doi:10.3390/telecom5020017 · Cited by 43
Toony, A. A., Alqahtani, F. H., Alginahi, Y. M., & Said, W. (2024) · Internet of Things · doi:10.1016/j.iot.2024.101231 · Cited by 39
Karmous, N., Aoueileyine, M. O.-E., Abdelkader, M., Romdhani, L., & Youssef, N. (2024) · Sensors · doi:10.3390/s24155022 · Cited by 39
Dhahir, Z. S. (2024) · Journal of Future Artificial Intelligence and Technologies · doi:10.62411/faith.2024-33 · Cited by 31
El-Sayed, A., Said, W., Tolba, A. K. R., Alginahi, Y. M., & Toony, A. A. (2024) · Computers & Electrical Engineering · doi:10.1016/j.compeleceng.2024.109484 · Cited by 30
Unseen Attack Detection in Software-Defined Networking Using a BERT-Based Large Language Model
Swileh, M. N., & Zhang, S. (2025) · AI · doi:10.3390/ai6070154 · Cited by 27
Kumar, C. B. S., Betam, S., Pustokhin, D. A., Lydia, E. L., Bala, K., Aluvalu, R., & Panigrahi, B. S. (2025) · Scientific Reports · doi:10.1038/s41598-025-96153-w · Cited by 27
Hybrid Chaotic Zebra Optimization Algorithm and Long Short-Term Memory for Cyber Threats Detection
Amin, R., Eltaweel, G., Ali, A. F., & Tahoun, M. (2024) · IEEE Access · doi:10.1109/access.2024.3397303 · Cited by 22
Comprehensive Review of Cybersecurity Challenges in the Age of IoT
Ismail, N. A.-K. N. (2026) · Innovative Reviews in Engineering and Science · doi:10.31838/ines/03.01.06 · Cited by 21
DDoS Attacks Detection in SDN Through Network Traffic Feature Selection and Machine Learning Models
Cuesta, E. P. E., Quintero, J. C. M., & Palma, J. D. A. (2025) · Telecom · doi:10.3390/telecom6030069 · Cited by 19
A.Abualhassan, A., Rashid, I., Binbeshr, F., & Imam, M. (2025) · IEEE Access · doi:10.1109/access.2025.3583855 · Cited by 18
Babbar, H., Rani, S., & Driss, M. (2024) · PLoS ONE · doi:10.1371/journal.pone.0314695 · Cited by 14
Pradeesh, S., Jeyakarthic, M., & Thirumalairaj, A. (2025) · Remote Sensing in Earth Systems Sciences · doi:10.1007/s41976-025-00204-9 · Cited by 14
Zhou, W. G., An, L., Han, R., & Li, G. (2025) · Information Processing & Management · doi:10.1016/j.ipm.2025.104179 · Cited by 14
IOTASDN: IOTA 2.0 Smart Contracts for Securing Software-Defined Networking Ecosystem
Fartitchou, M., Lamaakal, I., Maleh, Y., Makkaoui, K. E., Allali, Z. E., Pławiak, P., Alblehai, F., & El‐Latif, A. A. A. (2024) · Sensors · doi:10.3390/s24175716 · Cited by 12
Evaluating Machine Learning and Deep Learning Models for Enhanced DDoS Attack Detection
Owaid, M. A., & Hammoodi, A. S. (2024) · Mathematical Modelling and Engineering Problems · doi:10.18280/mmep.110221 · Cited by 11
Pebrianto, J., & Suryani, V. (2025) · IEEE Access · doi:10.1109/access.2025.3553144 · Cited by 10
A Swarm-Based Multi-Objective Framework for Lightweight and Real-Time IoT Intrusion Detection
Alsalamah, H. A., & Ismail, W. N. (2025) · Mathematics · doi:10.3390/math13152522 · Cited by 10
Enhanced DDoS Detection in Software Defined Networking Using Ensemble-Based Machine Learning
Bithi, M., Hossain, M. A., Ahmed, M. K., Sultana, R., Ahammad, I., & Islam, M. S. (2024) · International Conference on Electrical Engineering and Information Communication Technology · doi:10.1109/iceeict62016.2024.10534483 · Cited by 10
Wainwright, R., Bagheri, M., Salama, A., & Saatchi, R. (2025) · Applied Sciences · doi:10.3390/app152312389 · Cited by 9
Enhancing Network Security in IoT Applications through DDoS Attack Detection Using ML
Salama, A. M., Mohamed, M. A., & AbdElhalim, E. (2024) · MEJ Mansoura Engineering Journal · doi:10.58491/2735-4202.3181 · Cited by 8
RyuGuard —Combining Ryu and machine learning for proactive DDoS defense in software‐defined networks
Vadivu, D. S., & Rajagopalan, N. (2024) · Concurrency and Computation Practice and Experience · doi:10.1002/cpe.8289 · Cited by 8
Hybrid CNN-LSTM Model for DDoS Detection and Mitigation in Software-Defined Networks
Hirsi, A., Alhartomi, M. A., Audah, L., Hamdi, M. M., Salh, A., Ansa, G. O., Ahmed, S., & Farah, A. (2026) · IEEE Transactions on Network and Service Management · doi:10.1109/tnsm.2026.3662819 · Cited by 7
Manoharan, R., Joseph, C., Baskar, R., & Thavasimuthu, R. (2025) · Global NEST Journal · doi:10.30955/gnj.06966 · Cited by 7
Real-Time DDoS Detection in Software-Defined Networks Using Machine Learning
Hasan, K., Hossain, K. S., Alam, M. S., Islam, M., Apurbo, G. M. M., Ahmed, M. F., Noor, J., & Hossain, M. I. (2024) · International Conference on Computer and Information Technology (ICCIT) · doi:10.1109/iccit64611.2024.11022460 · Cited by 7
Kasprzyk, Z., & Rychlicki, M. (2025) · Sustainability · doi:10.3390/su17208985 · Cited by 6
Using machine learning to classify DOS/DDOS attacks
Kavetskyi, M. S., Сєвєрінов, О., Gvozdov, R. Y., & Smirnov, A. (2024) · Radiotekhnika · doi:10.30837/rt.2024.2.217.04 · Cited by 6
Detecting DDoS Attacks using Machine Learning: Survey
Arrak, S. Z., & Al-Janabi, R. J. S. (2024) · Journal of Al-Qadisiyah for Computer Science and Mathematics · doi:10.29304/jqcsm.2024.16.21548 · Cited by 5
Mandhari, E. A. A. A., Abdulnabi, M. S. H., Lontok, R. J., & Ali, A. (2026) · Discover Computing · doi:10.1007/s10791-026-10050-y · Cited by 5
Rajper, A., Paraman, N. B., Marsono, M. N., & Rajper, N. J. (2024) · International Conference on Smart Applications, Communications and Networking (SmartNets) · doi:10.1109/smartnets61466.2024.10577729 · Cited by 5
Detection and Mitigation of DDoS Attack in SDN Using Feature Based SVM and Decision Tree Approach
Ashwin, A., Santhosh, V. C. S., Venkatesh, R. T., Gowthami, N., & Tamilselvi, S. (2024) · International Conference on IoT Based Control Networks and Intelligent Systems (ICICNIS) · doi:10.1109/icicnis64247.2024.10823201 · Cited by 5
Yadav, A., Kaur, M., Sharma, C., & Prashar, D. (2025) · Elsevier eBooks · doi:10.1016/b978-0-443-29927-8.00005-9 · Cited by 5
Detection of DoS and DDoS Attacks Using Machine Learning and Blockchain in IoMT Networks
Agrawal, A. K., Baniya, P., Alazzawi, E. M., Rakesh, N., Bhushan, B., & Jamıl, A. (2024) · International Conference on Artificial Intelligence, Blockchain, and Internet of Things (AIBThings) · doi:10.1109/aibthings63359.2024.10863359 · Cited by 5
Chitte, P. H., & Chaudhari, S. S. (2025) · Decision Analytics Journal · doi:10.1016/j.dajour.2025.100608 · Cited by 4
Rajper, A., Paraman, N. B., Marsono, M. N., Rajper, N. J., Hameed, H., & Usman, M. (2026) · Scientific Reports · doi:10.1038/s41598-025-33463-z · Cited by 4
SDN-IDS: A Deep Learning Model for Detecting DDoS Attacks
Shariff, M. A., & Nelson Kennedy Babu, C. (2024) · International Journal of Electronics and Communication Engineering · doi:10.14445/23488549/ijece-v11i6p111 · Cited by 4
AI Based Intrusion Detection for DDoS and SQL Injection Attacks
Lamba, H. K., Gala, H., Mathew, R. R., & Shinde, S. (2024) · IEEE International Conference for Women in Computing (InCoWoCo) · doi:10.1109/incowoco64194.2024.10863756 · Cited by 4
IoT-based WISNE-SDN detection and DDOS attack mitigation using machine learning techniques
Raghavendran, N., & Robinson, Y. H. (2026) · PeerJ Computer Science · doi:10.7717/peerj-cs.3572 · Cited by 3
Evaluating Machine Learning Models for DDoS Detection in SDNs
Tonkal, Ö., & Mgungile, J. A. (2026) · Journal of Advances in Information Technology · doi:10.12720/jait.17.3.596-610 · Cited by 3
Machine Learning-Based Network Traffic Anomaly Detection Using the CIC-IDS2017 Dataset
Rozam, N. F., Sari, T. N., Yudianto, M. R. A., & Rahman, D. F. (2026) · UPGRADE Jurnal Pendidikan Teknologi Informasi · doi:10.30812/upgrade.v3i2.6174 · Cited by 3
Wicaksono, D. N., Setiadi, D. R. I. M., Susanto, A., Harkespan, I., Afendee, M., & Sambas, A. (2026) · Journal of Computing Theories and Applications · doi:10.62411/jcta.16126 · Cited by 3
Sathish, N., Valarmathi, K., Nagalakshmi, R., & Priya, K. H. (2024) · International Conference on Applied Artificial Intelligence and Computing (ICAAIC) · doi:10.1109/icaaic60222.2024.10575342 · Cited by 3
Zhang, H., Wu, S., Pan, J., Wang, Z., & Sun, X. (2024) · IEEE International Conference on Network Protocols (ICNP) · doi:10.1109/icnp61940.2024.10858549 · Cited by 3
Enhancing Credit Risk Classification Using LightGBM with Deep Feature Synthesis
Tambunan, S. R., Amalia, J., Sitorus, K. M., Sibuea, Y. A. R., & Hutabarat, L. R. (2024) · Journal of Information Systems and Informatics · doi:10.51519/journalisi.v6i4.902 · Cited by 3
Efficient Feature Engineering-Based Anomaly Detection for Network Security
Mayukha, S. (2024) · International Journal of Intelligent Systems and Applications in Engineering · Cited by 3
Haritha, V., Kumutha, R., Sindhuja, R., Srivastava, A., Shobana, G., & Sundararajan, S. C. M. (2023) · International Conference on Sustainable Communication Networks and Application (ICSCNA) · doi:10.1109/icscna58489.2023.10370432 · Cited by 3
RetractedBrief Review of Using Machine Learning for Traffic Engineering in Software-Defined Networks
Khalifa, E. H. (2025) · Pakistan Journal of Life and Social Sciences (PJLSS) · doi:10.57239/pjlss-2025-23.1.00135 · Cited by 2
Machine Learning-Based Detection and Mitigation of DDoS Attacks in Smart Grid Systems
(2025) · International Journal of Computer Applications Technology and Research · doi:10.7753/ijcatr1402.1021 · Cited by 2
Detection and Mitigation of DDOS Attack in SDN Using Feature Based RF & MLP Approach
Saranraj, K. R., Sumugar, M., Anantha Moorthy, R., Gowthami, N., & Tamilselvi, S. (2025) · International Conference on Intelligent Data Communication Technologies and Internet of Things (IDCIoT) · doi:10.1109/idciot64235.2025.10915162 · Cited by 2
Balaji, K., & Balachandra, M. (2025) · F1000Research · doi:10.12688/f1000research.163778.2 · Cited by 2
Machine Learning Models for DDoS Attack Detection: A Systematic Literature Review
Isiekwene, C. C., Azeez, N. A., Akinboro, S. A., & Sennaike, O. A. (2026) · Vokasi UNESA Bulletin of Engineering, Technology and Applied Science · doi:10.26740/vubeta.v3i2.40146 · Cited by 2
Mathematical Model on Distributed Denial of Service Attack in the Computer Network
Rao, Y. S., Rauta, A. K., Kund, S. N., Sethi, B., & Behera, J. (2023) · WSEAS TRANSACTIONS on COMMUNICATIONS archive · doi:10.37394/23204.2023.22.18 · Cited by 2
Novel prediction mechanism for Attack Prevention in Fiber-Optical Networks using AI-based SDN
Beemkumar Nagappan, N. S. (2024) · International Journal of Intelligent Systems and Applications in Engineering · Cited by 2
Padmakala, S., Al‐Jawahry, H. M., Palanivel, R., John, Y. M. M., & Madhavi, A. (2024) · International Conference on Distributed Systems, Computer Networks and Cybersecurity (ICDSCNC) · doi:10.1109/icdscnc62492.2024.10939939 · Cited by 2
Efficient DDoS Detection in Software-Defined Networking: A Machine Learning Perspective
Ranjan, A., & Singh, A. (2025) · International Conference on Disruptive Technologies (ICDT) · doi:10.1109/icdt63985.2025.10986478 · Cited by 1
Optimizing DDoS attack detection in SDN using machine learning
Yao, R. A., & Guinko, F. T. (2025) · Intelligent Cybersecurity Conference (ICSC) · doi:10.1109/icsc65596.2025.11139942 · Cited by 1
Hamad, S., & Ghafoor, K. Z. (2026) · ARO-The Scientific Journal of Koya University · doi:10.14500/aro.12210 · Cited by 1
Machine Learning for DDoS Attack Detection in SDN: a Systematic Literature Review
Muchtar, T., & Mutijarsa, K. (2025) · IEEE International Conference on Cryptography, Informatics, and Cybersecurity (ICoCICs) · doi:10.1109/icocics68032.2025.11384079 · Cited by 1
Autonomous Detection of DDoS Attacks in IoT Networks Using Machine Learning
Praveen Kumar, G., Kalaiarasan, T., Priyadharshini, K., V, Nagavel, V., Ramesh, P., & Bhuvaneswari, P. T., V (2025) · IEEE International Conference on Smart Innovations in Systems, Infrastructure, Mechanical, Power, AI and Computing Technologies (SISIMPACT) · doi:10.1109/sisimpact67725.2025.11439189 · Cited by 1
Sangeetha, M., Geraldine, J. M., Pamulaparthyvenkata, S., Mohan, M., & Kumar, H. (2026) · Lecture notes in electrical engineering · doi:10.1007/978-981-95-0788-7_15 · Cited by 1
Eksplorasi Teknik Pre-Processing Berbasis eXtreme Gradient Boosting (XGBoost) pada Serangan DDoS
Faiz, M. N., Sari, L., Riadi, I., Muhammad, A. W., & Aji, S. (2025) · JURIKOM (Jurnal Riset Komputer) · doi:10.30865/jurikom.v12i6.9380 · Cited by 1
Wiranata, A. D., Murniasih, I., & Ansari, R. (2026) · Journal of Nexural Intelligence · doi:10.71200/nexural.v1.i1.263 · Cited by 1
Enhancing Network Security Against DDoS Attacks: An Analysis of OPNET Modelers
Agrawal, A., Jain, V. K., & Astya, R. (2023) · International Conference on System Modeling & Advancement in Research Trends (SMART) · doi:10.1109/smart59791.2023.10428206 · Cited by 1
Ranjith, V., Yaashuwanth, C., Prathibanandhi, K., & Jayasankar, T. (2025) · Tehnicki vjesnik - Technical Gazette · doi:10.17559/tv-20240902001960 · Cited by 1
OPNET Insights: Unpacking DDoS Effects on Network Performance
Agrawal, A., Jain, V. K., & Astya, R. (2023) · International Conference on Advances in Computing, Communication Control and Networking (ICAC3N) · doi:10.1109/icac3n60023.2023.10541548
Abd, N. S., Karoui, K., & Abdulkareem, M. G. (2024) · Security and Safety · doi:10.1051/sands/2024025
Detection & Mitigation of DDoS Attacks Using Deep Learning Algorithms
Sanjeev, D., & Mokashi, B. (2025) · International Conference on AIML-Applications for Engineering & Technology (ICAET) · doi:10.1109/icaet63349.2025.10932173
Topsakal, M., Cevher, S., & Ergenç, D. (2025) · Journal of Systems Architecture · doi:10.1016/j.sysarc.2025.103408
DDoS Attack Detection Using Machine Learning
Antad, S. M., Uplenchwar, R., Gajbhiye, P., Wasnik, D., & Pawar, O. (2025) · Lecture notes in networks and systems · doi:10.1007/978-981-96-2697-7_42
Gopal, K. P., & Sambath, M. (2025) · Vietnam Journal of Science and Technology/Science and Technology · doi:10.15625/2525-2518/19667
DDoS Anomaly Detection in Software Defined Networks Using ML and DL
Tabasum, S. S. P. A. (2025) · IARJSET · doi:10.17148/iarjset.2025.12824
Peña, W., & Cubas, S. (2025) · LACCEI International Multiconference on Entrepreneurship, Innovation and Regional Development (LEIRD) · doi:10.18687/leird2025.1.1.419
Détection et classification des attaques DDoS dans les réseaux SDN par apprentissage machine
Mammeri, K. (2024) · Le dépôt institutionnel (Université du Québec à Trois-Rivières)
Elsi, Z. R. S., Stiawan, D., Suprapto, B. Y., Arifin, M. A. S., Idris, M. Y., & Budiarto, R. (2025) · IAES International Journal of Artificial Intelligence · doi:10.11591/ijai.v14.i4.pp3047-3062
Cost benefit analysis of underground and above ground structuresPreprint
Kalegore, S. J., & mohite, S. (2025) · SSRN Electronic Journal · doi:10.2139/ssrn.5605121
Разработка модели раннего обнаружения DDoS-атак на основе анализа сетевого трафика
Бакунина, К. Е. (2024) · Электронный архив ЮУрГУ (South Ural State University)
DDoS Attack Detection in Software Defined Networks
Kumar, S., & Gupta, S. (2025) · Lecture notes in networks and systems · doi:10.1007/978-981-96-8343-7_47
Blockchain and SVM Integration for Distributed DDoS Attack Detection
Hia, S. G. P., Hayati, N. Q., Hindarto, D., & Sani, A. (2026) · SinkrOn · doi:10.33395/sinkron.v10i1.15483
Aziz, T. A., & Ismayadi, I. (2026) · Bulletin of Intelligent Machines and Algorithms · doi:10.65780/bima.v1i2.10
DDoS Detection in SDN Using a Hybrid KNN and Naive Bayes Voting Model
AlMomin, H., Gargouri, A., & Ghorbel, M. (2025) · International Conference on Computational Intelligence and Communication Networks (CICN) · doi:10.1109/cicn67655.2025.11368300
Performance Analysis of Support Vector Machine Kernel Functions for UDP Flood DDoS Attack Detection
Dasari, K. B., Aeloori, S. T., Harismitha, E., Priyanka, R., & Laxmiprasanna, N. (2025) · International Conference on Intelligent Systems for Cybersecurity (ISCS) · doi:10.1109/iscs69371.2025.11386390
Alhamami, K. E., Ali, H., Abdulkadhim, F. G., Gafel, R., & Kdhm, A. A. (2026) · Engineering headway · doi:10.4028/p-mu7mpl
Kwiecien, A., & Saeed, W. (2026) · Mathematical and Computational Applications · doi:10.3390/mca31020062
Neuro-Fuzzy Approach for Detecting DDoS Attacks in IoT Environments Applied to Biosignal Monitoring
Fernandez, A. P., & Bayas, M. M. (2026) · Technologies · doi:10.3390/technologies14050253
A Lightweight Deep Learning Framework for Early-Stage DDoS Defense in Software Defined Networking
Zubayer, M. M. H., Tabassum, B., Masum, A. K. M., & Farid, D. M. (2025) · International Conference on Computer and Information Technology (ICCIT) · doi:10.1109/iccit68739.2025.11490538
Temitope, A. B., & Makinde, O. E. (2026) · International Journal of Research and Innovation in Applied Science · doi:10.51584/ijrias.2026.11050051
Bharathi, S. K., Mathivanan, M., Mohamedyaseen, A., & Alagarsundaram, P. (2026) · International Journal of Communication Systems · doi:10.1002/dac.70532
A Framework for Network Traffic–Based DDoS Attack Detection and Explanation
Viola, R., Nogueira, M., & Veloso, A. (2026) · doi:10.5753/sbrc.2026.19395
An accurate and lightweight network intrusion detection system for software-defined networking
Abdulsalam, H. A., & Güney, H. (2026) · Engineering Research Express · doi:10.1088/2631-8695/ae7fd6
AlMomin, H. (2026) · International journal of intelligent engineering and systems · doi:10.22266/ijies2026.0731.20
DDoS Detection Framework Using Machine Learning Optimized by Bayesian and PSO Techniques
Sathaporn, P., Krungseanmuang, W., Chaowalittawin, V., Benjangkaprasert, C., Archevapanich, T., & Purahong, B. (2026) · Journal of Current Science and Technology · doi:10.59796/jcst.v16n3.2026.204
Ensuring Cybersecurity through Artificial Intelligence and Machine Learning
Bhavani, J., Dayalan, P., Sambamoorthy, N., & Woods, A. (2026) · BENTHAM SCIENCE PUBLISHERS eBooks · doi:10.2174/9798898816780126010007
Metadata
- Authors
- Liu, Z., Wang, Y., Feng, F., Liu, Y., Li, Z., & Shan, Y.
- Affiliations
- Hebei University (CN)
- Corresponding author
- Liu, Yifan
- Venue
- Sensors
- Publisher
- MDPI AG
- Published
- 2023-07-05
- Volume
- 23
- Issue
- 13
- Pages
- 6176
- ISSN
- 1424-8220 (ISSN-L)
- PMC
- PMC10346601
- OpenAlex
- W4383346073
- Cited by
- 119
- References
- 50
- Citations by year
- 2026: 43 · 2025: 38 · 2024: 34 · 2023: 4
- FWCI
- 9.74
- Type
- journal article
- Language
- en
- Open access
- gold
- doi.org
- Licence
- Locations
- Sensors (publishedVersion, cc-by)
- PubMed Central (publishedVersion, cc-by)
- PubMed (publishedVersion)
- DOAJ (DOAJ: Directory of Open Access Journals) (submittedVersion, cc-by-sa)
- Funders
- National Natural Science Foundation of Hebei Province, China (F2019201427, 2017A20004)
- Fund for Integration of Cloud Computing and Big Data, Innovation of Science and Education (FII) of Ministry of Education of China (F2019201427, 2017A20004)
- Topics
- Physical Sciences › Computer Science › Computer Networks and Communications › Network Security and Intrusion Detection
- Physical Sciences › Computer Science › Computer Networks and Communications › Software-Defined Networks and 5G
- Physical Sciences › Computer Science › Hardware and Architecture › Network Packet Processing and Optimization
- Keywords
- DDoS attack detection, software-defined networking, feature selection, grey wolf optimizer, random forest, XGBoost, support vector machine, k-nearest neighbors, decision tree, SDN controller security, network intrusion detection
- MeSH terms
- Machine Learning, Algorithms, Software, Cluster Analysis, Benchmarking
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
A language model drew the claims from the paper on 2026-11-16, under version 3 of the claim definition (model deepseek-v4.1-flash, prompt extract-v3).
A second model labelled each claim on 2026-11-16 (model jev-1.13-20260917, definition revision gold-guideline-v0.2).
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
Data sources
Bibliographic data: Semantic Scholar, OpenAlex, Crossref.
Contains information from the Semantic Scholar Academic Graph Datasets, made available under the ODC Attribution License (ODC-BY 1.0).
Semantic Scholar’s data is described in: Kinney, R., et al. (2023). The Semantic Scholar Open Data Platform. arXiv:2301.10140.
