

Explainable Artificial Intelligence in CyberSecurity: A Survey
Open accessThe DOI matches its Crossref record; 242 of the 242 references it cites were found in a registry or an index.
Abstract
Nowadays, Artificial Intelligence (AI) is widely applied in every area of human being’s daily life. Despite the AI benefits, its application suffer from the opacity of complex internal mechanisms and doesn’t satisfy by design the principles of Explainable Artificial Intelligence (XAI). The lack of transparency further exacerbates the problem in the field of Cybersecurity because entrusting crucial decisions to a system that cannot explain itself presents obvious dangers. There are several methods in the literature capable of providing explainability of AI results. Anyway, the application of XAI in Cybersecurity can be a double-edged sword. It substantially improves the Cybersecurity practices but simultaneously leaves the system vulnerable to adversary attacks. Therefore, there is a need to analyze the state-of-the-art of XAI methods in Cybersecurity to provide a clear vision for future research. This study presents an in-depth examination of the application of XAI in Cybersecurity. It considers more than 300 papers to comprehensively analyze the main Cybersecurity application fields, like Intrusion Detection Systems,Malware detection, Phishing and Spam detection, BotNets detection, Fraud detection, Zero-Day vulnerabilities, Digital Forensics and Crypto-Jacking. Specifically, this study focuses on the explainability methods adopted or proposed in these fields, pointing out promising works and new challenges.
Overview
The claims and statistics of this paper haven’t been checked yet.
Free: it reads the open-access text and checks the first 5 claims that cite a source we can check. Create a free account to check every claim.
Integrity signals
Registry
Cites
Statistics
Figures

Verification
Claims the paper makes
The claims and statistics of this paper haven’t been checked yet.
Free: it reads the open-access text and checks the first 5 claims that cite a source we can check. Create a free account to check every claim.
Claims other papers make about this one
Each is checked against this paper’s own text: does it say what the citing paper says it does?
The check wasn’t confident either way, so it gives no verdict — never disputed.
In the citing paper
“In this way, AI-based testing methods not only enhance processing time but also improve the accuracy of randomness assessment processes by providing more comprehensive and reliable analyses”
From A novel deep learning-based statistical randomness evaluation test methodology for cryptographic applications (2025) · cites this paper as Capuano et al. 2022
Experimental — accuracy not yet measured
Self-check
Percentages, sums and reported differences re-computed from the paper’s own numbers.
The self-check needs the paper’s full text.
Citations
Cites
Grad-CAM: Visual Explanations from Deep Networks via Gradient-Based Localization
Selvaraju, R. R., Cogswell, M., Das, A., Vedantam, R., Parikh, D., & Batra, D. (2017) · 2017 IEEE International Conference on Computer Vision (ICCV) · doi:10.1109/iccv.2017.74 · Cited by 24,513
A Unified Approach to Interpreting Model Predictions
Lundberg, S., & Lee, S.-I. (2017) · arXiv · doi:10.48550/arxiv.1705.07874 · Cited by 23,707
Arrieta, A. B., Díaz-Rodríguez, N., Del Ser, J., Bennetot, A., Tabik, S., Barbado, A., García, S., Gil-López, S., Molina, D., Benjamins, R., et al. (2019) · arXiv · doi:10.48550/arxiv.1910.10045 · Cited by 11,321
Barredo Arrieta, A., Díaz-Rodríguez, N., Del Ser, J., Bennetot, A., Tabik, S., Barbado, A., Garcia, S., Gil-Lopez, S., Molina, D., Benjamins, R., et al. (2020) · Information Fusion · doi:10.1016/j.inffus.2019.12.012 · Cited by 10,423
“Why Should I Trust You?”: Explaining the Predictions of Any Classifier
Ribeiro, M., Singh, S., & Guestrin, C. (2016) · Proceedings of the 2016 Conference of the North American Chapter of the Association for Computational Linguistics: Demonstrations · doi:10.18653/v1/n16-3020 · Cited by 6,682
Peeking Inside the Black-Box: A Survey on Explainable Artificial Intelligence (XAI)
Adadi, A., & Berrada, M. (2018) · IEEE Access · doi:10.1109/access.2018.2870052 · Cited by 6,294 · cited 1×
“312 Adadi and Berrada [16] conducted an exhaustive literature 313 analysis, collecting and analyzing 381 different scientific 314”
A detailed analysis of the KDD CUP 99 data set
Tavallaee, M., Bagheri, E., Lu, W., & Ghorbani, A. A. (2009) · 2009 IEEE Symposium on Computational Intelligence for Security and Defense Applications · doi:10.1109/cisda.2009.5356528 · Cited by 5,396
Toward Generating a New Intrusion Detection Dataset and Intrusion Traffic Characterization
Sharafaldin, I., Habibi Lashkari, A., & Ghorbani, A. A. (2018) · Proceedings of the 4th International Conference on Information Systems Security and Privacy · doi:10.5220/0006639801080116 · Cited by 5,318
Explanation in artificial intelligence: Insights from the social sciences
Miller, T. (2019) · Artificial Intelligence · doi:10.1016/j.artint.2018.07.007 · Cited by 5,302
Wohlin, C. (2014) · Proceedings of the 18th International Conference on Evaluation and Assessment in Software Engineering · doi:10.1145/2601248.2601268 · Cited by 4,234
Moustafa, N., & Slay, J. (2015) · 2015 Military Communications and Information Systems Conference (MilCIS) · doi:10.1109/milcis.2015.7348942 · Cited by 4,033
Explainable AI: a review of machine learning interpretability methods
Linardatos, P., Papastefanopoulos, V., & Kotsiantis, S. (2020) · Entropy · doi:10.3390/e23010018 · Cited by 2,922 · cited 1×
“High-performance AI systems, particularly those based on DL, behave similarly to black boxes that provide good results but can hardly justify a given output in a human-understandable way [12], [13].”
BackgroundA Survey on Explainable Artificial Intelligence (XAI): Toward Medical XAI
Tjoa, E., & Guan, C. (2021) · IEEE Transactions on Neural Networks and Learning Systems · doi:10.1109/tnnls.2020.3027314 · Cited by 2,524
Explaining Explanations: An Overview of Interpretability of Machine Learning
Gilpin, L. H., Bau, D., Yuan, B. Z., Bajwa, A., Specter, M., & Kagal, L. (2018) · 2018 IEEE 5th International Conference on Data Science and Advanced Analytics (DSAA) · doi:10.1109/dsaa.2018.00018 · Cited by 2,507 · cited 1×
“A methodological approach for evaluating the inter-350 pretability of ML models is proposed in [22], based on a taxonomy that separates three forms of Explain-352 ability: imitate the processing, explain the representation, and explain-producing networks.”
MethodDrebin: Effective and Explainable Detection of Android Malware in Your Pocket
Arp, D., Spreitzenbarth, M., Hübner, M., Gascon, H., & Rieck, K. (2014) · Proceedings 2014 Network and Distributed System Security Symposium · doi:10.14722/ndss.2014.23247 · Cited by 2,331 · cited 1×
“One of the main works in this area is Drebin [134]; how-920 ever, for consistency, it will not be analyzed in-depth as it is a pre-2018 work.”
BackgroundDefinitions, methods, and applications in interpretable machine learning
Murdoch, W. J., Singh, C., Kumbier, K., Abbasi-Asl, R., & Yu, B. (2019) · Proceedings of the National Academy of Sciences · doi:10.1073/pnas.1900654116 · Cited by 2,167
Anchors: High-Precision Model-Agnostic Explanations
Ribeiro, M. T., Singh, S., & Guestrin, C. (2018) · Proceedings of the AAAI Conference on Artificial Intelligence · doi:10.1609/aaai.v32i1.11491 · Cited by 2,162
Machine Learning Interpretability: A Survey on Methods and Metrics
Carvalho, D. V., Pereira, E. M., & Cardoso, J. S. (2019) · Electronics · doi:10.3390/electronics8080832 · Cited by 1,842 · cited 1×
“Carvalho et al. [33] add a criterion on the stage of model 402 development, in-model interpretability that concerns ML 403 models that have inherent interpretability in it (through con-404 straints or not).”
BackgroundA Deep Learning Approach to Network Intrusion Detection
Shone, N., Ngoc, T. N., Phai, V. D., & Shi, Q. (2018) · IEEE Transactions on Emerging Topics in Computational Intelligence · doi:10.1109/tetci.2017.2772792 · Cited by 1,819
Explainable AI: From black box to glass box
Rai, A. (2020) · Journal of the Academy of Marketing Science · doi:10.1007/s11747-019-00710-5 · Cited by 1,317 · cited 1×
“It is essential to min-309 imize potential biases (e.g., algorithmic, racial, ideological and gender biases) during the ethical AI solution development stage [14], [15]. extremely particular object components to improve the inter-338 pretability of traditional CNNs.”
BackgroundAhmad, Z., Shahid Khan, A., Wai Shiang, C., Abdullah, J., & Ahmad, F. (2021) · Transactions on Emerging Telecommunications Technologies · doi:10.1002/ett.4150 · Cited by 1,288 · cited 1×
“IDSs can be implemented with hardware appliances or with 555 special software; sometimes, they combine both systems [69].”
Machine Learning and Deep Learning Methods for Cybersecurity
Xin, Y., Kong, L., Liu, Z., Chen, Y., Li, Y., Zhu, H., Gao, M., Hou, H., & Wang, C. (2018) · IEEE Access · doi:10.1109/access.2018.2836950 · Cited by 1,228
The Enron Corpus: A New Dataset for Email Classification Research
Klimt, B., & Yang, Y. (2004) · Lecture Notes in Computer Science · doi:10.1007/978-3-540-30115-8_22 · Cited by 1,157
Deep learning for cyber security intrusion detection: Approaches, datasets, and comparative study
Ferrag, M. A., Maglaras, L., Moschoyiannis, S., & Janicke, H. (2020) · Journal of Information Security and Applications · doi:10.1016/j.jisa.2019.102419 · Cited by 1,130 · cited 1×
“The performance of seven DL models on the CSE-CIC-474 IDS2018 and Bot-IoT datasets is examined in [59].”
MethodVisual interpretability for deep learning: a survey
Zhang, Q.-S., & Zhu, S.-C. (2018) · Frontiers of Information Technology & Electronic Engineering · doi:10.1631/fitee.1700808 · Cited by 950
Machine learning based phishing detection from URLs
Sahingoz, O. K., Buber, E., Demir, O., & Diri, B. (2019) · Expert Systems with Applications · doi:10.1016/j.eswa.2018.09.029 · Cited by 857
Explainable artificial intelligence: an analytical review
Angelov, P. P., Soares, E. A., Jiang, R., Arnold, N. I., & Atkinson, P. M. (2021) · WIREs Data Mining and Knowledge Discovery · doi:10.1002/widm.1424 · Cited by 843 · cited 1×
“Also, Angelov et al. [20] cover the visualization technique; in particular, they proposed a broader taxonomy, considering whether the explanation is local or not, if the models are transparent or opaque, if the techniques are model-specific or model-agnostic, and whether explanations are created by…”
BackgroundInterpretable Convolutional Neural Networks
Zhang, Q., Wu, Y. N., & Zhu, S.-C. (2018) · 2018 IEEE/CVF Conference on Computer Vision and Pattern Recognition · doi:10.1109/cvpr.2018.00920 · Cited by 833
Mittelstadt, B., Russell, C., & Wachter, S. (2019) · Proceedings of the Conference on Fairness, Accountability, and Transparency · doi:10.1145/3287560.3287574 · Cited by 794 · cited 1×
“In philosophy and sociology, Mittelstadt et al. [26] pay attention to the differences between these models and explanations.”
BackgroundA Multidisciplinary Survey and Framework for Design and Evaluation of Explainable AI Systems
Mohseni, S., Zarei, N., & Ragan, E. D. (2021) · ACM Transactions on Interactive Intelligent Systems · doi:10.1145/3387166 · Cited by 785 · cited 1×
“In [28], the attention is focused on the fidelity of work closely related to the explanation accuracy.”
BackgroundA Multidisciplinary Survey and Framework for Design and Evaluation of Explainable AI Systems
Mohseni, S., Zarei, N., & Ragan, E. D. (2018) · arXiv · doi:10.48550/arxiv.1811.11839 · Cited by 783
Cybersecurity data science: an overview from machine learning perspective
Sarker, I. H., Kayes, A. S. M., Badsha, S., Alqahtani, H., Watters, P., & Ng, A. (2020) · Journal of Big Data · doi:10.1186/s40537-020-00318-5 · Cited by 766 · cited 1×
“435 Information Security, Network security, operational secu-436 rity, application security, Internet of Things (IoT) Security, 437 Cloud security, and infrastructure Security are all covered by 438 CyberSecurity [48].”
BackgroundAbdul, A., Vermeulen, J., Wang, D., Lim, B. Y., & Kankanhalli, M. (2018) · Proceedings of the 2018 CHI Conference on Human Factors in Computing Systems · doi:10.1145/3173574.3174156 · Cited by 743
EMBER: An Open Dataset for Training Static PE Malware Machine Learning ModelsPreprint
Anderson, H. S., & Roth, P. (2018) · arXiv (Cornell University) · doi:10.48550/arxiv.1804.04637 · Cited by 680
Langer, M., Oster, D., Speith, T., Hermanns, H., Kästner, L., Schmidt, E., Sesing, A., & Baum, K. (2021) · Artificial Intelligence · doi:10.1016/j.artint.2021.103473 · Cited by 652 · cited 1×
“The need to consider the perspectives of 405 diverse stakeholders is highlighted in [34].”
BackgroundExplainable machine learning in deployment
Bhatt, U., Xiang, A., Sharma, S., Weller, A., Taly, A., Jia, Y., Ghosh, J., Puri, R., Moura, J. M. F., & Eckersley, P. (2020) · Proceedings of the 2020 Conference on Fairness, Accountability, and Transparency · doi:10.1145/3351095.3375624 · Cited by 633 · cited 1×
“In [35] 408 a survey of XAI methods in deployment is made, and [36] 409 which considers the XAI for tabular data.”
BackgroundA Survey of Methods for Explaining Black Box Models
Guidotti, R., Monreale, A., Ruggieri, S., Turini, F., Giannotti, F., & Pedreschi, D. (2019) · ACM Computing Surveys · doi:10.1145/3236009 · Cited by 629 · cited 1×
“Methods for describing black-box models on a wide scale, such as data mining and ML, were reviewed in [23].”
BackgroundNotions of explainability and evaluation approaches for explainable artificial intelligence
Vilone, G., & Longo, L. (2021) · Information Fusion · doi:10.1016/j.inffus.2021.05.009 · Cited by 598 · cited 1×
“To end this review 410 of works in Explainable Artificial Intelligence it is worth 411 considering also [37] where are identified future research 412 directions with Explainability as the starting component of 413 any AI system.”
BackgroundA Survey of Deep Learning Methods for Cyber Security
Berman, D. S., Buczak, A. L., Chavis, J. S., & Corbett, C. L. (2019) · Information · doi:10.3390/info10040122 · Cited by 569 · cited 1×
“In the sphere of CyberSecurity, researchers apply DL techniques for a variety of applications such as detecting network intrusions, malware traffic detec-471 tion and classification, and so on, as analyzed extensively in [55], [56], [57], and [58].”
MethodLoyola-Gonzalez, O. (2019) · IEEE Access · doi:10.1109/access.2019.2949286 · Cited by 559 · cited 1×
“As presented in [30], an alternative perspective on hybrid XAI models entails augmenting black-box model expertise with that of transparent model.”
BackgroundIntrusion Detection in 802.11 Networks: Empirical Evaluation of Threats and a Public Dataset
Kolias, C., Kambourakis, G., Stavrou, A., & Gritzalis, S. (2016) · IEEE Communications Surveys & Tutorials · doi:10.1109/comst.2015.2402161 · Cited by 550
Deep Learning Approach Combining Sparse Autoencoder With SVM for Network Intrusion Detection
Al-Qatf, M., Lasheng, Y., Al-Habib, M., & Al-Sabahi, K. (2018) · IEEE Access · doi:10.1109/access.2018.2869577 · Cited by 550
AI-Driven Cybersecurity: An Overview, Security Intelligence Modeling and Research Directions
Sarker, I. H. (2021) · doi:10.20944/preprints202101.0457.v1 · Cited by 550
DARPA's explainable artificial intelligence (XAI) program
Gunning, D. (2019) · Proceedings of the 24th International Conference on Intelligent User Interfaces · doi:10.1145/3301275.3308446 · Cited by 546
AI-Driven Cybersecurity: An Overview, Security Intelligence Modeling and Research Directions
Sarker, I. H., Furhad, M. H., & Nowrozy, R. (2021) · SN Computer Science · doi:10.1007/s42979-021-00557-0 · Cited by 543 · cited 1×
“[47] proposed a broad definition of Cyber- 434 Security that takes into account all relevant definitions.”
BackgroundA Survey on Machine Learning Techniques for Cyber Security in the Last Decade
Shaukat, K., Luo, S., Varadharajan, V., Hameed, I. A., & Xu, M. (2020) · IEEE Access · doi:10.1109/access.2020.3041951 · Cited by 530 · cited 2×
“There are various advantages and disadvantages to the use 429 of AI in this field, as briefly analyzed in [44] and [45], and 430 work like that done in [46], where all the existing literature 431 on the last decade is analyzed, can be of help to those who are 432 entering into the specific sector.”
BackgroundNetwork Intrusion Detection Combined Hybrid Sampling With Deep Hierarchical Network
Jiang, K., Wang, W., Wang, A., & Wu, H. (2020) · IEEE Access · doi:10.1109/access.2020.2973730 · Cited by 446 · cited 2×
“of Neural Networks [83], [84] and Adversarial Methods [85], 660 [86], [87].”
BackgroundDeep Learning Based Attack Detection for Cyber-Physical System Cybersecurity: A Survey
Zhang, J., Pan, L., Han, Q.-L., Chen, C., Wen, S., & Xiang, Y. (2022) · IEEE/CAA Journal of Automatica Sinica · doi:10.1109/jas.2021.1004261 · Cited by 432 · cited 1×
“In the sphere of CyberSecurity, researchers apply DL techniques for a variety of applications such as detecting network intrusions, malware traffic detec-471 tion and classification, and so on, as analyzed extensively in [55], [56], [57], and [58].”
MethodA comprehensive survey of AI-enabled phishing attacks detection techniques
Basit, A., Zafar, M., Liu, X., Javed, A. R., Jalil, Z., & Kifayat, K. (2021) · Telecommunication Systems · doi:10.1007/s11235-020-00733-2 · Cited by 429 · cited 1×
“For the specific field of phishing interesting approach is defined in [61] and for ransomware attacks in [62].”
BackgroundDeep learning methods in network intrusion detection: A survey and an objective comparison
Gamage, S., & Samarabandu, J. (2020) · Journal of Network and Computer Applications · doi:10.1016/j.jnca.2020.102767 · Cited by 382 · cited 1×
“The whole execution of the study is made public in order to facilitate objective comparisons and transparency in [60].”
BackgroundCreech, G., & Hu, J. (2014) · IEEE Transactions on Computers · doi:10.1109/tc.2013.13 · Cited by 356
An Explainable Machine Learning Framework for Intrusion Detection Systems
Wang, M., Zheng, K., Yang, Y., & Wang, X. (2020) · IEEE Access · doi:10.1109/access.2020.2988359 · Cited by 355
Parameterized Explainer for Graph Neural Network
Luo, D., Cheng, W., Xu, D., Yu, W., Zong, B., Chen, H., & Zhang, X. (2020) · arXiv · doi:10.48550/arxiv.2011.04573 · Cited by 355 · cited 1×
“The explanation is 1365 attributable to subgraph decomposition theory [198], where 1366 it is feasible to determine whether the learned model is inter- 1367 pretable by identifying the subgraph with the most significant 1368 influence on prediction and judging whether the subgraph is 1369 faithful to general knowledge.”
BackgroundChiew, K. L., Tan, C. L., Wong, K., Yong, K. S. C., & Tiong, W. K. (2019) · Information Sciences · doi:10.1016/j.ins.2019.01.064 · Cited by 348 · cited 1×
“Hybrid Ensemble Feature Selection (HEFS) is an interesting approach proposed in [155] with a new feature selection framework.”
BackgroundBotnet detection based on traffic behavior analysis and flow intervals
Zhao, D., Traore, I., Sayed, B., Lu, W., Saad, S., Ghorbani, A., & Garant, D. (2013) · Computers & Security · doi:10.1016/j.cose.2013.04.007 · Cited by 343
Cyber security meets artificial intelligence: a survey
Li, J.-H. (2018) · Frontiers of Information Technology & Electronic Engineering · doi:10.1631/fitee.1800573 · Cited by 329 · cited 1×
“The interaction of AI and CyberSecurity was discussed by 426 the author in [42].”
A decade of social bot detection
Cresci, S. (2020) · Communications of the ACM · doi:10.1145/3409116 · Cited by 323 · cited 1×
“Since they are 1276 automated, they work considerably more quickly than actual 1277 individuals [182].”
BackgroundInterpretML: A Unified Framework for Machine Learning Interpretability
Nori, H., Jenkins, S., Koch, P., & Caruana, R. (2019) · arXiv · doi:10.48550/arxiv.1909.09223 · Cited by 322 · cited 1×
“The last analyzed work is [173], where the authors use LIME and Explainable Boosting Machine (EBM) [174].”
MethodIslam, M. R., Ahmed, M. U., Barua, S., & Begum, S. (2022) · Applied Sciences · doi:10.3390/app12031353 · Cited by 311 · cited 1×
“In [24] are examined and presented several XAI approaches, validation measures, and the types of explana-360 tions that can be generated to improve the acceptance of expert systems among general users.”
BackgroundPerformance Comparison and Current Challenges of Using Machine Learning Techniques in Cybersecurity
Shaukat, K., Luo, S., Varadharajan, V., Hameed, I., Chen, S., Liu, D., & Li, J. (2020) · Energies · doi:10.3390/en13102509 · Cited by 303 · cited 1×
“Shaukat et al. [52] examined the performance of various ML algorithms in terms of time complexity for identifying Cyber-attacks.”
BackgroundMicrosoft Malware Classification ChallengePreprint
Ronen, R., Radu, M., Feuerstein, C., et al. (2018) · arXiv (Cornell University) · doi:10.48550/arxiv.1802.10135 · Cited by 287
LEMNA: Explaining Deep Learning based Security Applications
Guo, W., Mu, D., Xu, J., Su, P., Wang, G., & Xing, X. (2018) · Proceedings of the 2018 ACM SIGSAC Conference on Computer and Communications Security · doi:10.1145/3243734.3243792 · Cited by 287
Microsoft Malware Classification Challenge
Ronen, R., Radu, M., Feuerstein, C., Yom‐Tov, E., & Ahmadi, M. (2018) · arXiv (Cornell University) · doi:10.13140/rg.2.2.34695.91045 · Cited by 286
Faris, H., Al-Zoubi, A. M., Heidari, A. A., Aljarah, I., Mafarja, M., Hassonah, M. A., & Fujita, H. (2019) · Information Fusion · doi:10.1016/j.inffus.2018.08.002 · Cited by 270
Deep Learning-Based Intrusion Detection With Adversaries
Wang, Z. (2018) · IEEE Access · doi:10.1109/access.2018.2854599 · Cited by 269 · cited 1×
“Swarm optimization algorithm, similar to the works in [81] 658”
MethodExplainable Artificial Intelligence: a Systematic Review
Vilone, G., & Longo, L. (2020) · arXiv · doi:10.48550/arxiv.2006.00093 · Cited by 269
Four principles of explainable artificial intelligence
Phillips, P. J., Hahn, C. A., Fontana, P. C., Yates, A. N., Greene, K., Broniatowski, D. A., & Przybocki, M. A. (2021) · doi:10.6028/nist.ir.8312 · Cited by 262
Trusting artificial intelligence in cybersecurity is a double-edged sword
Taddeo, M., McCutcheon, T., & Floridi, L. (2019) · Nature Machine Intelligence · doi:10.1038/s42256-019-0109-1 · Cited by 256
A New Intrusion Detection System Based on Fast Learning Network and Particle Swarm Optimization
Ali, M. H., Al Mohammed, B. A. D., Ismail, A., & Zolkipli, M. F. (2018) · IEEE Access · doi:10.1109/access.2018.2820092 · Cited by 248
DALEX: Explainers for Complex Predictive Models in R
Biecek, P. (2020) · Zenodo (CERN European Organization for Nuclear Research) · doi:10.5281/zenodo.3670939 · Cited by 247
Analysis of ResNet and GoogleNet models for malware detection
Khan, R. U., Zhang, X., & Kumar, R. (2019) · Journal of Computer Virology and Hacking Techniques · doi:10.1007/s11416-018-0324-z · Cited by 245
Using convolutional neural networks for classification of malware represented as images
Gibert, D., Mateu, C., Planes, J., & Vicens, R. (2019) · Journal of Computer Virology and Hacking Techniques · doi:10.1007/s11416-018-0323-0 · Cited by 243
Rawal, A., McCoy, J., Rawat, D. B., Sadler, B. M., & Amant, R. S. (2022) · IEEE Transactions on Artificial Intelligence · doi:10.1109/tai.2021.3133846 · Cited by 239 · cited 2×
“AI and 423 ML play a substantial role in the protection of computer 424 systems [13], [38], [39], [40], [41].”
BackgroundPhishpedia: A Hybrid Deep Learning Based Approach to Visually Identify Phishing Webpages
Lin, Y., Liu, R., Divakaran, D. M., Ng, J. Y., Chan, Q. Z., Lu, Y., Si, Y., Zhang, F., & Dong, J. S. (2021) · Griffith Research Online · Cited by 239
Effective Feature Extraction via Stacked Sparse Autoencoder to Improve Intrusion Detection System
Yan, B., & Han, G. (2018) · IEEE Access · doi:10.1109/access.2018.2858277 · Cited by 236
Le, T.-T.-H., Kim, H., Kang, H., & Kim, H. (2022) · Sensors · doi:10.3390/s22031154 · Cited by 208
A Memory-Based Approach to Anti-Spam Filtering for Mailing Lists
Sakkis, G., Androutsopoulos, I., Paliouras, G., Karkaletsis, V., Spyropoulos, C. D., & Stamatopoulos, P. (2003) · Information Retrieval · doi:10.1023/a:1022948414856 · Cited by 207
Explanation-Guided Backdoor Poisoning Attacks Against Malware ClassifiersPreprint
Severi, G., Meyer, J., Coull, S. E., & Oprea, A. (2020) · arXiv (Cornell University) · doi:10.48550/arxiv.2003.01031 · Cited by 205
Deep learning at the shallow end: Malware classification for non-domain experts
Le, Q., Boydell, O., Mac Namee, B., & Scanlon, M. (2018) · Digital Investigation · doi:10.1016/j.diin.2018.04.024 · Cited by 189
Yang, Y., Zheng, K., Wu, B., Yang, Y., & Wang, X. (2020) · IEEE Access · doi:10.1109/access.2020.2977007 · Cited by 185
Gumusbas, D., Yldrm, T., Genovese, A., & Scotti, F. (2021) · IEEE Systems Journal · doi:10.1109/jsyst.2020.2992966 · Cited by 182 · cited 1×
“In the sphere of CyberSecurity, researchers apply DL techniques for a variety of applications such as detecting network intrusions, malware traffic detec-471 tion and classification, and so on, as analyzed extensively in [55], [56], [57], and [58].”
MethodLocal Rule-Based Explanations of Black Box Decision Systems
Guidotti, R., Monreale, A., Ruggieri, S., Pedreschi, D., Turini, F., & Giannotti, F. (2018) · arXiv (Cornell University) · doi:10.48550/arxiv.1805.10820 · Cited by 179
An Explainable AI-Based Intrusion Detection System for DNS Over HTTPS (DoH) Attacks
Zebin, T., Rezvy, S., & Luo, Y. (2022) · IEEE Transactions on Information Forensics and Security · doi:10.1109/tifs.2022.3183390 · Cited by 171
Spam detection in social media using convolutional and long short term memory neural network
Jain, G., Шарма, М., & Agarwal, B. (2019) · Annals of Mathematics and Artificial Intelligence · doi:10.1007/s10472-018-9612-z · Cited by 169
Extensible Android Malware Detection and Family Classification Using Network-Flows and API-Calls
Taheri, L., Kadir, A. F. A., & Lashkari, A. H. (2019) · 2019 International Carnahan Conference on Security Technology (ICCST) · doi:10.1109/ccst.2019.8888430 · Cited by 166
GEE: A Gradient-based Explainable Variational Autoencoder for Network Anomaly Detection
Nguyen, Q. P., Lim, K. W., Divakaran, D. M., Low, K. H., & Chan, M. C. (2019) · 2019 IEEE Conference on Communications and Network Security (CNS) · doi:10.1109/cns.2019.8802833 · Cited by 165 · cited 1×
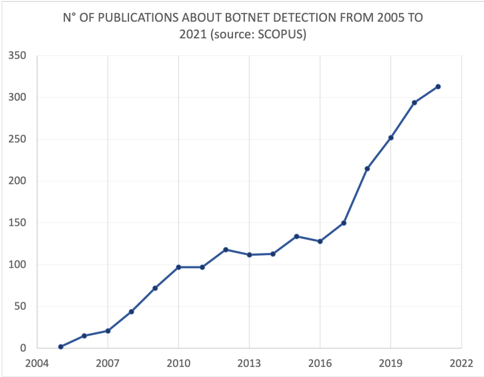
“Reference [199], [200], [201], three explainable studies focused on DGA-based botnet detection, are also worth mentioning, as is [202], in which the authors created a Gradient-based Explainable Variational Autoencoder for Net-1374 work Anomaly Detection utilizing a BotNet dataset as a test.”
MethodRTbust: Exploiting Temporal Patterns for Botnet Detection on Twitter
Mazza, M., Cresci, S., Avvenuti, M., Quattrociocchi, W., & Tesconi, M. (2019) · Proceedings of the 10th ACM Conference on Web Science · doi:10.1145/3292522.3326015 · Cited by 163 · cited 1×
“1339 In [189], the authors point out one of their proposal’s main 1340 cons, the framework’s non-Explainability.”
BackgroundMulti-Channel Deep Feature Learning for Intrusion Detection
Andresini, G., Appice, A., Mauro, N. D., Loglisci, C. A. A. M. D., & Malerba, D. (2020) · IEEE Access · doi:10.1109/access.2020.2980937 · Cited by 162 · cited 1×
“of Neural Networks [83], [84] and Adversarial Methods [85], 660 [86], [87].”
BackgroundWeb Phishing Detection Using a Deep Learning Framework
Yi, P., Guan, Y., Zou, F., Yao, Y., Wang, W., & Zhu, T. (2018) · Wireless Communications and Mobile Computing · doi:10.1155/2018/4678746 · Cited by 161 · cited 1×
“In [157], Yerima et al. propose an approach based on a Convolutional Neural Network tested on a dataset obtained from 6, 157 genuine and 4, 898 phishing websites; a small dataset instead is used in [158] where the authors introduce a Deep Belief Network (DBN).”
MethodLR-HIDS: logistic regression host-based intrusion detection system for cloud environments
Besharati, E., Naderan, M., & Namjoo, E. (2019) · Journal of Ambient Intelligence and Humanized Computing · doi:10.1007/s12652-018-1093-8 · Cited by 161
An Adversarial Approach for Explainable AI in Intrusion Detection Systems
Marino, D. L., Wickramasinghe, C. S., & Manic, M. (2018) · IECON 2018 - 44th Annual Conference of the IEEE Industrial Electronics Society · doi:10.1109/iecon.2018.8591457 · Cited by 159
DeepAM: a heterogeneous deep learning framework for intelligent malware detection
Ye, Y., Chen, L., Hou, S., Hardy, W., & Li, X. (2017) · Knowledge and Information Systems · doi:10.1007/s10115-017-1058-9 · Cited by 155 · cited 1×
“In [132] and [133] satisfying results are obtained using ML and DL techniques.”
MethodExplaining Vulnerabilities of Deep Learning to Adversarial Malware BinariesPreprint
Demetrio, L., Biggio, B., Lagorio, G., Roli, F., & Armando, A. (2019) · arXiv (Cornell University) · doi:10.48550/arxiv.1901.03583 · Cited by 153 · cited 1×
“The authors in [150] discovered that MalConv neural network does not learn any useful characteristics for malware detection from the data and text sections of executable files but instead has a tendency to learn to distinguish between benign and mali-1030 cious samples based on the characteristics…”
BackgroundClassification of Explainable Artificial Intelligence Methods through Their Output Formats
Vilone, G., & Longo, L. (2021) · Machine Learning and Knowledge Extraction · doi:10.3390/make3030032 · Cited by 152 · cited 1×
“389 The stages are ante-hoc and post-hoc, according to Vilone 390 and Longo [31], [32].”
MethodHan, W., Xue, J., Wang, Y., Huang, L., Kong, Z., & Mao, L. (2019) · Computers & Security · doi:10.1016/j.cose.2019.02.007 · Cited by 151 · cited 1×
“MalDAE [149] is a framework that explores the dif-1015 ference and relation between the dynamic and static API call sequences, which are correlated and fused by seman-1017 tics mapping.”
BackgroundTRUST XAI: Model-Agnostic Explanations for AI With a Case Study on IIoT Security
Zolanvari, M., Yang, Z., Khan, K., Jain, R., & Meskin, N. (2023) · IEEE Internet of Things Journal · doi:10.1109/jiot.2021.3122019 · Cited by 148 · cited 1×
“In conclusion, this work mentions [109], where an explain-793 able automotive intrusion detection system is proposed, 794 and [110] where a new general method is presented and tested 795 on an IDS dataset.”
MethodAn Intrusion Detection Method Using Few-Shot Learning
Yu, Y., & Bian, N. (2020) · IEEE Access · doi:10.1109/access.2020.2980136 · Cited by 147
Artificial Intelligence for Cybersecurity: A Systematic Mapping of Literature
Wiafe, I., Koranteng, F. N., Obeng, E. N., Assyne, N., Wiafe, A., & Gulliver, S. R. (2020) · IEEE Access · doi:10.1109/access.2020.3013145 · Cited by 145 · cited 1×
“AI and 423 ML play a substantial role in the protection of computer 424 systems [13], [38], [39], [40], [41].”
BackgroundHost Based Intrusion Detection System with Combined CNN/RNN Model
Chawla, A., Lee, B., Fallon, S., & Jacob, P. (2019) · Lecture Notes in Computer Science · doi:10.1007/978-3-030-13453-2_12 · Cited by 144
Explanations based on the Missing: Towards Contrastive Explanations with Pertinent Negatives
Dhurandhar, A., Chen, P., Luss, R., Tu, C., Ting, P., Shanmugam, K., & Das, P. (2018) · arXiv (Cornell University) · doi:10.48550/arxiv.1802.07623 · Cited by 144 · cited 1×
“Contrastive Explanation Method (CEM) [9] pro-227 vides explanations for classification models.”
Adversarial XAI Methods in Cybersecurity
Kuppa, A., & Le-Khac, N.-A. (2021) · IEEE Transactions on Information Forensics and Security · doi:10.1109/tifs.2021.3117075 · Cited by 141
An In-Depth Benchmarking and Evaluation of Phishing Detection Research for Security Needs
El Aassal, A., Baki, S., Das, A., & Verma, R. M. (2020) · IEEE Access · doi:10.1109/access.2020.2969780 · Cited by 140 · cited 1×
“1145 The last work to be highlighted for Phishing Detection is 1146 PhishBench [161], a benchmarking framework that can help 1147”
BackgroundSarhan, M., Layeghy, S., & Portmann, M. (2022) · Big Data Research · doi:10.1016/j.bdr.2022.100359 · Cited by 136
IoT Malware Network Traffic Classification using Visual Representation and Deep Learning
Bendiab, G., Shiaeles, S. N., Alruban, A., & Kolokotronis, N. (2020) · IEEE International Conference on Network Softwarization (NetSoft) · doi:10.1109/netsoft48620.2020.9165381 · Cited by 135
Explainable Artificial Intelligence for Tabular Data: A Survey
Sahakyan, M., Aung, Z., & Rahwan, T. (2021) · IEEE Access · doi:10.1109/access.2021.3116481 · Cited by 135 · cited 1×
“In [35] 408 a survey of XAI methods in deployment is made, and [36] 409 which considers the XAI for tabular data.”
BackgroundUse of Data Visualisation for Zero-Day Malware Detection
Venkatraman, S., & Alazab, M. (2018) · Security and Communication Networks · doi:10.1155/2018/1728303 · Cited by 135
Efficient Data Representation by Selecting Prototypes with Importance Weights
Gurumoorthy, K. S., Dhurandhar, A., Cecchi, G., & Aggarwal, C. (2019) · 2019 IEEE International Conference on Data Mining (ICDM) · doi:10.1109/icdm.2019.00036 · Cited by 131 · cited 1×
“The Pro-719 toDash algorithm [99] provides example-based explanations to summarize datasets and explain the predictions of an AI model.”
MethodGupta, C., Johri, I., Srinivasan, K., Hu, Y., Qaisar, S. M., & Huang, K.-Y. (2022) · Sensors · doi:10.3390/s22052017 · Cited by 131 · cited 1×
“Related to this, Gupta et al. [49] provide a thorough exam-446 ination of the various ML and DL models used in mobile 447 network electronic information Security.”
MethodMulti-level host-based intrusion detection system for Internet of things
Gassais, R., Ezzati‐Jivan, N., Fernandez, J. M., Aloise, D., & Dagenais, M. (2020) · Journal of Cloud Computing Advances Systems and Applications · doi:10.1186/s13677-020-00206-6 · Cited by 128
High Accuracy Phishing Detection Based on Convolutional Neural Networks
Yerima, S. Y., & Alzaylaee, M. K. (2020) · International Conference on Computer Applications & Information Security (ICCAIS) · doi:10.1109/iccais48893.2020.9096869 · Cited by 127 · cited 1×
“In [157], Yerima et al. propose an approach based on a Convolutional Neural Network tested on a dataset obtained from 6, 157 genuine and 4, 898 phishing websites; a small dataset instead is used in [158] where the authors introduce a Deep Belief Network (DBN).”
MethodArtificial Intelligence in the Cyber Domain: Offense and Defense
Truong, T. C., Diep, Q. B., & Zelinka, I. (2020) · Symmetry · doi:10.3390/sym12030410 · Cited by 126 · cited 1×
“The study looked, in particular, at ML, and 427 DL approaches to countering Cyber threats [43].”
BackgroundNetwork intrusion detection algorithm based on deep neural network
Jia, Y., Wang, M., & Wang, Y. (2019) · IET Information Security · doi:10.1049/iet-ifs.2018.5258 · Cited by 124
Jail-Phish: An improved search engine based phishing detection system
Rao, R. S., & Pais, A. R. (2019) · Computers & Security · doi:10.1016/j.cose.2019.02.011 · Cited by 120
Rabbani, M., Wang, Y. L., Khoshkangini, R., Jelodar, H., Zhao, R., & Hu, P. (2020) · Journal of Network and Computer Applications · doi:10.1016/j.jnca.2019.102507 · Cited by 120 · cited 1×
“Statista detected that 68.5% of In [112], the authors propose an Anomaly-based approach 870 where the system employs significant features of activ-871 ity to model normal and malicious behaviour of users in 872 Cloud-based environments.”
BackgroundInfluentialInformation security breaches due to ransomware attacks - a systematic literature review
Reshmi, T. R. (2021) · International Journal of Information Management Data Insights · doi:10.1016/j.jjimei.2021.100013 · Cited by 120 · cited 1×
“For the specific field of phishing interesting approach is defined in [61] and for ransomware attacks in [62].”
BackgroundA pipeline and comparative study of 12 machine learning models for text classification
Occhipinti, A., Rogers, L., & Angione, C. (2022) · Expert Systems with Applications · doi:10.1016/j.eswa.2022.117193 · Cited by 113 · cited 1×
“[180], [181] are two works focused on text classifica-1248 tion that use Spam datasets.”
BackgroundWhy an Android App Is Classified as Malware: Toward Malware Classification Interpretation
Wu, B., Chen, S., Gao, C., Fan, L., Liu, Y., Wen, W., & Lyu, M. R.-T. (2021) · ACM Transactions on Software Engineering and Methodology · doi:10.1145/3423096 · Cited by 111
Barushka, A., & Hájek, P. (2018) · Applied Intelligence · doi:10.1007/s10489-018-1161-y · Cited by 111 · cited 1×
“[164] propose a Spam filter integrating an 1157 N-gram tf-idf feature selection, a modified distribution-based 1158”
MethodAn improved two-hidden-layer extreme learning machine for malware hunting
Jahromi, A. N., Hashemi, S., Dehghantanha, A., Choo, K. R., Karimipour, H., Newton, D. E., & Parizi, R. M. (2019) · Computers & Security · doi:10.1016/j.cose.2019.101655 · Cited by 110 · cited 1×
“Similar are the works in [113] 873 and [114] where extreme surveillance through malware hunt-874 A Hybrid-based approach method is proposed in [125] where the framework use more than one complementary filter and a wrapper feature selection approach to identify the most significant runtime behavioural…”
ResultCryptomining Detection in Container Clouds Using System Calls and Explainable Machine Learning
Karn, R. R., Kudva, P., Huang, H., Suneja, S., & Elfadel, I. M. (2021) · IEEE Transactions on Parallel and Distributed Systems · doi:10.1109/tpds.2020.3029088 · Cited by 108
Towards an interpretable deep learning model for mobile malware detection and family identification
Iadarola, G., Martinelli, F., Mercaldo, F., & Santone, A. (2021) · Computers & Security · doi:10.1016/j.cose.2021.102198 · Cited by 105
Malware Detection Based on Deep Learning of Behavior Graphs
Xiao, F., Lin, Z., Sun, Y., & Ma, Y. (2019) · Mathematical Problems in Engineering · doi:10.1155/2019/8195395 · Cited by 104
DeNNeS: deep embedded neural network expert system for detecting cyber attacks
Mahdavifar, S., & Ghorbani, A. A. (2020) · Neural Computing and Applications · doi:10.1007/s00521-020-04830-w · Cited by 104 · cited 1×
“Two works where the goal is not Phishing detection, but a dataset of this type is used for tests are [170], [171].”
BackgroundIntelligent malware detection based on graph convolutional network
Li, S., Zhou, Q., Zhou, R., & Lv, Q. (2021) · The Journal of Supercomputing · doi:10.1007/s11227-021-04020-y · Cited by 104
Liu, H., Zhong, C., Alnusair, A., & Islam, S. R. (2021) · Journal of Network and Systems Management · doi:10.1007/s10922-021-09606-8 · Cited by 103 · cited 1×
“FAIXID [96] is a new proposed framework that uses data cleaning techniques.”
MethodDeep Learning for Android Malware Defenses: A Systematic Literature Review
Liu, Y., Tantithamthavorn, C., Li, L., & Liu, Y. (2023) · ACM Computing Surveys · doi:10.1145/3544968 · Cited by 101 · cited 1×
“Indeed, [68] 509 focuses on Android Malware Defenses and XAI applications 510 in this field; they point out that nine out of ten primary sources 511 are proposed after 2019, indicating that Explainable Deep 512 Learning approaches for malware defenses are a current hot 513 research topic.”
BackgroundZhu, E., Ju, Y.-Y., Chen, Z., Liu, F., & Fang, X. (2020) · Applied Soft Computing · doi:10.1016/j.asoc.2020.106505 · Cited by 101
Detection of Advanced Malware by Machine Learning Techniques
Sharma, S., Krishna, C. R., & Sahay, S. K. (2018) · Advances in intelligent systems and computing · doi:10.1007/978-981-13-0589-4_31 · Cited by 99
Data augmentation based malware detection using convolutional neural networks
Çatak, F. Ö., Ahmed, J., Şahinbaş, K., & Khand, Z. H. (2021) · PeerJ Computer Science · doi:10.7717/peerj-cs.346 · Cited by 95
Explainable Unsupervised Machine Learning for Cyber-Physical Systems
Wickramasinghe, C. S., Amarasinghe, K., Marino, D., Rieger, C. G., & Manic, M. (2021) · IEEE Access · doi:10.1109/access.2021.3112397 · Cited by 94 · cited 1×
“Wickramasinghe et al. [219] propose a Desiderata on Explainability of unsupervised approaches in Cyber-Physical Systems since they generate a large amount of unlabeled data.”
BackgroundEfficient spam and phishing emails filtering based on deep learning
Magdy, S., Abouelseoud, Y., & Mikhail, M. (2022) · Computer Networks · doi:10.1016/j.comnet.2022.108826 · Cited by 94
Classifying Spam Emails Using Text and Readability Features
Shams, R., & Mercer, R. E. (2013) · Proceedings · doi:10.1109/icdm.2013.131 · Cited by 92
Robust Botnet DGA Detection: Blending XAI and OSINT for Cyber Threat Intelligence Sharing
Suryotrisongko, H., Musashi, Y., Tsuneda, A., & Sugitani, K. (2022) · IEEE Access · doi:10.1109/access.2022.3162588 · Cited by 90 · cited 1×
“Suryotrisongko et al. [194] propose the XAI and OSINT combination for Cyber Threat Intelligence Sharing in pre-1359 venting Botnet DGA.”
BackgroundD., A., K.A., V. K., S., S. C., & P., V. (2019) · Computer Communications · doi:10.1016/j.comcom.2019.08.003 · Cited by 88
Towards Explainable CNNs for Android Malware Detection
Kinkead, M., Millar, S., McLaughlin, N., & O’Kane, P. (2021) · Procedia Computer Science · doi:10.1016/j.procs.2021.03.118 · Cited by 88
Gotcha - Sly Malware!: Scorpion A Metagraph2vec Based Malware Detection System
Fan, Y., Hou, S., Zhang, Y., Ye, Y., & Abdulhayoglu, M. (2018) · Proceedings of the 24th ACM SIGKDD International Conference on Knowledge Discovery & Data Mining · doi:10.1145/3219819.3219862 · Cited by 86
A Fuzzy Logic based feature engineering approach for Botnet detection using ANN
Joshi, C., Ranjan, R. K., & Bharti, V. (2021) · Journal of King Saud University - Computer and Information Sciences · doi:10.1016/j.jksuci.2021.06.018 · Cited by 85 · cited 1×
“Other interesting works are [190], [191].”
A Survey on Machine-Learning Based Security Design for Cyber-Physical Systems
Kim, S., & Park, K. (2021) · Applied Sciences · doi:10.3390/app11125458 · Cited by 83 · cited 1×
“Kim and Park [54] focus the attention on ML in Cyber-Physical Systems (CPS), which is the integration of a physical system into the real world and control applications in a computing system, interacting through a communica-466 tions network.”
BackgroundEXPLAIN-IT: Towards Explainable AI for Unsupervised Network Traffic Analysis
Morichetta, A., Casas, P., & Mellia, M. (2019) · Proceedings of the 3rd ACM CoNEXT Workshop on Big DAta, Machine Learning and Artificial Intelligence for Data Communication Networks · doi:10.1145/3359992.3366639 · Cited by 82
BotStop : Packet-based efficient and explainable IoT botnet detection using machine learning
Alani, M. M. (2022) · Computer Communications · doi:10.1016/j.comcom.2022.06.039 · Cited by 79 · cited 1×
“BotStop [192] is a Packet-based Botnet detection system that examines incoming and outgoing network traffic in an IoT device to prevent infections from Botnets.”
BackgroundROULETTE: A neural attention multi-output model for explainable Network Intrusion Detection
Andresini, G., Appice, A., Caforio, F. P., Malerba, D., & Vessio, G. (2022) · Expert Systems with Applications · doi:10.1016/j.eswa.2022.117144 · Cited by 78
Provenance documentation to enable explainable and trustworthy AI: A literature review
Kale, A., Nguyen, T., Harris, F. C., Li, C., Zhang, J., & Ma, X. (2023) · Data Intelligence · doi:10.1162/dint_a_00119 · Cited by 77 · cited 1×
“It is essential to min-309 imize potential biases (e.g., algorithmic, racial, ideological and gender biases) during the ethical AI solution development stage [14], [15]. extremely particular object components to improve the inter-338 pretability of traditional CNNs.”
BackgroundMultiple instance learning for malware classification
Stiborek, J., Pevný, T., & Řehák, M. (2017) · Expert Systems with Applications · doi:10.1016/j.eswa.2017.10.036 · Cited by 77
Convolutional neural networks and extreme learning machines for malware classification
Jain, M., Andreopoulos, W., & Stamp, M. (2020) · Journal of Computer Virology and Hacking Techniques · doi:10.1007/s11416-020-00354-y · Cited by 75
IoT botnet detection via power consumption modeling
Jung, W., Zhao, H., Sun, M., & Zhou, G. (2020) · Smart Health · doi:10.1016/j.smhl.2019.100103 · Cited by 74
Towards Self-Explainable Cyber-Physical Systems
Blumreiter, M., Greenyer, J., Garcia, F. J. C., Klös, V., Schwammberger, M., Sommer, C., Vogelsang, A., & Wortmann, A. (2019) · ACM/IEEE International Conference on Model Driven Engineering Languages and Systems Companion (MODELS-C) · doi:10.1109/models-c.2019.00084 · Cited by 72 · cited 1×
“An Explainable Cyber-Physical Systems based on Knowl-1489 edge Graph is proposed in [220] for Energy Systems while in [221] the authors propose a framework to build Self-1491 Explainable Cyber-Physical System.”
BackgroundVigano, L., & Magazzeni, D. (2020) · 2020 IEEE European Symposium on Security and Privacy Workshops (EuroS&PW) · doi:10.1109/eurospw51379.2020.00045 · Cited by 69 · cited 1×
“In [66] Vigano et al. presented Explainable Security (XSec), 504 a new security paradigm that involves several different stake-505 holders and is multifaceted by nature.”
BackgroundKebede, T. M., Djaneye-Boundjou, O., Narayanan, B. N., Ralescu, A., & Kapp, D. (2017) · IEEE National Aerospace and Electronics Conference (NAECON) · doi:10.1109/naecon.2017.8268747 · Cited by 67
Explainable artificial intelligence for digital forensics
Hall, S. W., Sakzad, A., & Choo, K. R. (2022) · WIREs Forensic Science · doi:10.1002/wfs2.1434 · Cited by 66
Can We Trust Your Explanations? Sanity Checks for Interpreters in Android Malware Analysis
Fan, M., Wei, W., Xie, X., Liu, Y., Guan, X., & Liu, T. (2021) · IEEE Transactions on Information Forensics and Security · doi:10.1109/tifs.2020.3021924 · Cited by 65 · cited 1×
“To conclude the section, it is necessary to analyze the work of Fan et al. [154].”
MethodAchieving Explainability of Intrusion Detection System by Hybrid Oracle-Explainer Approach
Szczepanski, M., Choras, M., Pawlicki, M., & Kozik, R. (2020) · 2020 International Joint Conference on Neural Networks (IJCNN) · doi:10.1109/ijcnn48605.2020.9207199 · Cited by 64
PSI-rooted subgraph: A novel feature for IoT botnet detection using classifier algorithms
Nguyen, H., Ngo, Q.-D., Nguyen, D.-H., & Le, V.-H. (2020) · ICT Express · doi:10.1016/j.icte.2019.12.001 · Cited by 62
Explaining Black-box Android Malware Detection
Melis, M., Maiorca, D., Biggio, B., Giacinto, G., & Roli, F. (2018) · European Signal Processing Conference (EUSIPCO) · doi:10.23919/eusipco.2018.8553598 · Cited by 61
Enabling Dynamic Network Access Control with Anomaly-based IDS and SDN
Li, H., Feng, W. Q., & Hu, H. (2019) · ACM International Workshop on Security in Software Defined Networks & Network Function Virtualization (SDN-NFV Sec) · doi:10.1145/3309194.3309199 · Cited by 61 · cited 1×
“The work proposed in [100] defines a method to make rules for accessing the network dynamically and not statically as, for example, the rules set in a firewall may be.”
MethodHybrid Email Spam Detection Model Using Artificial Intelligence
Douzi, S., AlShahwan, F. A., Lemoudden, M., & Ouahidi, B. E. (2020) · International Journal of Machine Learning and Computing · doi:10.18178/ijmlc.2020.10.2.937 · Cited by 61
Explaining Network Intrusion Detection System Using Explainable AI Framework
Mane, S., & Rao, D. J. (2021) · arXiv (Cornell University) · doi:10.48550/arxiv.2103.07110 · Cited by 60
Host-Based Intrusion Detection Model Using Siamese Network
Park, D., Kim, S. S., Kwon, H.-J., Shin, D., & Shin, D. (2021) · IEEE Access · doi:10.1109/access.2021.3082160 · Cited by 60
Adversarial Attacks in Explainable Machine Learning: A Survey of Threats Against Models and Humans
Vadillo, J., Santana, R., & Lozano, J. A. (2024) · Wiley Interdisciplinary Reviews Data Mining and Knowledge Discovery · doi:10.1002/widm.1567 · Cited by 59
XAI for Cybersecurity: State of the Art, Challenges, Open Issues and Future Directions
Srivastava, G., Jhaveri, R. H., Bhattacharya, S., Pandya, S., Rajeswari, Maddikunta, P. K. R., Yenduri, G., Hall, J. G., Alazab, M., & Gadekallu, T. R. (2022) · arXiv (Cornell University) · doi:10.48550/arxiv.2206.03585 · Cited by 58 · cited 2×
“Currently, only two work focus exclusively on this area, which are [63], [64].”
BackgroundDynamic API call sequence visualisation for malware classification
Tang, M., & Qian, Q. (2018) · IET Information Security · doi:10.1049/iet-ifs.2018.5268 · Cited by 58
Rallying Adversarial Techniques against Deep Learning for Network Security
Clements, J., Yang, Y., Sharma, A. A., Hu, H., & Lao, Y. (2021) · 2021 IEEE Symposium Series on Computational Intelligence (SSCI) · doi:10.1109/ssci50451.2021.9660011 · Cited by 58
Memory-Efficient Deep Learning for Botnet Attack Detection in IoT Networks
Popoola, S. I., Adebisi, B., Ande, R., Hammoudeh, M. A. A., & Atayero, A. A. A. (2021) · Electronics · doi:10.3390/electronics10091104 · Cited by 57
Artificial Intelligence and Problems of Ensuring Cyber Security
Khisamova, Z. I., Begishev, I. R., & Sidorenko, E. L. (2019) · International journal of cyber criminology · Cited by 56
A Machine Learning Based Two-Stage Wi-Fi Network Intrusion Detection System
Reyes-Angulo, A. A., Vaca, F. D., Aguayo, G. A. C., Niyaz, Q., & Devabhaktuni, V. (2020) · Electronics · doi:10.3390/electronics9101689 · Cited by 56
Anomaly Detection for Cyber-Security Based on Convolution Neural Network : A survey
Alabadi, M., & Celik, Y. (2020) · 2020 International Congress on Human-Computer Interaction, Optimization and Robotic Applications (HORA) · doi:10.1109/hora49412.2020.9152899 · Cited by 55 · cited 1×
“Alabadi and Celik in [53] presented a comprehensive sur-461 vey about using CNN as a key solution for anomaly detection.”
MethodASSCA: API sequence and statistics features combined architecture for malware detection
Lu, X., Fangshuo, J., Xiao, Z., Yi, S., Sha, J. J., & Lió, P. (2019) · Computer Networks · doi:10.1016/j.comnet.2019.04.007 · Cited by 55
Le, T., Wang, S., & Lee, D. (2020) · Proceedings of the 26th ACM SIGKDD International Conference on Knowledge Discovery & Data Mining · doi:10.1145/3394486.3403066 · Cited by 54 · cited 1×
“GRACE [178] generates contrastive samples that are concise, informative and faithful to the neural network model’s specific prediction.”
BackgroundExplainable Artificial Intelligence in Cybersecurity: A Brief Review
Hariharan, S., Velicheti, A., Anagha, A. S., Thomas, C., & Balakrishnan, N. (2021) · doi:10.1109/isea-isap54304.2021.9689765 · Cited by 54 · cited 2×
“However, it must be pointed out that in [63], the authors 490 provide a quick overview and, above all, do not pay attention 491 on the different applications within CyberSecurity.”
BackgroundDetection and Classification of Botnet Traffic using Deep Learning with Model Explanation
Kundu, P. P., Truong-Huu, T., Chen, L., Zhou, L., & Teo, S. G. (2024) · IEEE Transactions on Dependable and Secure Computing · doi:10.1109/tdsc.2022.3183361 · Cited by 52
Analysis and classification of context-based malware behavior
Alaeiyan, M., Parsa, S. A., & Conti, M. (2019) · Computer Communications · doi:10.1016/j.comcom.2019.01.003 · Cited by 52
Nahmias, D., Cohen, A., Nissim, N., & Elovici, Y. (2020) · Neural Networks · doi:10.1016/j.neunet.2020.01.003 · Cited by 50
A Survey on Botnets, Issues, Threats, Methods, Detection and Prevention
Owen, H., Zarrin, J., & Pour, S. M. (2022) · Journal of Cybersecurity and Privacy · doi:10.3390/jcp2010006 · Cited by 49 · cited 1×
“Most of the time, users are unaware that 1297 their devices are part of a Botnet and are under the control of 1298 online criminals [183].”
BackgroundBoolean Decision Rules via Column Generation
Dash, S., Günlük, O., & Wei, D. (2018) · arXiv (Cornell University) · doi:10.48550/arxiv.1805.09901 · Cited by 49 · cited 1×
“They use the Boolean Rule Column Generation (BRCG) algorithm [97], which pro-715 vides a directly interpretable supervised learning method for binary classification.”
MethodA hybrid-multi filter-wrapper framework to identify run-time behaviour for fast malware detection
Huda, S., Islam, R., Abawajy, J., Yearwood, J. L., Hassan, M. M., & Fortino, G. (2018) · Future Generation Computer Systems · doi:10.1016/j.future.2017.12.037 · Cited by 48 · cited 1×
“Similar are the works in [113] 873 and [114] where extreme surveillance through malware hunt-874 A Hybrid-based approach method is proposed in [125] where the framework use more than one complementary filter and a wrapper feature selection approach to identify the most significant runtime behavioural…”
ResultImproving User Trust on Deep Neural Networks Based Intrusion Detection Systems
Amarasinghe, K., & Manic, M. (2018) · Annual Conference of the IEEE Industrial Electronics Society (IECON) · doi:10.1109/iecon.2018.8591322 · Cited by 47 · cited 1×
“The aim in [102] is to increase transparency in an IDS based on a Deep Neural Network.”
MethodAn Explainable Multi-Modal Hierarchical Attention Model for Developing Phishing Threat Intelligence
Chai, Y., Zhou, Y., Li, W., & Jiang, Y. (2021) · IEEE Transactions on Dependable and Secure Computing · doi:10.1109/tdsc.2021.3119323 · Cited by 46 · cited 1×
“Two works where the goal is not Phishing detection, but a dataset of this type is used for tests are [170], [171].”
Background(2020) · doi:10.14778/3494124.3494128 · Cited by 46
Bot-Detective: An explainable Twitter bot detection service with crowdsourcing functionalities
Kouvela, M., Dimitriadis, I., & Vakali, A. I. (2020) · International Conference on Management of Emergent Digital EcoSystems (MEDES) · doi:10.1145/3415958.3433075 · Cited by 45 · cited 1×
“Bot-Detective [203] is an explainable Twitter bot detection service with crowdsourcing functionalities that uses LIME.”
BackgroundHardware-Assisted Malware Detection and Localization using Explainable Machine Learning
Pan, Z., Sheldon, J., & Mishra, P. (2022) · IEEE Transactions on Computers · doi:10.1109/tc.2022.3150573 · Cited by 45 · cited 1×
“[144], [145] in two related works propose a 988 hardware-assisted malware detection framework developing 989 a regression-based Explainable Machine Learning algorithm.”
BackgroundA Fog-Augmented Machine Learning based SMS Spam Detection and Classification System
Busaeed, S., Katib, I. A., & Mehmood, R. (2020) · International Conference on Fog and Mobile Edge Computing (FMEC) · doi:10.1109/fmec49853.2020.9144833 · Cited by 43
Explaining AI for Malware Detection: Analysis of Mechanisms of MalConv
Bose, S., Barao, T., & Liu, X. (2020) · International Joint Conference on Neural Networks (IJCNN) · doi:10.1109/ijcnn48605.2020.9207322 · Cited by 43 · cited 1×
“The backtracking method selects the most important features VOLUME 10, 2022 explains the outcomes of deep networks in real-world test-995 ing, the authors of [146] propose a framework that interpo-996 lates between samples of different classes at different layers.”
MethodReview of Cybersecurity Research Topics, Taxonomy and Challenges: Interdisciplinary Perspective
Suryotrisongko, H., & Musashi, Y. (2019) · IEEE International Conference on Service-Oriented Computing and Applications (SOCA) · doi:10.1109/soca.2019.00031 · Cited by 42 · cited 1×
“AI and 423 ML play a substantial role in the protection of computer 424 systems [13], [38], [39], [40], [41].”
BackgroundFast-flux hunter: a system for filtering online fast-flux botnet
Almomani, A. (2016) · Neural Computing and Applications · doi:10.1007/s00521-016-2531-1 · Cited by 41 · cited 1×
“1317 Fast-flux hunter (FFH) [184] is a framework that can 1318 improve the performance level in detecting and predicting 1319 unknown and Zero-day fast-flux Botnets.”
BackgroundKumar, R., & Geetha, S. (2022) · Sensors · doi:10.3390/s22072798 · Cited by 40
A Hybrid Approach for an Interpretable and Explainable Intrusion Detection System
Dias, T., Oliveira, N. R. B. D., Sousa, N., Praça, I., & Sousa, O. (2022) · Lecture notes in networks and systems · doi:10.1007/978-3-030-96308-8_96 · Cited by 39
Metamorphic malware identification using engine-specific patterns based on co-opcode graphs
Kakisim, A. G., Nar, M., & Soğukpınar, İ. (2020) · Computer Standards & Interfaces · doi:10.1016/j.csi.2020.103443 · Cited by 39 · cited 1×
“com/topics/8338/malware/dossierKeyfigures Staying on the use of graphs but moving to Signature- 890 based systems, HLES-MMI [121] is a method that iden- 891 tifies metamorphic malware families based on computing 892 the similarities among the higher-level engine signatures.”
MethodAn overview of the applications of Artificial Intelligence in Cybersecurity
Akhtar, M., & Feng, T. (2021) · EAI Endorsed Transactions on Creative Technologies · doi:10.4108/eai.23-11-2021.172218 · Cited by 39 · cited 1×
“428 There are various advantages and disadvantages to the use 429 of AI in this field, as briefly analyzed in [44] and [45], and 430 work like that done in [46], where all the existing literature 431 on the last decade is analyzed, can be of help to those who are 432 entering into the specific sector.”
BackgroundEffective and Explainable Detection of Android Malware Based on Machine Learning Algorithms
Kumar, R., Xiaosong, Z., Khan, R. U., Kumar, J., & Ahad, I. (2018) · International Conference on Computing and Artificial Intelligence (ICCAI) · doi:10.1145/3194452.3194465 · Cited by 38
Phishing Detection Using URL-based XAI Techniques
Galego Hernandes, P. R., Floret, C. P., Cardozo De Almeida, K. F., Da Silva, V. C., Papa, J. P., & Pontara Da Costa, K. A. (2021) · 2021 IEEE Symposium Series on Computational Intelligence (SSCI) · doi:10.1109/ssci50451.2021.9659981 · Cited by 38
Generalized Linear Rule ModelsPreprint
Wei, D., Dash, S., Gao, T., & Günlük, O. (2019) · arXiv (Cornell University) · doi:10.48550/arxiv.1906.01761 · Cited by 38 · cited 1×
“Logistic Rule Regression (LogRR) [98] is a directly interpretable supervised learning method that can perform logistic regression on rule-based functions.”
MethodDENAS: automated rule generation by knowledge extraction from neural networks
Chen, S., Bateni, S., Grandhi, S., Li, X., Liu, C., & Yang, W. (2020) · ACM Joint European Software Engineering Conference and Symposium on the Foundations of Software Engineering (ESEC/FSE) · doi:10.1145/3368089.3409733 · Cited by 37
Malrec: Compact Full-Trace Malware Recording for Retrospective Deep Analysis
Severi, G., Leek, T., & Dolan-Gavitt, B. (2018) · Lecture notes in computer science · doi:10.1007/978-3-319-93411-2_1 · Cited by 36
Holder, E. W., & Wang, N. (2021) · Human-Intelligent Systems Integration · doi:10.1007/s42454-020-00021-z · Cited by 35 · cited 1×
“In [242], the authors present an example and approach for creating a concept for an XAI-driven junior cyber analyst based on understanding the information needs of both humans and AI components in terms of the work context and workflow.”
MethodMahbooba, B., Sahal, R., Alosaimi, W. A., & Serrano, M. (2021) · Complexity · doi:10.1155/2021/5538896 · Cited by 35 · cited 1×
“In [111] instead, the authors emphasize the 796 importance of trust but do not use XAI methods.”
BackgroundGuerra-Manzanares, A., Nõmm, S., & Bahşi, H. (2019) · International Conference on Machine Learning and Applications · doi:10.1109/icmla.2019.00193 · Cited by 34 · cited 1×
“This latter is also used in [195] and [196] where the final goal is the detection in IoT Networks.”
BackgroundAI-Powered Honeypots for Enhanced IoT Botnet Detection
Memos, V. A., & Psannis, K. E. (2020) · World Symposium on Communication Engineering (WSCE) · doi:10.1109/wsce51339.2020.9275581 · Cited by 34
First Step Towards EXPLAINable DGA Multiclass Classification
Drichel, A., Faerber, N., & Meyer, U. (2021) · International Conference on Availability, Reliability and Security (ARES) · doi:10.1145/3465481.3465749 · Cited by 34 · cited 1×
“1370 Reference [199], [200], [201], three explainable studies 1371 focused on DGA-based botnet detection, are also worth 1372 mentioning, as is [202], in which the authors created a 1373 Gradient-based Explainable Variational Autoencoder forNet- 1374 work Anomaly Detection utilizing a BotNet dataset as a test.”
Explainable AI and Random Forest Based Reliable Intrusion Detection systemPreprint
Wali, S. W., & Khan, I. (2021) · doi:10.36227/techrxiv.17169080 · Cited by 34
Hardware-Assisted Malware Detection using Explainable Machine Learning
Pan, Z., Sheldon, J., & Mishra, P. (2020) · IEEE International Conference on Computer Design: VLSI in Computers and Processors (ICCD) · doi:10.1109/iccd50377.2020.00113 · Cited by 32
SLISEMAP: supervised dimensionality reduction through local explanations
Björklund, A., Mäkelä, J., & Puolamäki, K. (2022) · Machine Learning · doi:10.1007/s10994-022-06261-1 · Cited by 32 · cited 1×
“SLISEMAP [179] finds local Explanations for all data items and builds a (typically) two-1245 dimensional global visualization of the black box model such that data items with similar Local Explanations are projected nearby.”
Background
Research works printed but not linked: 12
- Morgan, 2020, Special report: Cyberwarfare in the C-suite
- 2020, Enisa Threat Landscape 2020—List of Top 15 Threats
- Dalave, A review on artificial intelligence in cyber security, 304
- Biswas, 2018, Intrusion detection using machine learning: A comparison study, Int. J. pure Appl. Math., 118, 101
- Tcydenova, 2021, Detection of adversarial attacks in ai-based intrusion detection systems using explainable AI, Hum.-Centric Comput. Inf. Sci., 11, 1
- 10.1109/ICCW.2019.8757060 · doi:10.1109/iccw.2019.8757060
- Yang, CADE: Detecting and explaining concept drift samples for security applications, 2327
- 10.2172/1878725 · doi:10.2172/1878725
- Khanan, JITBOT: An explainable just-in-time defect prediction bot, 1336
- Dhanabal, 2015, A study on NSL-KDD dataset for intrusion detection system based on classification algorithms, Int. J. Adv. Res. Comput. Commun. Eng., 4, 446
- Creech, 2014, Developing a high-accuracy cross platform host-based intrusion detection system capable of reliably detecting zero-day attacks
- Panigrahi, 2018, A detailed analysis of CICIDS2017 dataset for designing intrusion detection systems, Int. J. Eng. Technol., 7, 479
Cited by
Moustafa, N., Koroniotis, N., Keshk, M., Zomaya, A. Y., & Tari, Z. (2023) · IEEE Communications Surveys & Tutorials · doi:10.1109/comst.2023.3280465 · Cited by 266
Survey on Explainable AI: From Approaches, Limitations and Applications Aspects
Yang, W., Wei, Y., Wei, H., Chen, Y., Huang, G., Li, X., Li, R., Yao, N., Wang, X., Gu, X., et al. (2023) · Human-Centric Intelligent Systems · doi:10.1007/s44230-023-00038-y · Cited by 240
Mohamed, N. (2025) · Knowledge and Information Systems · doi:10.1007/s10115-025-02429-y · Cited by 208
Nwakanma, C. I., Ahakonye, L. A. C., Njoku, J. N., Odirichukwu, J. C., Okolie, S. A., Uzondu, C., Ndubuisi Nweke, C. C., & Kim, D.-S. (2023) · Applied Sciences · doi:10.3390/app13031252 · Cited by 202
Sarker, I. H., Janicke, H., Mohsin, A., Gill, A., & Maglaras, L. (2024) · ICT Express · doi:10.1016/j.icte.2024.05.007 · Cited by 188
Metadata
- Authors
- Capuano, N., Fenza, G., Loia, V., & Stanzione, C.
- Affiliations
- University of Basilicata (IT)
- University of Salerno (IT)
- Centro Alti Studi per la Difesa (CASD) (IT)
- Venue
- IEEE Access
- Published
- 2022
- Volume
- 10
- Pages
- 93575-93600
- ISSN
- 2169-3536 (ISSN-L)
- OpenAlex
- W4294691140
- Cited by
- 330
- References
- 239
- Citations by year
- 2026: 102 · 2025: 98 · 2024: 82 · 2023: 43 · 2022: 3
- FWCI
- 18.59
- Type
- journal article
- Language
- en
- Open access
- gold
- doi.org
- Locations
- IEEE Access (publishedVersion, cc-by)
- DOAJ (DOAJ: Directory of Open Access Journals) (submittedVersion, cc-by-sa)
- CINECA IRIS Institutional Research Information System (University of Basilicata) (submittedVersion)
- Topics
- Physical Sciences › Computer Science › Artificial Intelligence › Explainable Artificial Intelligence (XAI)
- Physical Sciences › Computer Science › Computer Networks and Communications › Network Security and Intrusion Detection
- Physical Sciences › Computer Science › Artificial Intelligence › Adversarial Robustness in Machine Learning
- Keywords
- explainable AI, cybersecurity, intrusion detection systems, malware detection, phishing detection, spam detection, botnet detection, fraud detection, zero-day vulnerabilities, digital forensics, cryptojacking
About these checks
Registry, retraction, Cites and statistics results are computed, not judged, with one exception: a printed reference that no index lists is read once by a model before it counts as a citation error. Claims are extracted by a model and kept only when their quote appears verbatim in the text; each cited source is then checked, with a model’s help, for whether it says what the claim relies on. Those verdicts can be wrong — read the claim’s quote and the cited source before relying on one.
Statistics and arithmetic are recomputed, not judged.
Confidence bands are shown only for fields calibrated on our annotated test set. None is calibrated yet, so no band is shown.
What counts as a claim ›How we measure confidence ›How we check this ›
Are you an author, or do you see a problem with this page? Request a review
Data sources
Bibliographic data: Semantic Scholar, OpenAlex, Crossref.
Contains information from the Semantic Scholar Academic Graph Datasets, made available under the ODC Attribution License (ODC-BY 1.0).
Semantic Scholar’s data is described in: Kinney, R., et al. (2023). The Semantic Scholar Open Data Platform. arXiv:2301.10140.
